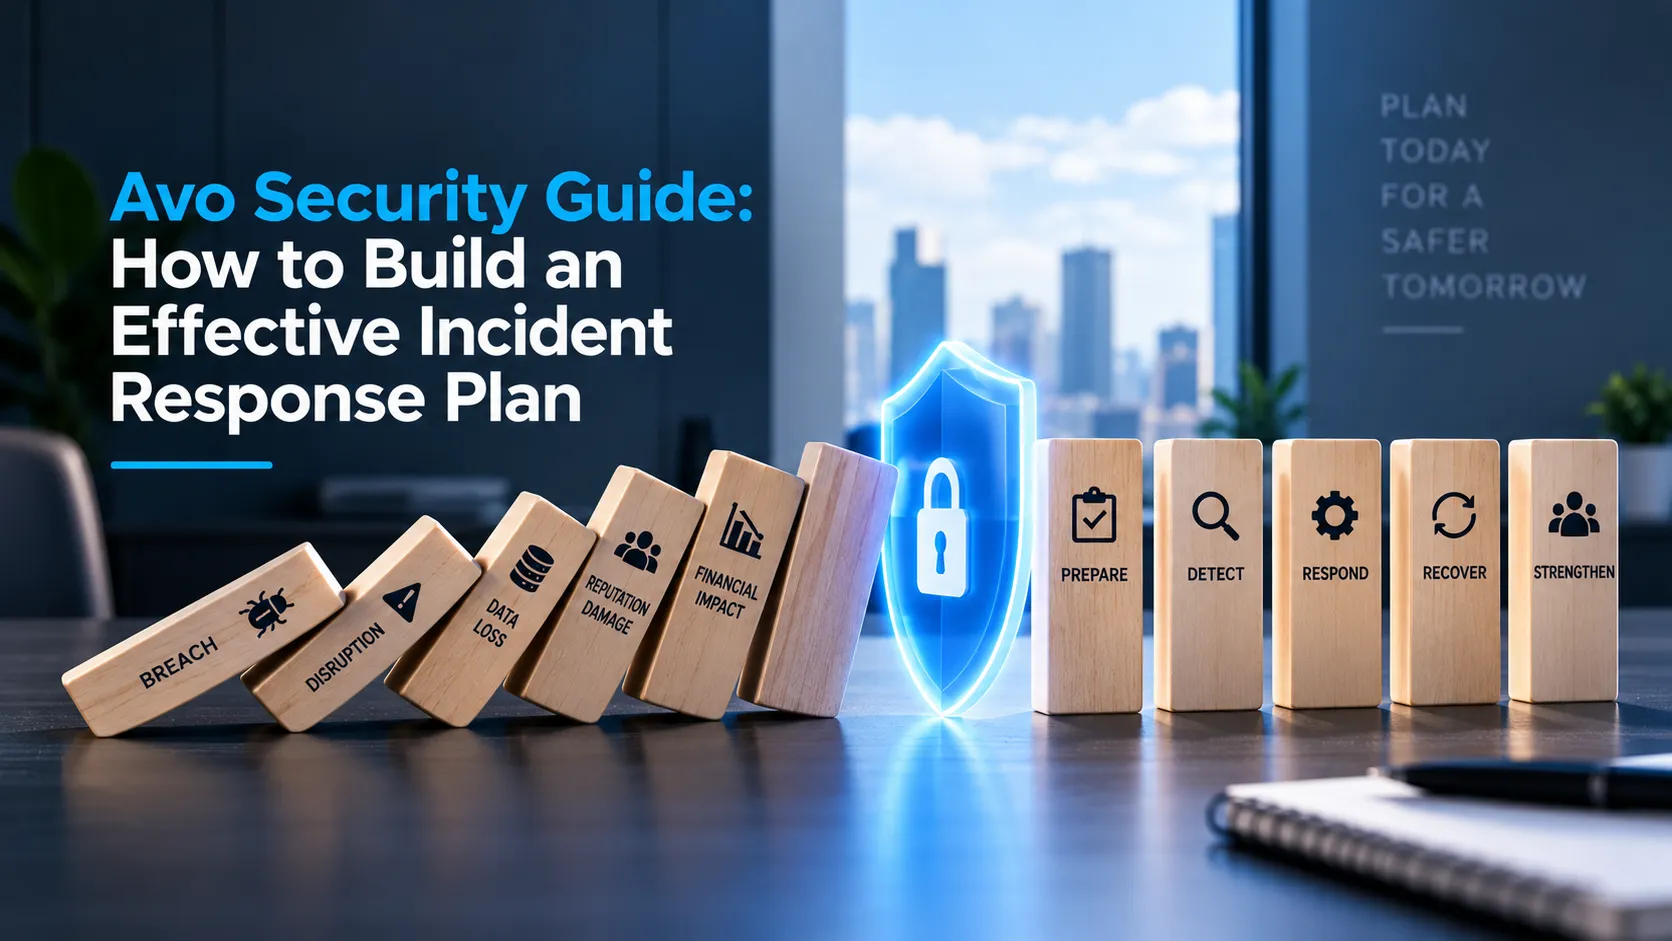

Cyberattacks rarely announce themselves in advance. A phishing email lands in an inbox, a laptop connects to an unsecured network, or a forgotten password gets leaked in a data breach somewhere else entirely. AVO Security helps businesses stay ahead of these everyday threats by providing an added layer of protection across their digital environment. By the time anyone notices an attack, the damage may already be spreading.

This is exactly why an incident response plan matters. It is not a document you write once and forget. It is a living framework that tells you, your team, or your family exactly what to do the moment something goes wrong online.
In this guide, we will walk through what an incident response plan actually is, why it matters for individuals and businesses alike, and how to build one step by step. Along the way, we will also look at the everyday tools and habits that reduce the chances of ever needing to activate that plan in the first place.
What Is an Incident Response Plan?
An incident response plan is a documented, structured approach for detecting, responding to, and recovering from a cybersecurity incident. Think of it as a fire escape plan, but for your digital environment.
A cybersecurity incident can be almost anything: a ransomware attack, a stolen password, an employee clicking a malicious link, or a data breach exposing customer information. Without a plan, the first instinct during a crisis is often panic, followed by confusion about who should do what.
A good incident response plan removes that guesswork. It defines roles, communication channels, technical steps, and recovery procedures in advance, so that when something happens, people can act quickly instead of debating what to do next.
It is worth noting that incident response plans are not just for large corporations with dedicated IT departments. Small businesses, freelancers, and even individuals managing sensitive personal data benefit from having at least a basic version of one.
Why Incident Response Planning Matters More Than Ever
The frequency and sophistication of cyber threats have increased significantly over the past decade. Attackers no longer rely solely on obvious scams; they use convincing phishing emails, fake websites, and even QR codes to trick people into giving up sensitive information.
For businesses, a delayed or poorly handled response to a security incident can mean lost revenue, damaged customer trust, and in some cases, legal consequences. Regulations like GDPR and various data protection laws around the world often require organizations to report breaches within a specific timeframe, which is impossible without a plan already in place.
For individuals, the stakes are more personal. A compromised email account can lead to identity theft, financial fraud, or someone impersonating you online. Having even a simple personal incident response checklist can help you react calmly instead of scrambling when something feels off.
The truth is, most incidents are not caused by highly advanced hacking techniques. They usually stem from simple oversights: reused passwords, unpatched software, or clicking a link without checking where it leads. This makes preparation and awareness just as important as any technical defense.
Understanding Common Types of Security Incidents
Before you can respond effectively to an incident, it helps to understand the range of situations your plan might need to cover. Security incidents come in many forms, and each type often requires a slightly different response approach.
Phishing attacks remain one of the most common entry points for larger incidents. These typically involve deceptive emails or messages designed to trick someone into revealing credentials, clicking a malicious link, or downloading malware disguised as a legitimate file.
Ransomware is another significant concern, particularly for businesses. This type of malware encrypts files and demands payment for their release. Because ransomware can spread quickly across a network, containment speed is especially critical in these cases.
Data breaches involve unauthorized access to sensitive information, whether through a hacked database, a misconfigured cloud storage bucket, or an insider improperly accessing records they shouldn't. These incidents often carry legal and regulatory implications beyond the immediate technical fix.
Account takeovers occur when someone gains unauthorized access to a personal or business account, often through a reused or weak password. This is particularly common with email accounts, since access to email can often be used to reset passwords for other connected services.
Insider threats, whether intentional or accidental, involve someone within an organization misusing their access to systems or data. These can be harder to detect because the activity often comes from a legitimate, authorized account.
Understanding these common categories helps you tailor specific response steps for each scenario, rather than relying on a single generic process that may not fit every situation equally well.
Legal and Regulatory Considerations
Depending on your location, industry, and the type of data involved, a security incident may trigger specific legal or regulatory obligations. Understanding these requirements in advance, rather than scrambling to research them during an actual incident, saves valuable time.
Many regions have data breach notification laws that require organizations to inform affected individuals and, in some cases, regulatory bodies within a specific timeframe after discovering a breach. Missing these deadlines can result in significant penalties on top of the incident itself.
Industries handling particularly sensitive information, such as healthcare or financial services, often face additional compliance requirements around how incidents must be documented, reported, and remediated. If your organization falls into one of these categories, it's worth having legal counsel review your incident response plan to ensure it aligns with applicable regulations.
Even if you are not legally required to notify anyone, being transparent with affected customers or users is often the right approach from a trust standpoint. People tend to be more forgiving of a company that handled a breach honestly and promptly than one that tried to downplay or hide it.
It also helps to maintain a record of your compliance-related decisions during an incident. If regulators ever review how a situation was handled, having documented reasoning for the choices made can demonstrate that the response was thoughtful rather than reactive or negligent.
The Core Phases of an Incident Response Plan
Most established incident response frameworks, including those from NIST and SANS, break the process down into distinct phases. While the exact terminology can vary, the general structure remains consistent across most organizations. Let's go through each phase in detail.
Phase 1: Preparation
Preparation is the foundation of any incident response plan, and it is arguably the most important phase because everything else depends on it. This is where you identify your assets, understand your risks, and put the right tools and policies in place before anything happens.
Start by taking inventory of what you are actually protecting. For a business, this means identifying critical systems, sensitive data, and the applications your team relies on daily. For an individual, this could mean listing your important accounts, devices, and any sensitive personal or financial information stored online.
Next, define roles and responsibilities. Who will be in charge if an incident occurs? Who handles communication with customers or stakeholders? Who manages the technical containment and recovery process? Even in a small team, having clear ownership prevents confusion during a stressful moment.
Preparation also includes setting up preventive tools and habits. Regularly scanning devices for vulnerabilities, keeping software updated, and using secure browsing habits all reduce the likelihood of an incident occurring in the first place. Tools like AVO Security are often used during this phase to continuously monitor devices for threats before they escalate into full-blown incidents.
Documentation matters here too. Write down your incident response procedures in plain language, store them somewhere accessible even if your primary systems go down, and make sure everyone involved knows where to find them.
Phase 2: Identification
Identification is about recognizing that an incident has actually occurred. This sounds simple, but in practice, it can be surprisingly difficult. Many incidents go unnoticed for days, weeks, or even months.
Signs of a potential incident vary widely. It could be unusual login activity, unexpected pop-ups, a device running slower than usual, or an email that looks slightly off. Training yourself and your team to recognize these warning signs is a critical part of this phase.
Automated detection tools play a major role here as well. Features that scan devices and networks for suspicious activity, such as Smart Scan, can flag potential threats early, often before a human would notice anything wrong. Early detection significantly reduces the time an attacker has to cause damage.
Once a potential incident is identified, the next step is verification. Not every unusual event is a genuine security incident, so it is important to confirm what is actually happening before jumping into a full response. This might involve checking logs, reviewing recent activity, or consulting with a technical team member.
Documenting everything during identification is essential. Note the time the anomaly was first observed, what triggered the suspicion, and any initial findings. This information becomes valuable later when analyzing the root cause and improving your defenses.
Phase 3: Containment
Once an incident is confirmed, the priority shifts to containment: stopping the problem from spreading further. This phase often needs to happen quickly, but rushing without a plan can sometimes make things worse.
Containment strategies generally fall into two categories: short-term and long-term. Short-term containment involves immediate actions like disconnecting an infected device from the network, disabling a compromised account, or blocking a malicious IP address. Long-term containment involves more thorough measures, such as patching vulnerabilities while keeping systems operational.
For individuals dealing with a compromised network at home, containment might mean isolating the affected device and checking the security of the entire home network. This is where features focused on Wifi Security become particularly relevant, helping identify whether other devices on the same network have also been affected or exposed.
It is also important to preserve evidence during containment rather than immediately wiping everything clean. Logs, screenshots, and system snapshots can help during the later investigation phase and may even be required for legal or compliance reasons.
Communication during containment should be measured and factual. If customers, employees, or family members need to be informed, avoid speculation and stick to what is currently known. Overreacting or underreacting at this stage can both create unnecessary complications.
Phase 4: Eradication
Eradication is the phase where you remove the actual cause of the incident from your systems. This goes beyond containment; it means eliminating malware, closing the vulnerability that was exploited, and ensuring the threat cannot simply return.
This phase often requires a deeper technical investigation. What exactly allowed the incident to happen? Was it an outdated piece of software, a weak password, a phishing email that bypassed filters, or a malicious link that was clicked without verification?
If a phishing link was involved, this is a good time to reinforce the habit of checking suspicious URLs before clicking them. A Link Checker can help verify whether a link leads somewhere legitimate or whether it has been flagged as part of a known scam.
Eradication also involves updating security configurations to prevent a repeat occurrence. This could mean changing passwords across multiple accounts, enabling multi-factor authentication, updating firewall rules, or removing any unauthorized access that was granted during the incident.
It is worth being thorough here rather than rushing to move on. Incomplete eradication is one of the most common reasons incidents recur shortly after they appear resolved.
Phase 5: Recovery
Recovery is the process of restoring affected systems and returning to normal operations. This phase requires careful planning because bringing systems back online too quickly, without confirming the threat is fully removed, can lead to a repeat incident.
Start by testing systems in a controlled environment before fully restoring them to production or daily use. Monitor closely for any signs that the issue has not been fully resolved. This is often a good time to run a comprehensive scan across all devices to confirm nothing was missed.
For businesses, recovery might also involve restoring data from backups, verifying data integrity, and gradually reintroducing systems back into the network rather than doing everything at once. Having reliable, regularly tested backups is one of the most underrated aspects of incident response planning.
For individuals, recovery could mean resetting compromised accounts, checking whether any personal information was exposed, and monitoring financial statements for unusual activity. If an email account was involved, running an Email Breach Scan can help confirm whether your credentials have appeared in any known data leaks.
Recovery is also a good time to communicate transparently with anyone affected. Letting stakeholders know that the issue has been resolved, what was done to fix it, and what steps are being taken to prevent recurrence helps rebuild trust.
Phase 6: Lessons Learned
The final phase is often skipped, but it is arguably one of the most valuable. After the immediate crisis has passed, take time to review what happened, why it happened, and what could have been done differently.
Gather everyone involved and walk through the timeline of the incident. What worked well during the response? What caused delays or confusion? Were there any gaps in the original plan that became obvious only during the actual event?
Use these findings to update your incident response plan. Security is not static, and your plan should evolve based on real experiences rather than remaining a theoretical document that never changes.
This phase is also an opportunity to reinforce good habits going forward. If the incident stemmed from a weak password or a lack of awareness about phishing, consider whether additional training or better tools could help prevent similar issues in the future.
Building Preventive Layers Into Your Plan
While the six phases above outline how to respond after something happens, a genuinely effective incident response plan also incorporates preventive measures. The goal is not just to respond well but to reduce how often you need to respond at all.
Securing Your Browsing Activity
A large percentage of security incidents start with something as simple as visiting a malicious website. Whether through a phishing email, a fake advertisement, or a compromised search result, unsafe browsing is one of the most common entry points for attackers.
Incorporating browser-level protection into your prevention strategy can catch many threats before they ever reach your device. Features like Web Shield work by identifying and blocking access to known malicious or suspicious websites in real time, adding a layer of defense that complements your own vigilance.
This kind of protection is particularly valuable for teams where not everyone has the same level of security awareness. Not every employee or family member will recognize a suspicious website at first glance, so having a technical safeguard in place reduces reliance on individual judgment alone.
Protecting Network Connections
Public Wi-Fi networks, whether at a coffee shop, airport, or hotel, are notoriously insecure. Data transmitted over these networks can sometimes be intercepted, especially if the network itself has been set up maliciously to mimic a legitimate one.
Using a VPN when connecting to unfamiliar networks encrypts your internet traffic, making it significantly harder for anyone to intercept sensitive information. Incorporating VPN usage into your standard operating procedure, especially for remote workers or frequent travelers, is a practical step that many incident response plans now include as a baseline requirement.
This is not just about avoiding worst-case scenarios. It is about building a habit where secure connections become the default rather than an afterthought, particularly for anyone regularly accessing sensitive accounts or company systems while away from a trusted network.
Verifying Links and QR Codes Before Interacting
QR codes have become increasingly common, appearing on restaurant menus, parking meters, and marketing materials. Unfortunately, this popularity has made them an attractive target for scammers who replace legitimate codes with malicious ones leading to phishing sites or malware downloads.
Before scanning an unfamiliar QR code, especially one in a public space, it is worth verifying where it actually leads. Tools like a QR Scanner that check the destination URL before opening it can prevent an accidental visit to a harmful site.
The same principle applies to regular links shared through email, text messages, or social media. Verifying a link's legitimacy before clicking, particularly when it comes from an unexpected source, is a small habit that prevents a significant number of incidents from ever starting.
Monitoring for Data Breaches
Even with strong personal security habits, your information can still be exposed if a company or service you use experiences a data breach. This is largely outside your control, but staying informed about it is not.
Regularly checking whether your email address or associated accounts have appeared in known data breaches allows you to act quickly, changing passwords and monitoring for suspicious activity before an attacker has a chance to exploit the exposed information. This kind of monitoring should be a standard part of any personal or organizational incident response strategy.
Extending Protection to Families and Shared Devices
Incident response planning is often discussed in a business context, but households face similar risks, particularly when children use shared devices or have their own accounts. A family's incident response plan looks a little different but follows the same underlying logic: know what you are protecting, set up preventive measures, and know what to do if something goes wrong.
Setting appropriate boundaries around what children can access online, and monitoring for signs of inappropriate contact or content, is part of a broader family security strategy. Features like Parental Controls can help parents manage this without needing to monitor every single interaction manually.
This is less about restricting access and more about creating a safer digital environment where risks are identified early, before they turn into a larger incident affecting the entire household.
Measuring the Effectiveness of Your Incident Response Plan
Once a plan is in place, it helps to track a few basic metrics to understand whether it's actually working. Without measurement, it's easy to assume a plan is effective simply because nothing catastrophic has happened recently.
One useful metric is detection time: how long does it typically take from when an incident begins to when it's first identified? Shorter detection times generally mean less damage, since attackers have less opportunity to spread or extract data before being noticed.
Another helpful measure is containment time, tracking how quickly the team can isolate an affected system or account once an incident is confirmed. Comparing this across different incidents over time can reveal whether your team's response speed is improving or slipping.
Recovery time, the duration between containment and full restoration of normal operations, is also worth tracking. Long recovery times can indicate gaps in backup procedures, unclear recovery steps, or insufficient testing of the recovery process beforehand.
Finally, consider tracking how many incidents stem from the same root cause. If multiple incidents trace back to the same unpatched vulnerability or the same type of phishing attempt, that's a signal that your preventive measures in that specific area need reinforcement rather than just repeated incident response.
These metrics don't need to be tracked with complex tools or dashboards, especially for smaller teams. A simple spreadsheet noting the type of incident, detection time, containment time, and root cause is often enough to spot patterns and prioritize improvements.
Common Mistakes When Building an Incident Response Plan
Even well-intentioned incident response plans can fall short if certain common mistakes are not addressed. Recognizing these pitfalls in advance can save significant time and stress later.
One frequent mistake is treating the plan as a one-time project rather than an ongoing process. Threats evolve, technology changes, and teams grow or shrink. A plan written two years ago and never revisited is unlikely to reflect your current environment accurately.
Another common issue is a lack of clear communication protocols. During an actual incident, people often assume someone else is handling notifications or updates, leading to delays or, worse, no communication at all until it's too late.
Overcomplicating the plan is another pitfall. If the document is so long and technical that no one actually reads it or remembers what to do, it defeats its own purpose. A good incident response plan should be clear, concise, and easy to reference under pressure.
Finally, many organizations and individuals fail to practice their plan before they need it. Reading through a plan is very different from actually walking through the steps during a simulated incident. Without practice, even a well-written plan can fall apart when real pressure sets in.
Building an Effective Incident Response Team
For organizations, having the right people involved is just as important as having the right procedures. An incident response team does not need to be large, but it does need clearly defined roles.
Typically, this team includes an incident response lead who coordinates the overall effort, technical staff responsible for investigation and containment, a communications lead who manages internal and external messaging, and, depending on the size of the organization, legal or compliance representatives.
Smaller organizations or individuals do not need a formal team in the traditional sense, but it still helps to identify who you would contact for support. This could be an IT consultant, a trusted technical friend, or a dedicated support service depending on the severity of the situation.
Regardless of team size, everyone involved should know their role in advance. Assigning responsibilities during an actual crisis wastes valuable time and often leads to overlapping or missed tasks.
Testing and Updating Your Incident Response Plan
An incident response plan is only as good as its last test. Running tabletop exercises, where the team walks through a hypothetical incident scenario step by step, helps identify gaps before a real incident exposes them.
These exercises do not need to be elaborate. Even a simple discussion-based walkthrough, asking "what would we do if this happened," can reveal misunderstandings about roles or missing steps in the process.
After any real incident, or after each testing exercise, update the plan based on what was learned. This keeps the document relevant and ensures it reflects your actual current systems, team structure, and threat landscape rather than an outdated version of your environment.
It also helps to review the plan whenever significant changes occur, such as adopting new software, hiring new team members, or expanding into new markets with different regulatory requirements. Treating the plan as a living document rather than a static one is what separates genuinely effective incident response from a plan that simply exists on paper.
Third-Party and Supply Chain Risks
Modern businesses rarely operate in isolation. Most rely on a network of vendors, cloud providers, software tools, and contractors, any of which could become the entry point for a security incident even if your own systems are well protected.
A vendor with weak security practices can expose your data indirectly, since many partnerships involve sharing access to systems, customer information, or internal tools. This is sometimes referred to as a supply chain or third-party risk, and it's an area that's often overlooked in incident response planning.
Include a review of your key vendors and their security practices as part of your preparation phase. Ask whether they have their own incident response procedures, how they handle data you share with them, and how quickly they would notify you if something went wrong on their end.
Your incident response plan should also account for scenarios where a third-party breach affects you, even though the incident didn't originate within your own systems. This means having a process for assessing the impact, notifying anyone on your end who might be affected, and adjusting your own security measures based on the vendor's incident.
Incident Response for Small Businesses and Solo Professionals
Many resources on incident response are written with large enterprises in mind, but small businesses and independent professionals face similar risks, often with fewer resources to address them. This does not mean a formal plan is out of reach; it simply needs to be scaled appropriately.
Start with the basics: know what data you handle, where it is stored, and who has access to it. For a freelancer or small business owner, this might be as simple as listing your email accounts, cloud storage, and any tools that store client information.
Next, establish basic preventive habits. Regularly updating software, using strong and unique passwords, and being cautious about links and attachments go a long way in reducing risk without requiring significant investment.
Finally, know your response steps in advance, even if they are simple. Who will you contact if your business email is compromised? What will you tell clients if their data might have been affected? Having these answers ready before an incident occurs makes a real difference in how quickly and confidently you can respond.
Communicating with External Stakeholders
Beyond internal teams and immediate technical response, many incidents eventually require communication with people outside the organization. This might include customers, business partners, vendors, or in more serious cases, the media.
The tone and timing of external communication matter significantly. Sharing information too early, before the situation is properly understood, risks spreading inaccurate details that may need to be walked back later. Waiting too long, on the other hand, can make it look like the situation was being hidden.
A good practice is to prepare general communication templates in advance as part of your planning phase, even if the specific details need to be filled in once an actual incident occurs. Having a starting point saves time and reduces the chance of poorly worded, rushed messaging during a stressful moment.
When communicating with customers specifically, focus on what happened in plain language, what data or systems may have been affected, and what steps they can take to protect themselves, such as changing a password or monitoring an account. Avoid excessive technical jargon that might confuse or alarm people unnecessarily.
For vendors or business partners who may also be affected, direct and prompt communication helps them take their own protective measures and maintains the trust needed for an ongoing working relationship.
The Human Element in Incident Response
Technology plays a significant role in both preventing and responding to security incidents, but people remain a central factor in almost every situation. Many incidents begin with human error, whether it's clicking a suspicious link, using a weak password, or falling for a convincing phishing attempt.
This means that ongoing awareness and education are just as important as any technical tool. Regularly reminding team members or family members about common tactics used by attackers, such as urgent-sounding emails or too-good-to-be-true offers, helps build a more security-conscious environment.
It also helps to create a culture where people feel comfortable reporting potential incidents without fear of blame. If someone accidentally clicks a malicious link, the priority should be addressing the issue quickly, not punishing the person who reported it. A blame-focused culture often leads to delayed reporting, which only makes incidents worse.
Regular, low-pressure training sessions tend to work better than occasional lengthy lectures. Short, periodic reminders about current phishing trends or common scam tactics keep security awareness fresh without becoming tedious enough that people start tuning it out entirely.
Documenting and Communicating During an Incident
Clear documentation throughout an incident serves multiple purposes. It helps the response team stay organized, provides a record for post-incident review, and may be necessary for legal or regulatory reasons depending on the nature of the incident and your location.
At a minimum, document when the incident was first detected, what actions were taken and by whom, and any communications sent internally or externally. This timeline becomes invaluable during the lessons-learned phase and can also protect your organization if questions arise later about how the situation was handled.
Communication during an incident should be honest and proportionate to what is actually known. Avoid making promises about timelines or outcomes that you cannot guarantee, and update stakeholders as new information becomes available rather than waiting until everything is fully resolved.
Conclusion
An incident response plan is not a luxury reserved for large corporations with dedicated security teams. It is a practical necessity for anyone who relies on digital systems, which today includes nearly everyone, whether running a business, managing a household, or simply trying to protect personal information online.
The core takeaway is straightforward: prepare before something happens, know the steps to take when it does, and take time afterward to learn and improve. Combine this structured approach with consistent preventive habits, and you significantly reduce both the likelihood and the impact of future security incidents. A plan you've thought through in advance, even a simple one, will always serve you better than trying to figure things out in the middle of a crisis.
Reference Links
How to Know If Your Phone Is Hacked
Is My Phone Hacked? 7 Signs to Check Right Now
What to Do If Your Phone Is Hacked
How to Remove a Virus from an Android Phone
Does a Mac Need Antivirus in 2026?











Sign in to leave a comment.