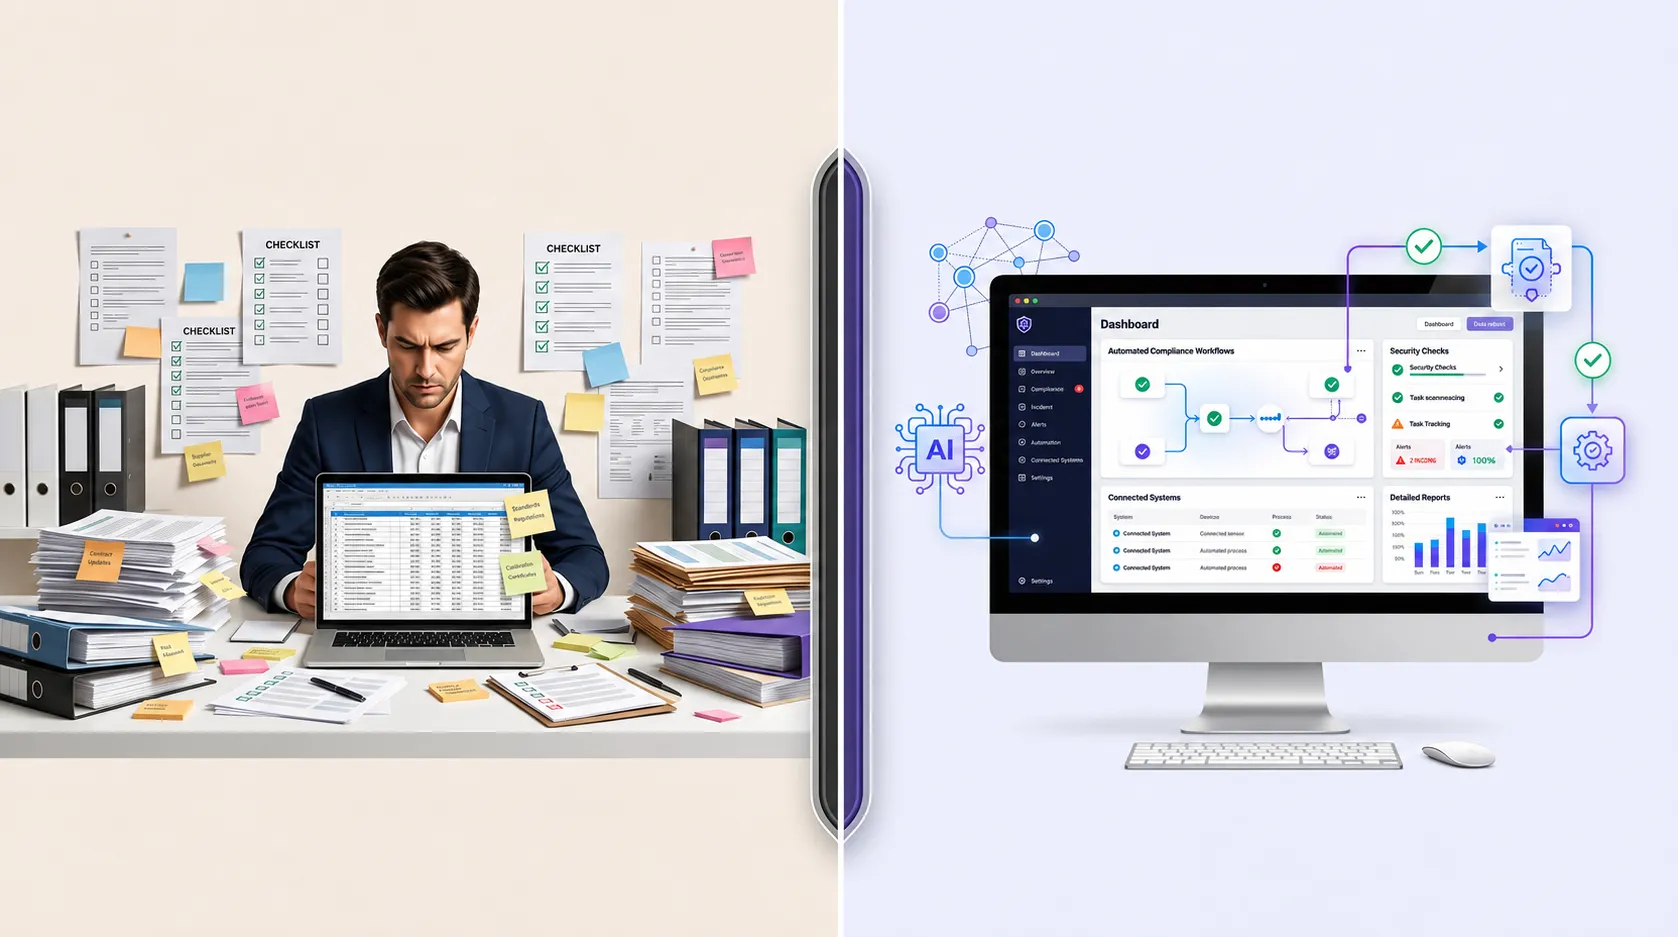


At some point, every growing company hits the same wall: compliance that used to be manageable with a shared spreadsheet and a folder of screenshots suddenly isn't. Maybe it's your first SOC 2 audit. Maybe it's a second framework getting added on top of the first. Either way, the question becomes unavoidable: do we keep doing this manually, or is it time to automate?
There's no universal right answer, but there is a clear way to think through it.
What "Manual Compliance" Actually Looks Like
Manual compliance management means exactly what it sounds like: spreadsheets tracking control status, screenshots gathered by hand before an audit, policies stored across shared folders and documents, and risk assessments done as one-off exercises rather than ongoing processes.
For a small team with a single, straightforward compliance requirement, this can genuinely work. It's low-cost, requires no new tooling, and doesn't demand much process overhead. The trade-off is that it scales poorly with every new framework, every new employee, every audit cycle adds manual work that grows roughly linearly (or worse) with your company's complexity.
What "Compliance Automation" Actually Looks Like
Compliance automation uses software to handle the repetitive parts of the process: automatically pulling evidence from your cloud infrastructure, identity provider, HR platform, and ticketing systems; continuously monitoring controls like MFA status and access reviews instead of checking them quarterly; and centralizing policy management and audit readiness into a single dashboard instead of scattered documents.
The core shift is from periodic to continuous. Instead of scrambling to reconstruct your compliance posture right before an audit, the evidence is already there, updated in real time, because the systems are integrated year-round.
Where the Real Differences Show Up
The two approaches diverge most clearly in a few areas:
Evidence collection. Manual means someone on your team manually exporting logs, taking screenshots, and compiling documents. Automated means the evidence is pulled continuously from connected systems with far less risk of something being missed or out of date by audit time.
Monitoring frequency. Manual compliance is typically checked quarterly or annually, which means a control could silently fail for months before anyone notices. Automated compliance monitors continuously, surfacing issues before they become audit findings.
Scalability. This is where manual processes tend to break down first. One framework with a small team is manageable by hand. Multiple frameworks SOC 2, ISO 27001, HIPAA, GDPR with a growing headcount become exponentially harder to track manually, while automated systems handle overlapping controls across frameworks from a single source of truth.
Resource allocation. Manual compliance consumes ongoing team time that scales with company growth. Automation has more upfront setup cost but lower long-term resource requirements, freeing up your security and compliance people to work on actual risk reduction instead of spreadsheet maintenance.
So Which One Is Right for You?
Manual compliance is probably still fine if your requirements are genuinely simple, you're only managing a single framework, your documentation is easy to keep current, and audit prep doesn't consume meaningful time or stress.
Compliance automation starts to make sense once your operations have grown more complex, you're managing multiple frameworks simultaneously, enterprise customers are asking for ongoing proof of compliance (not just a point-in-time report), or your company is scaling quickly enough that manual tracking is becoming a bottleneck rather than a formality.
Most companies don't start with automation, they start manual, because it's the lowest-friction option when requirements are simple. The transition point tends to arrive the moment compliance stops being an occasional task and starts being an ongoing operational burden.
The Practical Takeaway
This isn't really an automation-is-always-better argument. It's a fit-for-stage argument. A five-person start-up pursuing its first SOC 2 report doesn't need the same infrastructure as a 200-person company juggling SOC 2, ISO 27001, and HIPAA simultaneously. The right move is matching your compliance approach to your actual operational complexity and being honest about which side of that line your company is on right now.
For a deeper look at the feature-by-feature differences, audit readiness comparisons, and a suggested workflow for both approaches, I'd recommend this compliance automation vs manual compliance management guide ; it lays out the trade-offs in more detail than I've covered here.












Sign in to leave a comment.