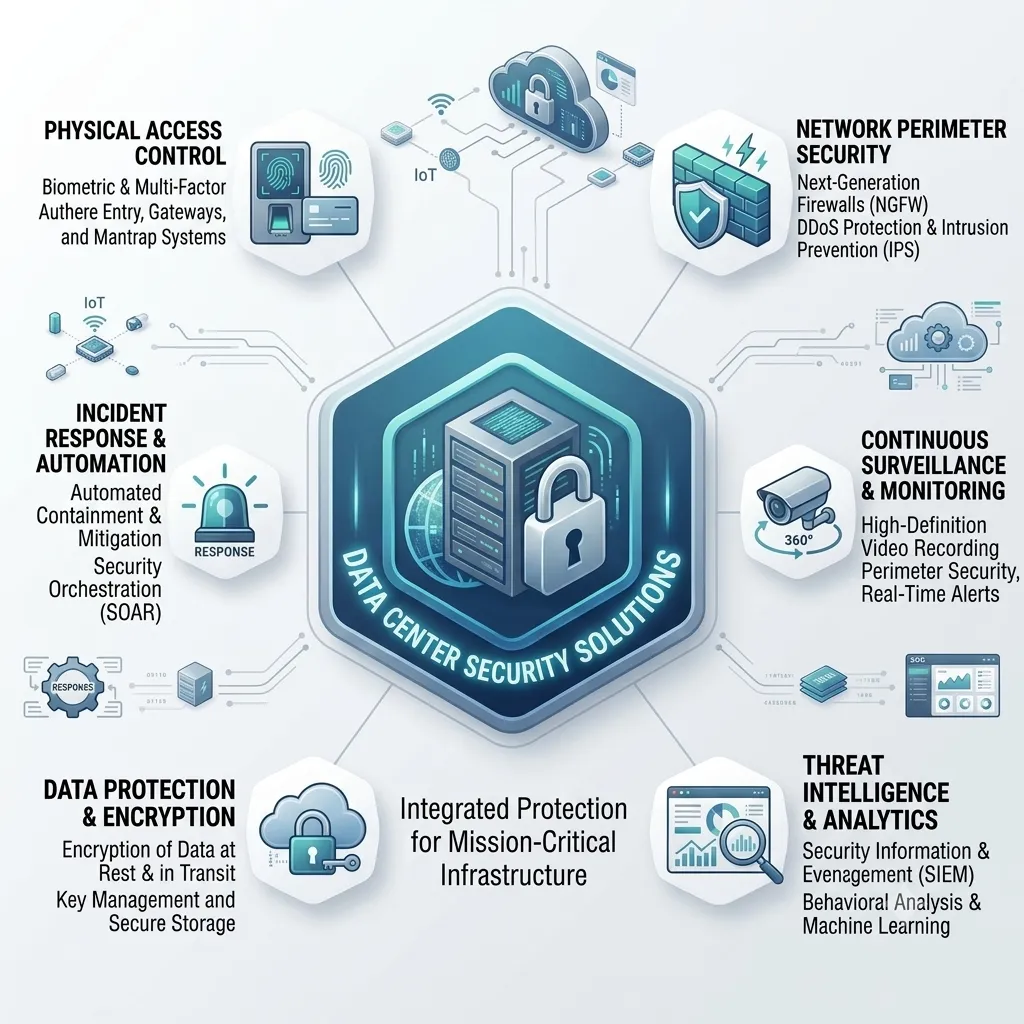

As the Kingdom races to become a regional cloud and AI hub, Data Center Security has moved from a back-office IT concern to a boardroom priority. Every new hyperscale facility, colocation site, and enterprise server room built under Vision 2030 now carries a mandate to defend against physical intrusion, cyberattack, and data compromise simultaneously. This guide walks through the layered data center protection framework in Saudi Arabia that operators are standardizing on, and why getting each layer right is no longer optional.
Why Data Center Security Has Become a National Priority
Saudi Arabia's push toward digital transformation has turned data centers into critical national infrastructure alongside power grids and water systems. Banks, telecom operators, oil and gas companies, and government ministries increasingly host their most sensitive workloads in-Kingdom rather than offshore, driven by data-residency rules and a genuine strategic interest in controlling where mission-critical information physically sits. That concentration of value makes every facility a higher-value target, whether the threat is a coordinated cyber intrusion or someone attempting to walk through an unguarded loading dock.
A single breach — physical or digital — at a facility hosting banking transactions or government records carries consequences that extend well beyond the operator's own balance sheet. Regulators, insurers, and enterprise customers now expect documented, auditable security controls before they will even shortlist a colocation provider, which is why security architecture has become a competitive differentiator rather than a compliance checkbox.

Cybersecurity for Data Center: Defending the Digital Perimeter
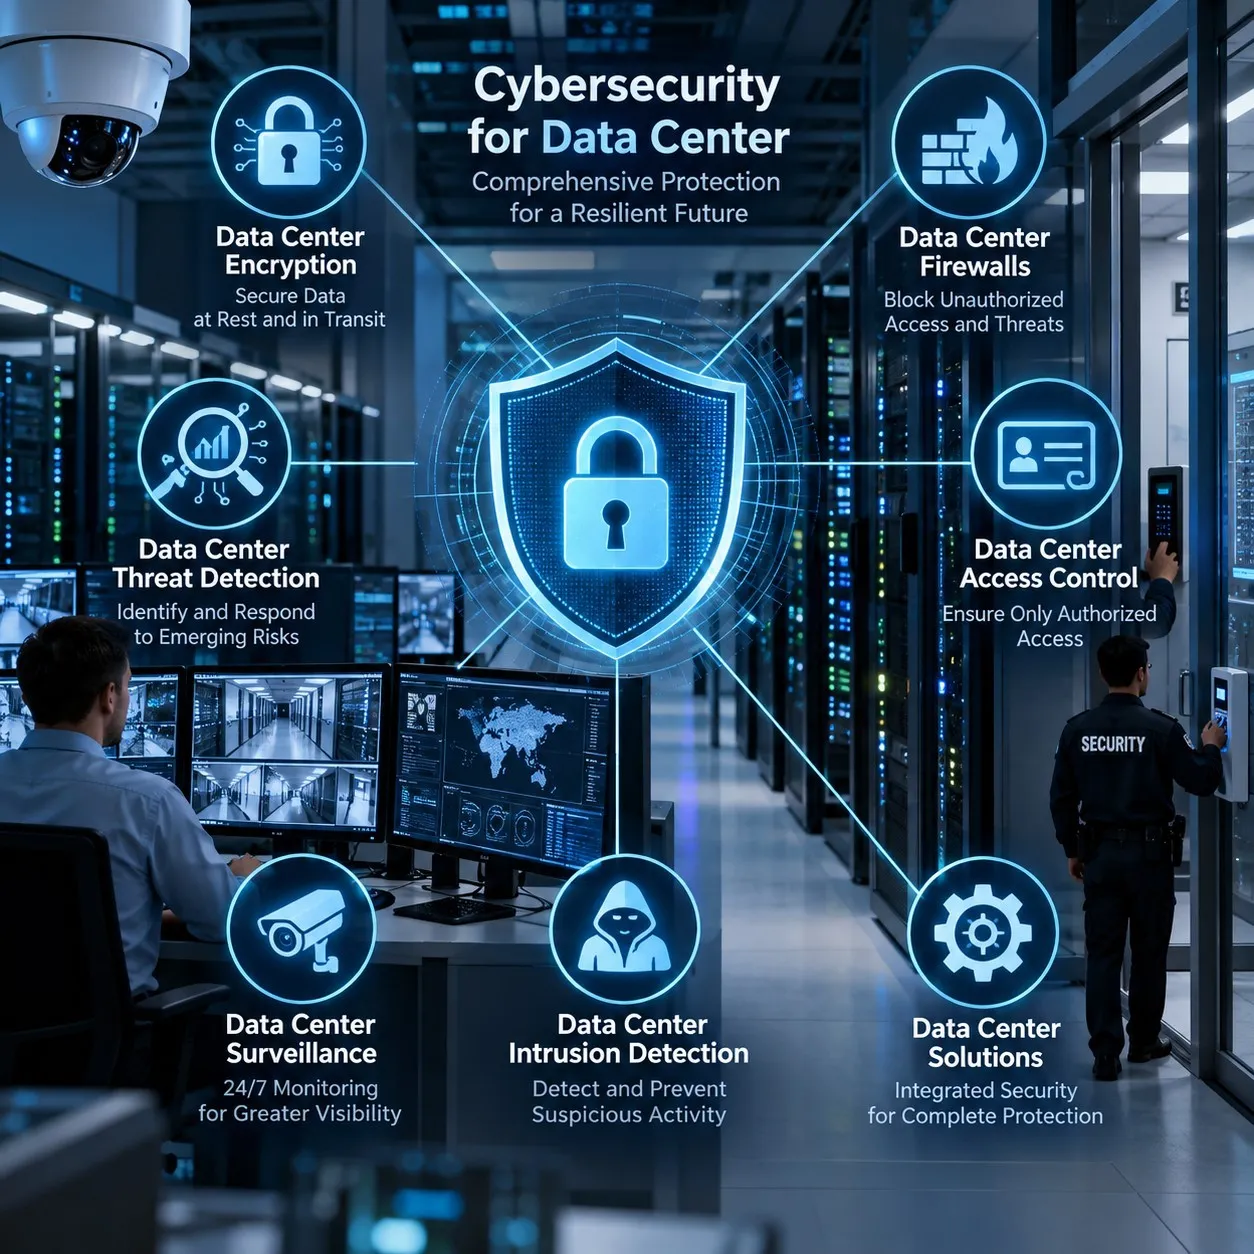
Cybersecurity for Data Center environments starts with the assumption that attackers will eventually reach the network edge, and layers defenses so that no single failure exposes the whole facility. This means network segmentation between customer environments, continuous vulnerability scanning, hardened hypervisors, and strict patch-management cycles for every piece of infrastructure software running inside the facility.
Insider risk deserves equal attention. Role-based access to management consoles, mandatory multi-factor authentication for administrative logins, and detailed session logging all reduce the chance that a compromised credential — rather than a sophisticated external attacker — becomes the point of failure. Saudi operators pursuing ISO 27001 or SAMA cybersecurity framework alignment build these controls in from day one rather than retrofitting them under audit pressure.
Data Center Encryption: Protecting Data at Rest and in Transit
Data Center Encryption is the last line of defense when every other control fails — if storage media or network traffic is intercepted, strong encryption ensures the data itself remains unreadable. Facilities operating at enterprise scale apply AES-256 encryption to data at rest across storage arrays and backup media, paired with TLS-based encryption for data moving between racks, buildings, and connected cloud regions.
Key management is where many encryption strategies quietly fail. Centralized, hardware-security-module-backed key storage, combined with strict key-rotation policies, prevents a stolen backup tape or decommissioned drive from becoming a usable data source years after it left production. This is increasingly a specific line item auditor check for during Saudi financial-sector compliance reviews.
Data Center Firewalls: The First Line of Network Defense
Data Center Firewalls form the perimeter control point between the facility's internal network and the outside world, inspecting traffic for known attack signatures, anomalous patterns, and unauthorized access attempts before they ever reach a hosted workload. Modern deployments favour next-generation firewalls capable of deep packet inspection and application-aware filtering, layered alongside internal segmentation firewalls that isolate individual tenant environments from one another inside a shared colocation facility.
- Perimeter firewalls inspecting all inbound and outbound internet-facing traffic
- Internal segmentation firewalls isolating tenant environments in shared facilities
- Automated threat-signature updates synced against global intelligence feeds
- Redundant firewall pairs configured for automatic failover without service interruption
Industry Applications: Where Layered Security Matters Most
Banking and Financial Services
Core banking systems and payment-processing infrastructure demand the strictest combination of encryption, access governance, and audit logging, since a compromise here carries direct financial and regulatory consequences.
Government and Public Sector
Ministries and public agencies hosting citizen data and national systems require facilities certified against government-grade physical and cyber standards, often exceeding commercial colocation baselines.
Telecommunications and Cloud Providers
Hyperscale and telecom-operated facilities carry the added complexity of multi-tenant isolation, where one customer's workload must remain provably segmented from another's at every layer of the stack.
Oil, Gas, and Industrial Enterprises
Operational technology data feeding into corporate data centers introduces additional intrusion-detection requirements at the boundary between IT and industrial control networks.
Emerging Trends Shaping Data Center Security
Security architecture for critical infrastructure is not static, and several trends are actively reshaping how facilities across the region approach protection. Zero-trust network design — where no device or user is implicitly trusted regardless of location inside the perimeter — is increasingly the default rather than an advanced option, requiring continuous verification for every access request rather than a single check at the network edge.
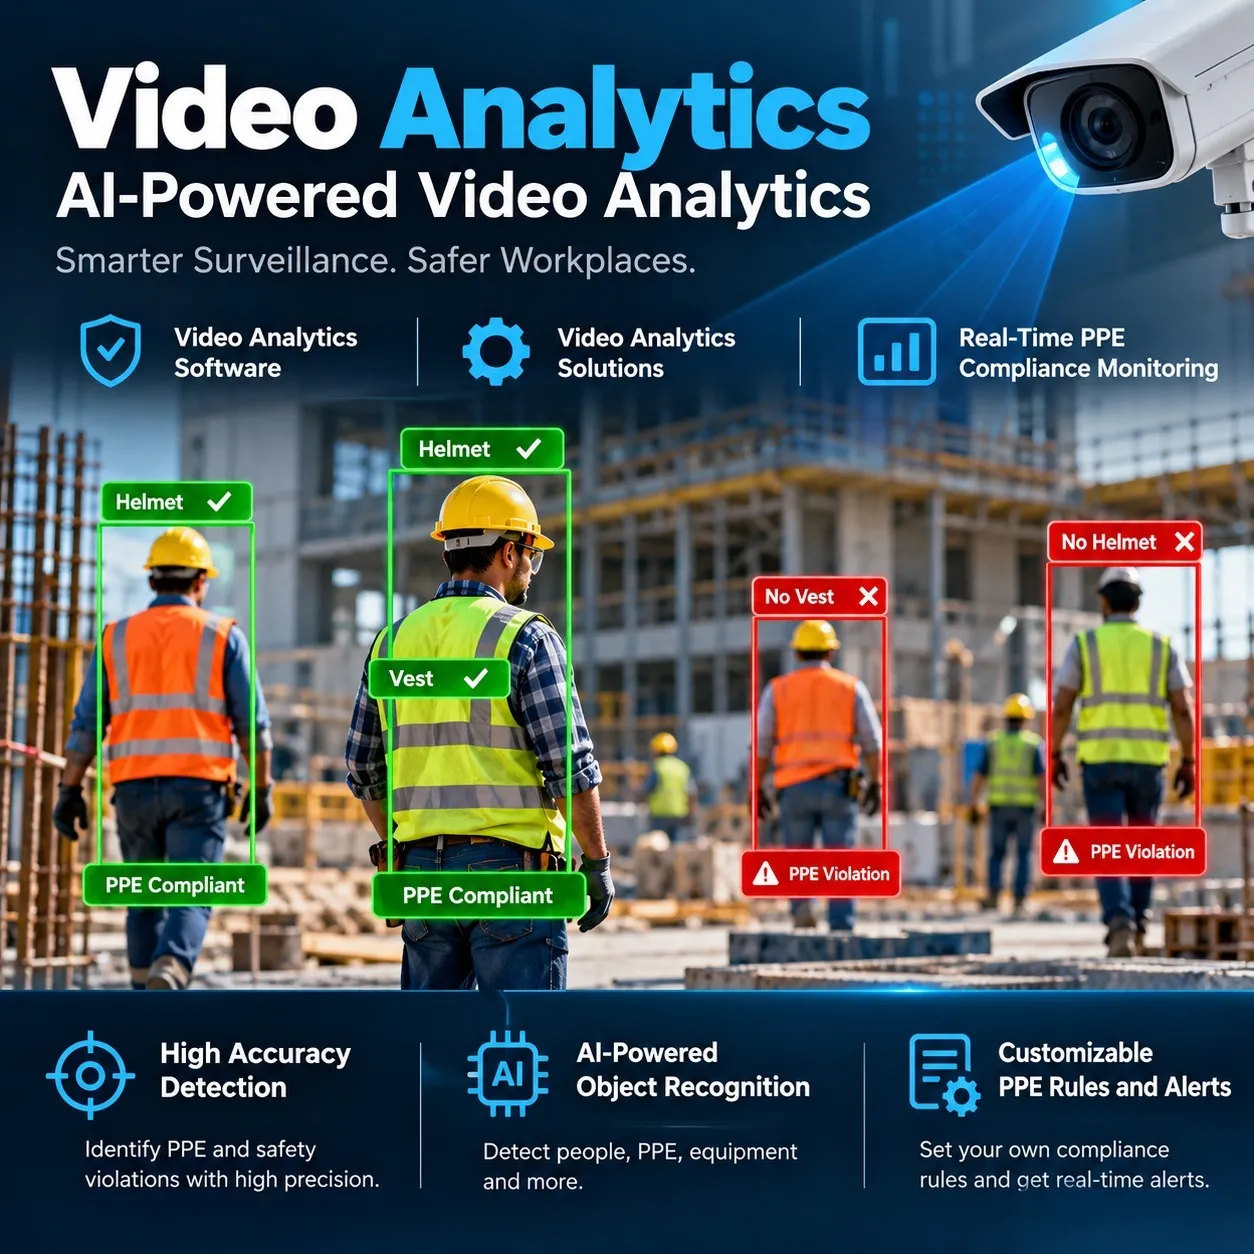
AI-driven anomaly detection is following a similar trajectory, moving from a differentiator to an expected baseline. Machine-learning models trained on historical access and network patterns can flag subtle deviations — a server communicating with an unusual external address, or a badge used at an atypical hour — well before a human analyst would notice the pattern manually. Combined with automated response playbooks, this shortens the window between detection and containment considerably.
Disaster Recovery and Business Continuity Planning
Security and resilience are closely linked disciplines: a facility that successfully repels an intrusion attempt but has no tested recovery plan for a subsequent outage has only solved half the problem. Redundant power and cooling, geographically separated backup sites, and regularly tested failover procedures all fall within a mature security program, since availability is itself a security objective under most regulatory frameworks operators must satisfy.
Tabletop exercises simulating both cyber incidents and physical breach scenarios help facilities teams validate that documented procedures actually work under pressure, rather than discovering gaps for the first time during a real event.
Conclusion
Protecting critical digital infrastructure in the Kingdom now demands a genuinely layered approach, where Data Center Security brings together Cybersecurity for Data Center defenses, Data Center Encryption, and Data Center Firewalls with physical Data Center Access Control, Data Center Surveillance, Data Center Intrusion Detection, and Data Center Threat Detection working as one system. Whether the requirement is Data Center Security KSA-wide or specific to Data Center Security Riyadh facilities, Tektronix delivers the integrated expertise operators need to meet both regulatory and operational demands.
























Sign in to leave a comment.