

Introduction
India is making a major change to how every business must handle personal data. The main duties of the Digital Personal Data Protection (DPDP) Rules, 2025 come into force on 13 May 2027, and from that date the penalties apply too: up to ₹250 crore for a single failure.
Most businesses are preparing their CRM, website forms and billing systems. Almost nobody is looking at the inbox. Yet that's where years of résumés, Aadhaar copies, salary slips, vendor bank details and customer complaints quietly pile up, forwarded, downloaded and synced to phones.
This guide explains, in plain language, what the DPDP Rules mean for your business email, what you need to change, and a checklist you can finish well before the deadline.
Key takeaways
- Deadline: The main DPDP duties and penalties start on 13 May 2027.
- Email is in scope: Résumés, KYC copies, salary slips and customer complaints in inboxes are all personal data.
- Biggest risk: Failing to take reasonable security safeguards can cost up to ₹250 crore. Failing to report a breach can cost up to ₹200 crore.
- Logs: Keep sign-in, traffic and processing logs for at least one year.
- Hosting: DPDP does not require all email to be hosted in India, but RBI rules for banks and government rules can.
In this article
- What is changing, and when?
- Why is email a DPDP risk?
- What do the DPDP Rules require from your email?
- Does business email have to be hosted in India?
- What should businesses do before 13 May 2027?
- What should you ask your email provider?
- How XgenPlus helps
- Frequently asked questions
- Conclusion
1. What is changing, and when?
The Ministry of Electronics and IT (MeitY) notified the Digital Personal Data Protection Rules, 2025 on 13 November 2025 (Gazette notification G.S.R. 846(E)). The Rules apply in three phases:
| Date | What comes into force | What it means for your email |
| 13 Nov 2025 | Data Protection Board of India | The regulator is in place |
| 13 Nov 2026 | Consent Manager registration (Rule 4) | Mostly affects consent platforms |
| 13 May 2027 | Notice, security, breach reporting, retention, children's data, rights, transfers (Rules 3, 5–16, 22, 23) and penalties | Your mailboxes must be compliant |
As of October 2026, no amendment to shorten this timeline has been notified, so 13 May 2027 remains the legal date.
2. Why is email a DPDP risk?
When companies plan for DPDP, they look at their CRM, website forms and customer database. Email often holds more personal data than all three:
- HR inboxes: résumés from every candidate you never hired, medical certificates, salary slips
- Accounts inboxes: vendor bank details, PAN and GST documents
- Support and sales inboxes: customer phone numbers, addresses, order histories, complaints
- Everyone's inbox: Aadhaar and KYC copies sent "just for verification"
The same data is then copied into forwards, attachments, mobile phones and the mailboxes of employees who left years ago. If you can't say where personal data lives in your email, you can't protect it, erase it, or answer a request about it.
3. What do the DPDP Rules require from your email?
Reasonable security safeguards (Rule 6)
The Rules expect access controls, encryption, logging and backups. For email, that means:
- Two-factor authentication for every user, not only administrators
- Sign-in limited to known office IP addresses or chosen countries where possible
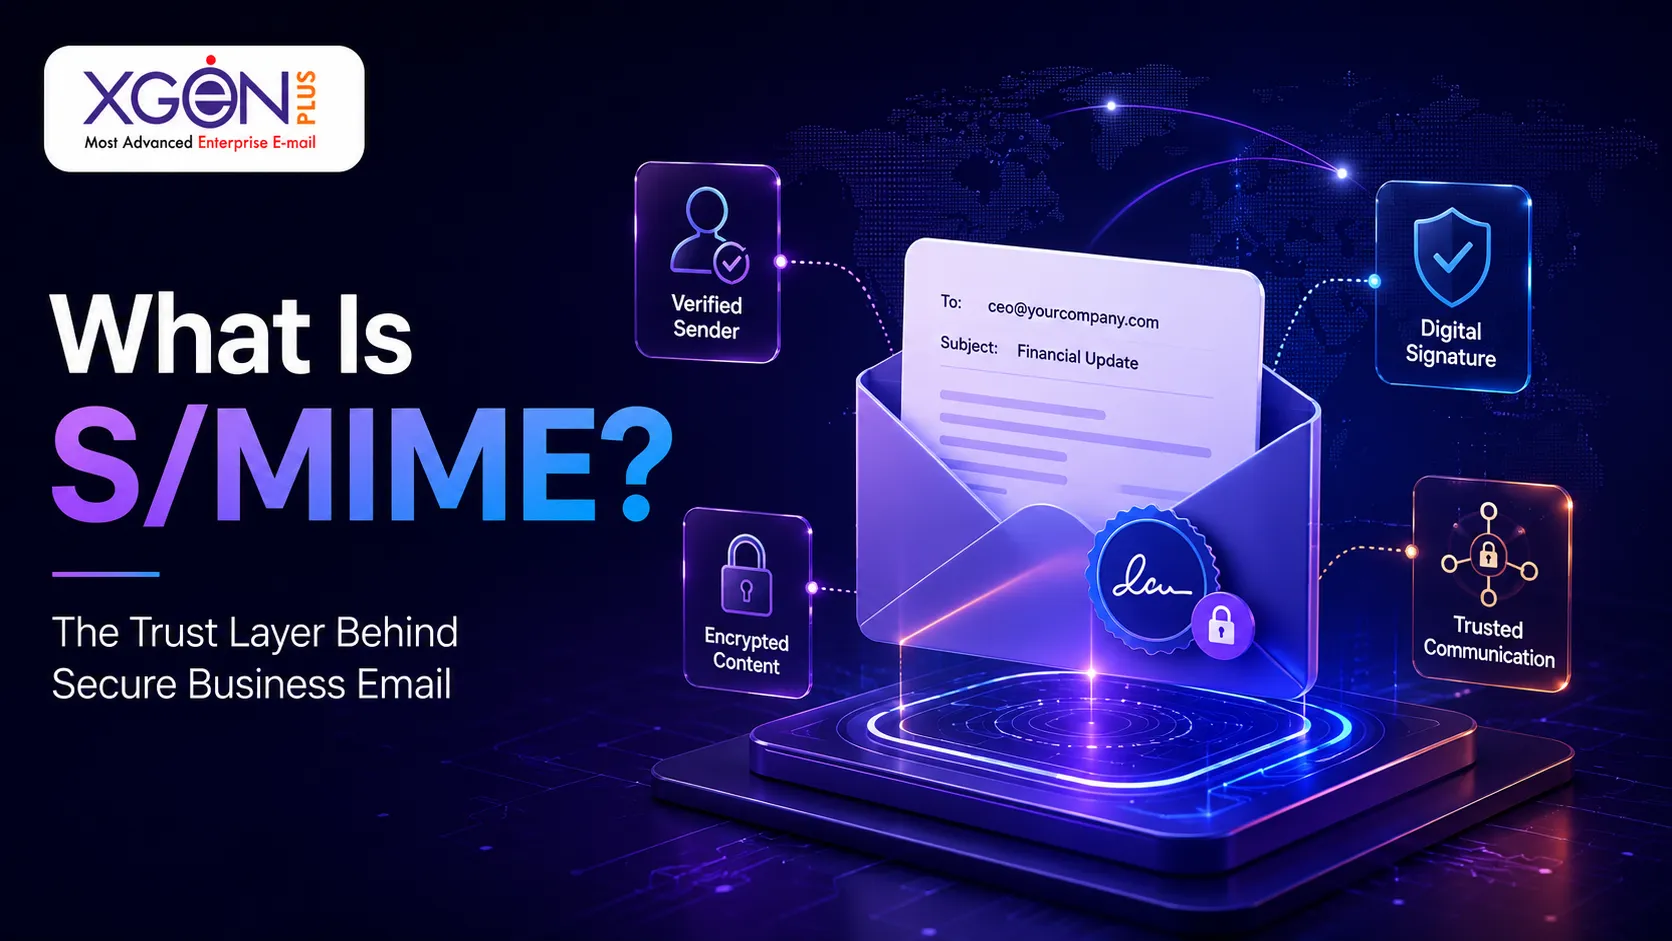
- Encryption, such as S/MIME email encryption, for sensitive messages
- Data loss prevention (DLP) to stop personal data leaving by mistake
Penalty: up to ₹250 crore for failing to take reasonable security safeguards to prevent a breach.
Breach reporting (Rule 7)
If personal data is breached, you must:
- inform each affected person promptly and in plain language
- inform the Data Protection Board without delay
- send the Board full details within 72 hours, or a longer period it allows
A single hacked mailbox containing customer data can be a reportable breach. To report accurately, you need sign-in and access logs that show what was opened, from where, and when.
Penalty: up to ₹200 crore for failing to notify the Board or affected people.
Log retention (Rule 8)
Personal data, traffic data and processing logs must be kept for at least one year. Many email services keep sign-in and delivery logs for only 30 to 90 days. Check yours.
Erasing data you no longer need (Rule 8)
Once the purpose for collecting personal data is served, you must erase it, unless another law requires you to keep it longer. Tax and labour laws, for example, require you to keep certain records.
Rejected candidates' résumés sitting in an HR inbox for five years are exactly what this rule targets.
The Third Schedule adds a specific duty for large e-commerce, online gaming and social media platforms. They must erase the data of users who have been inactive for the period it sets, and warn those users 48 hours before erasure.
A contract with your email provider (Section 8)
Under DPDP, your business is the data fiduciary and your email provider is a data processor. The legal responsibility stays with you. You need a written data processing agreement covering:
- security standards
- how and when the provider tells you about a breach
- deletion of your data when you leave
Rights requests and grievances (Rule 14)
People can ask what data you hold about them, ask for corrections, or ask for erasure. You must publish how long you take to respond to grievances, and that period cannot exceed 90 days.
In practice, someone in your team must be able to search every mailbox for one person's data. That requires admin-level search and domain administration or eDiscovery.
4. Does business email have to be hosted in India?
Not under DPDP in general. Rule 15 on cross-border transfers comes into force on 13 May 2027. The Act allows transfers abroad except to countries the government restricts by notification.
Sector rules can be stricter. RBI-regulated banks and NBFCs, central and state government departments, PSUs and defence suppliers often have data-localisation or on-premise email requirements. For them, where email is hosted can decide whether a provider is allowed at all.
5. What should businesses do before 13 May 2027?
- Map the mailboxes that hold the most personal data: HR, accounts, support, sales.
- Enforce two-factor authentication for every user. Lock down accounts in 5 minutes.
- Confirm your provider keeps sign-in and mail logs for at least 12 months.
- Write an email retention policy: what to keep, for how long, and under which law.
- Automate deletion or archiving for recruitment and support folders.
- Stop collecting Aadhaar and KYC copies by email; use a secure online form or portal instead.
- Sign a data processing agreement with your email provider.
- Prepare a breach response plan: who decides, who informs the Board, who emails affected people.
- Name a person for data requests and test a search across all mailboxes.
- Offboard properly: when an employee leaves, secure, transfer or delete their mailbox.
6. What should you ask your email provider?
- Where exactly is my mail stored, including backups?
- How long do you keep sign-in and delivery logs?
- Will you sign a data processing agreement?
- How quickly will you tell me about a breach on your side?
- Can I enforce two-factor authentication for all users?
- Can I set retention and auto-delete rules per mailbox or folder?
- Can an administrator search all mailboxes for one person's data?
- When I leave, how do I export my data, and how do you confirm deletion?
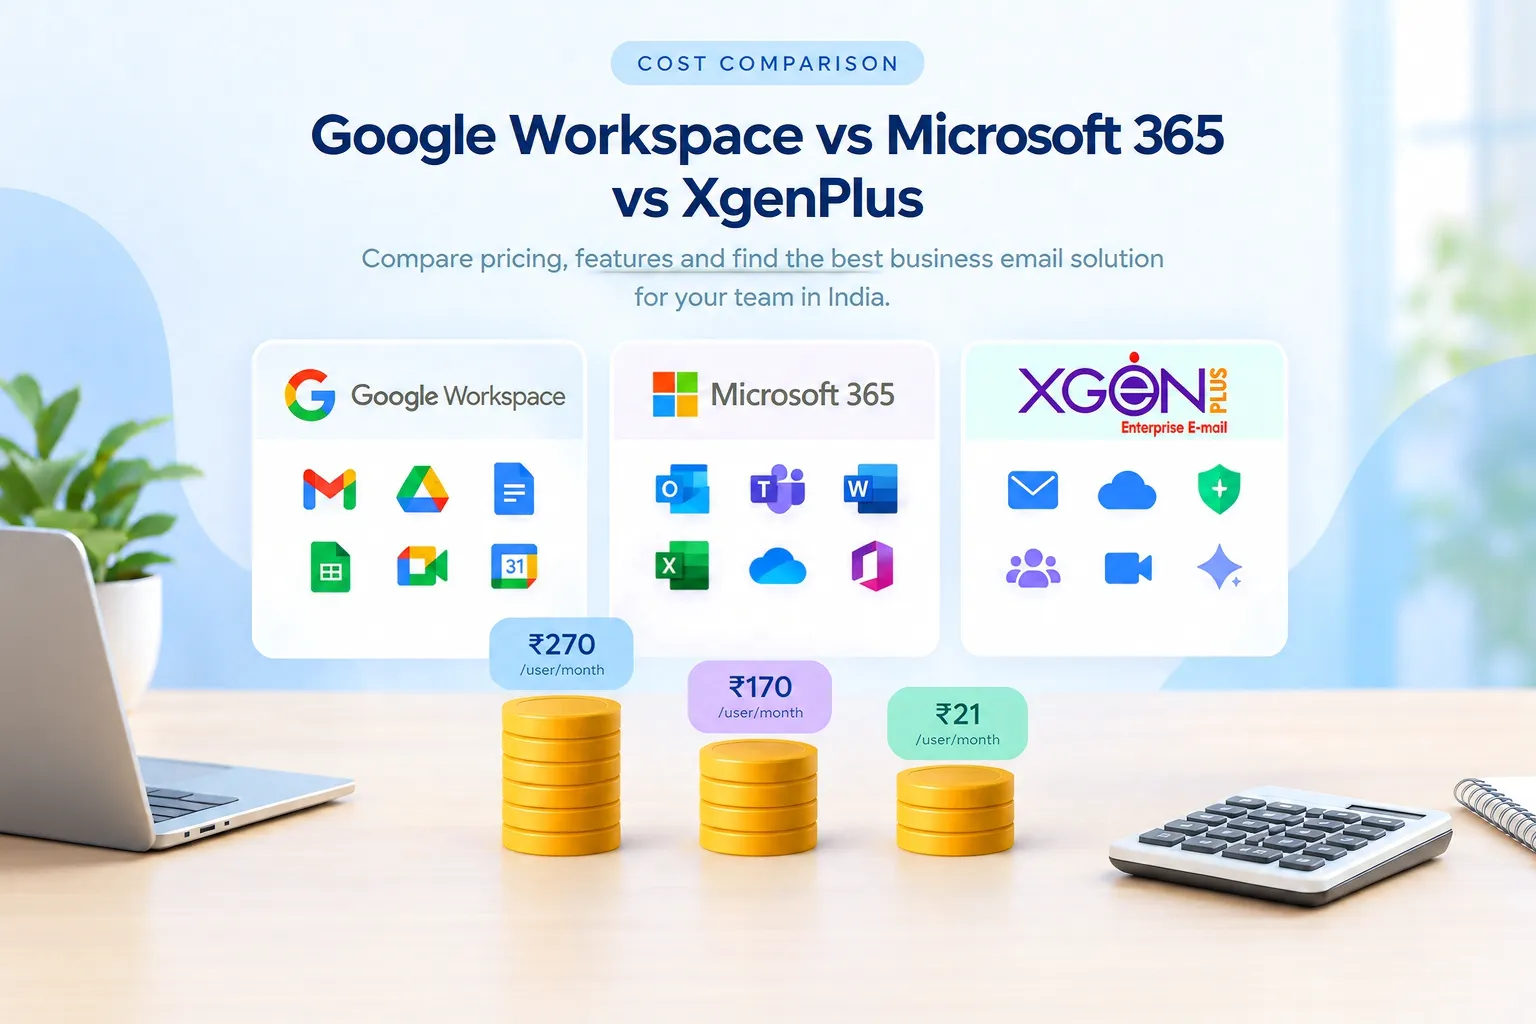
If any answer is vague, that's your first compliance risk. If you're comparing providers, see how XgenPlus compares with Google Workspace, Microsoft 365 and Zoho Mail.
7. How XgenPlus helps
XgenPlus is business email built and hosted in India by Data Xgen Technologies, Jaipur. An on-premise edition installs on your own servers when your sector or a tender requires it. Features that map to the DPDP duties above:
| DPDP duty | XgenPlus feature |
| Security safeguards | Two-factor sign-in (from Starter Pro); sign-in limited by country or office IP; S/MIME encryption and DLP (from Advance Pro). Compare plans and pricing |
| Breach reporting | Sign-in history and session controls |
| Retention and erasure | Email retention controls; bulk delete by search |
| Rights requests | Admin search; archiving and eDiscovery (on-premise Enterprise edition) |
| Privacy by design | Users consent before an admin can see their account logs, and admins never see mail content |
Tools support compliance; they don't replace your processes. Use the checklist above whichever provider you choose.
Frequently asked questions
Does the DPDP Act apply to my business email?
Yes. If your mailboxes contain names, phone numbers, addresses, résumés, ID documents or any other information about identifiable people, that is personal data under the DPDP Act. The main duties for protecting it apply from 13 May 2027.
When does DPDP compliance become mandatory?
The main obligations, including security safeguards, breach reporting, retention, erasure and data principal rights, apply from 13 May 2027. That is 18 months after the DPDP Rules were notified on 13 November 2025. Penalties apply from the same date.
Does DPDP apply to small businesses and startups?
Yes. The DPDP Act has no general exemption based on company size. The government can notify narrow exemptions for certain startups, but most small businesses should plan as if every duty applies to them.
Is Google Workspace, Microsoft 365 or Zoho Mail DPDP compliant?
No email product is DPDP compliant by itself. Compliance is your business's responsibility as the data fiduciary. A provider can supply the controls you need, such as security settings, log retention, retention policies and a processing agreement, but you must configure and use them.
Is a hacked email account a data breach under DPDP?
Yes, if the mailbox contained personal data and someone accessed it without authorisation. You must inform affected people and the Data Protection Board, with full details to the Board within 72 hours.
How long should a business keep emails under DPDP?
Keep sign-in, traffic and processing logs for at least one year. Keep other personal data only as long as its purpose requires, or longer if another law such as tax law requires it. Then erase it.
Does DPDP require email to be hosted in India?
Not in general. Transfers abroad are allowed except to countries the government restricts. However, RBI-regulated entities, government departments and PSUs often face stricter sector rules that require India-hosted or on-premise email.
What is the penalty for not complying with DPDP?
Up to ₹250 crore for failing to take reasonable security safeguards, and up to ₹200 crore for failing to report a breach. Other violations carry lower maximum penalties. The Data Protection Board decides the amount in each case.
What should we do first?
Turn on two-factor authentication for all users, check how long your provider keeps logs, and write a retention policy for HR and support mailboxes. These three steps reduce most of your risk and can be done within a week.
Conclusion
DPDP compliance can look like a legal project full of notices, consent flows and audits. For most Indian businesses, though, the fastest way to cut real risk is in email. That's where personal data piles up unnoticed, where a single stolen password can trigger a reportable breach, and where a few setting changes make the biggest difference.
You don't need to finish everything this month. You do need to start. This week:
- Turn on two-factor authentication for every user.
- Ask your provider how long it keeps logs, and whether it will sign a data processing agreement.
- Write a retention policy for your HR and support mailboxes.
The rest of the checklist can follow over the coming months. Six and a half months is enough time if you begin now. It won't be if you wait until April.
Whichever provider you use, the duty to protect the people in your inbox is yours. If you'd like help getting there, we're happy to look at your setup with you.
See DPDP-ready email plans

















Sign in to leave a comment.