
Data Center Security is arguably the single most consequential infrastructure investment a UAE enterprise makes. Every transaction processed by a DIFC trading platform, every patient record held inside a DHA-regulated hospital network, and every stream of production telemetry moving through an ADNOC upstream facility ultimately resides in, or passes through, a Data Center. The physical and cyber integrity of that facility is not a back-office IT concern — it is a board-level business continuity question.
The UAE has become the Middle East's pre-eminent digital infrastructure hub, hosting a dense concentration of Tier III and Tier IV carrier-neutral colocation facilities, hyperscale points of presence, and private enterprise data halls. That concentration of high-value data makes the country an increasingly attractive target for nation-state actors, ransomware syndicates, and insiders — often at the same time. Enterprises that treat facility protection as a one-off checklist rather than a continuously evolving discipline are, in effect, one incident away from regulatory sanction, reputational damage, and operational paralysis.
This guide sets out the architecture, technologies, and regional compliance considerations that define best-in-class facility defence for UAE organisations — from the perimeter fence to the hypervisor layer.
Data Center Perimeter Security: The First Line of Defence
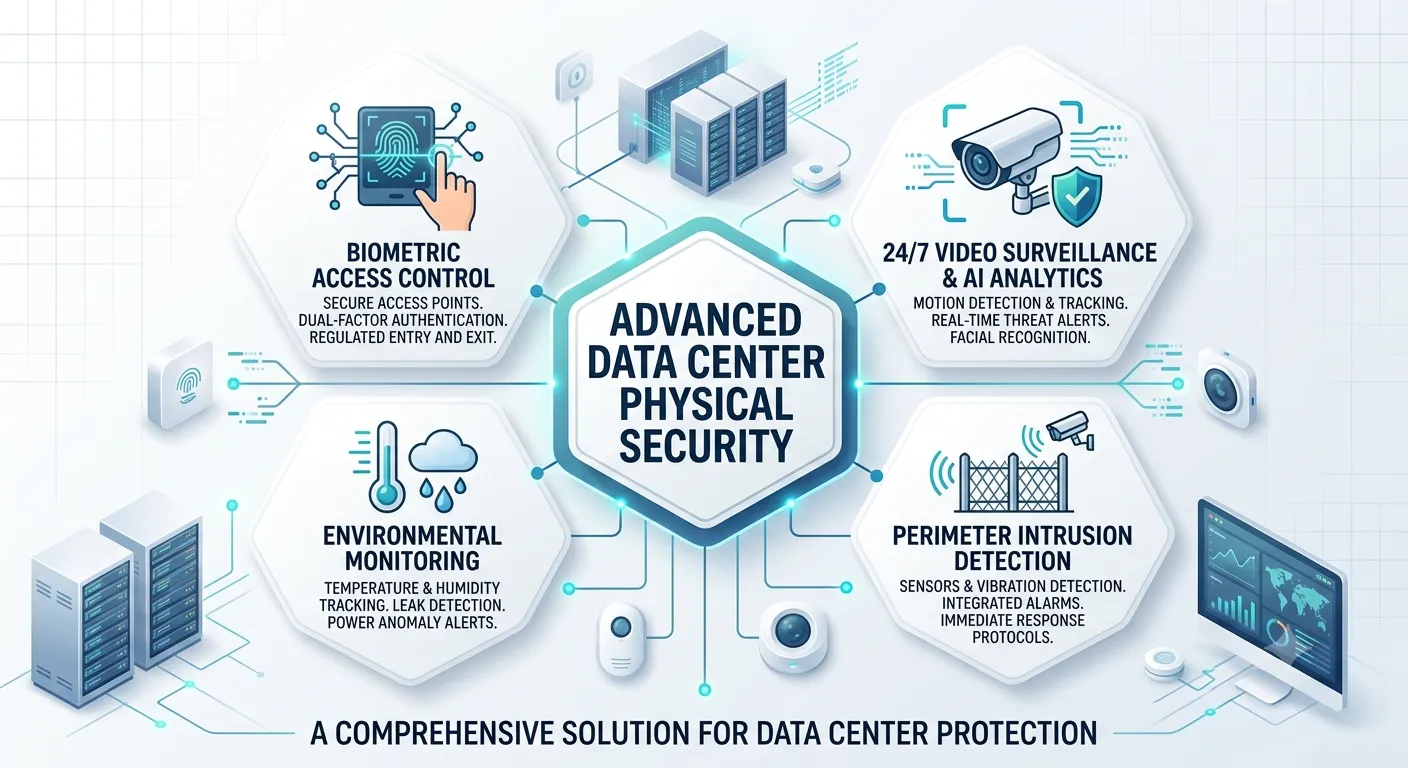
Data Center Perimeter Security is the outermost ring of protection standing between a facility and the outside world — and it is where most real-world intrusion attempts are stopped before they ever reach a server rack. A well-engineered perimeter combines physical deterrence with continuous, intelligent monitoring rather than relying on a single fence line or guard post.
A best-practice deployment typically layers several independent controls so that no single point of failure can compromise the whole site:
• Anti-ram bollards, vehicle barriers, and hostile-vehicle mitigation at all site entry points
• Perimeter intrusion detection using fibre-optic fence sensors, ground radar, and thermal imaging cameras
• AI-based video analytics that distinguish genuine intrusion attempts from wildlife, weather, or passing traffic to reduce false-positive alarm fatigue
• Mantrap and airlock entry systems that prevent tailgating into the building envelope
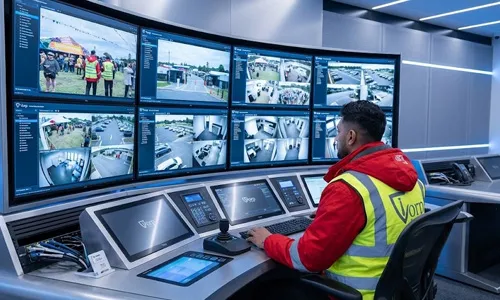
• Integration of perimeter alarms directly into the facility's central security operations centre for real-time response
Choosing the Right Data Center Perimeter Security Solution
Not every facility needs the same countermeasures, which is why a genuinely effective Data Center Perimeter Security Solution is engineered around a site-specific risk assessment rather than a generic product catalogue. Factors such as the facility's proximity to public roads, its tenant mix, its regulatory classification, and its threat profile all shape which combination of bollards, sensors, cameras, and access barriers deliver the best return on investment. Tektronix LLC begins every perimeter engagement with a formal site survey and threat modelling exercise before a single component is specified.
Data Center Threat Detection: Knowing What You Are Actually Defending Against
Effective Data Center Threat Detection starts with a clear-eyed understanding of the adversary. UAE facilities face a threat matrix that is broader and more sophisticated than in most other regions, shaped by the country's geopolitical position, its role as a global financial gateway, and the sheer density of high-value data concentrated within its borders.
The primary threat categories confronting UAE facility operators include:
•Advanced Persistent Threats (APTs) — state-sponsored actors conducting long-dwell reconnaissance against government, energy, and financial sector targets
•Ransomware-as-a-Service (RaaS) syndicates — encrypting production workloads and demanding cryptocurrency ransoms, with average demand values in the Gulf region exceeding USD 4.5 million per incident
•Supply chain infiltration — compromising hardware or software components upstream of installation to establish covert persistence
•Insider threats — privileged employees, contractors, or third-party maintenance engineers exploiting physical or logical access
•Physical intrusion — targeted theft of storage media, hardware implantation, or sabotage of cooling and power infrastructure
•DDoS amplification attacks — exploiting UAE's high-bandwidth transit capacity to overwhelm internet-facing services
A detection framework that cannot identify and respond to all six categories at once provides only the illusion of security.
Data Center Firewalls: The Critical First Cyber Layer
Data Center Firewalls bear little resemblance to the stateful packet-inspection engines that defined network security a decade ago. Today's enterprise-grade platforms combine next-generation firewall (NGFW) capability — deep packet inspection, application-layer visibility, TLS/SSL decryption, and user-identity awareness — with AI-driven threat intelligence feeds that update signatures in near real time.
North-south and east-west traffic segmentation
The most damaging breaches of recent years, including attacks on Gulf Cooperation Council (GCC) critical infrastructure, exploited the relative flatness of internal networks. Once a single endpoint was compromised, lateral movement across the east-west traffic plane went largely unimpeded. A properly designed firewall architecture enforces micro-segmentation between every workload tier — web, application, database, management, and storage — so a compromise in one zone cannot cascade into another.
Facilities hosting internet-facing services need purpose-built DDoS mitigation, whether through on-premise scrubbing appliances or upstream cloud-based services capable of absorbing volumetric attacks measured in terabits per second. Integration with UAE-based Internet Exchange Point (UAE-IX) scrubbing infrastructure adds a layer of domestic traffic cleaning that reduces latency impact during active mitigation.
Zero-trust network architecture
The zero-trust model — never trust, always verify — is rapidly becoming the default architecture for UAE government and regulated-sector facilities. Under zero-trust principles, every connection request, whether from an internal server, a remote administrator, or a third-party service, is authenticated, authorised, and encrypted regardless of where it originates. This approach aligns with NIST SP 800-207 and the guidance issued by the UAE Cybersecurity Council.
Data Center Encryption: Making Stolen Data Useless
Data Center Encryption is the foundational control that renders stolen data operationally worthless to an adversary. A comprehensive strategy addresses three distinct data states, each with its own technology and key-management discipline.
Encryption at rest
All storage media — SAN/NAS arrays, backup tapes, and decommissioned drives — should be protected with AES-256 encryption managed through a Hardware Security Module (HSM). For UAE government and financial sector facilities, HSMs are typically expected to be FIPS 140-2 Level 3 or Level 4 validated, a requirement referenced in the UAE Information Assurance Standards published by the UAE Cybersecurity Council.
Encryption in transit
All data moving across internal networks — storage replication traffic, management-plane communications, and inter-application API calls — should run over TLS 1.3 or IPSec tunnels. Legacy TLS 1.0/1.1 and unencrypted protocols such as Telnet, FTP, and HTTP need to be formally decommissioned, a gap that routinely surfaces in CBUAE technology risk examinations and NESA compliance assessments.
Encryption in use — confidential computing
The emerging frontier of confidential computing — using Intel TDX, AMD SEV-SNP, or ARM Confidential Compute Architecture to encrypt data even while it is being actively processed in CPU memory — is gaining traction among UAE financial institutions and healthcare operators who need to protect sensitive workloads from the hypervisor layer itself.
Cybersecurity for Data Center Environments: A Defence-in-Depth Framework
Cybersecurity for Data Center environments cannot be achieved through point products alone — it requires a coherent, layered architecture in which each control compensates for the limitations of the ones above and below it. A seven-layer framework aligned with the CIS Critical Security Controls v8 and the UAE National Cybersecurity Authority Essential Cybersecurity Controls typically covers:
1.Perimeter security — NGFW, IPS/IDS, DDoS mitigation, and web application firewalls (WAF)
2.Network segmentation — micro-segmentation, VLANs, and software-defined networking (SDN) policy enforcement
3.Identity and access management — privileged access management (PAM), multi-factor authentication, and just-in-time access provisioning
4.Endpoint and server hardening — CIS benchmark-aligned OS hardening, EDR/XDR agents, and automated patch management
5Data protection — HSM-managed encryption, DLP policy enforcement, and immutable backup storage
6.Security monitoring — SIEM correlation, UEBA, and a 24/7 Security Operations Centre with sub-15-minute mean time to detect
7.Incident response — pre-agreed playbooks, regular tabletop exercises, and recovery time objectives aligned to business continuity plans
Integrated Data Center Solutions: Converging Physical and Cyber Defence
The most resilient facilities are the ones where physical security and cybersecurity are designed as a single converged system rather than two separate budgets. End-to-end Data Center Solutions bring mantrap entry systems, biometric access control, CCTV analytics, environmental monitoring, firewalls, encryption, and SIEM correlation into one unified operating picture — so a badge swipe, a server login, and a camera alert can all be cross-referenced against the same timeline during an investigation.
This convergence is what allows a security team to answer the question that matters most during an incident: not just what happened on the network, but who was physically present in the building at the time. All physical access events feed into the centralised SIEM platform, correlating physical presence with logical system access — a capability that is essential for detecting insider threats and supporting post-incident forensics.
Data Center Security UAE: The National Compliance Landscape
Operating a facility in the UAE means navigating a multi-layered compliance landscape. Data Center Security UAE-wide requirements are shaped by a combination of federal legislation, emirate-level authority mandates, and sector-specific regulatory frameworks:
•UAE Cybersecurity Law (Federal Decree-Law No. 34 of 2021) — establishes baseline cybersecurity obligations for critical information infrastructure operators
•UAE Personal Data Protection Law (PDPL — Federal Decree-Law No. 45 of 2021) — governs data processing, residency, and breach notification for facilities handling personal data
•CBUAE Cyber Risk Management Framework — prescribes security architecture and incident response requirements for licensed financial institutions
•NESA UAE Information Assurance Standards — a comprehensive controls framework applicable to government and strategic sector facilities
•Dubai Electronic Security Centre (DESC) Cloud and Data Classification Standards — applies to Dubai government entities and their hosting providers
•Abu Dhabi Digital Authority (ADDA) ICT Security Policy — governs Abu Dhabi government entity facility security posture
A dedicated compliance advisory exercise maps a client's environment against all applicable frameworks, identifies control gaps, and delivers a prioritised remediation roadmap — ensuring security investment satisfies both operational needs and regulatory obligation at the same time.
Data Center Security Dubai: Protecting the Middle East's Digital Capital
Dubai hosts the highest concentration of Tier III and Tier IV facility capacity in the Arab world, with sites operated by du, Etisalat (e&), Khazna, Gulf Data Hub, and multiple hyperscale edge nodes. Data Center Security Dubai deployments must address not only the technical requirements of individual facilities but also the interconnection security implications of operating inside this dense peering ecosystem.
Dubai Internet City, Dubai Silicon Oasis, and the DIFC financial district each impose additional security baseline requirements on operators and tenants within their jurisdiction. High-profile deployments linked to Dubai Future Foundation-affiliated entities and Smart Dubai initiative programmes have further raised the expected baseline, with AI-driven threat detection, automated compliance reporting, and zero-trust network architectures now treated as standard rather than advanced features.
Data Center Security Sharjah: Securing the Northern Emirates' Growing Digital Economy
Sharjah's emergence as a technology and innovation hub — anchored by Sharjah Research Technology and Innovation Park (SRTIP) and the Sharjah Publishing City free zone — is driving rapid growth in enterprise facility demand. Data Center Security Sharjah deployments serve a diverse client base spanning manufacturing, logistics, education, and government entities migrating workloads from on-premise server rooms into purpose-built colocation and private cloud environments.
The Northern Emirates more broadly — including Ajman, Ras Al Khaimah, Fujairah, and Umm Al Quwain — are benefiting from UAE Vision 2031 digital infrastructure investment that is expanding facility capacity beyond the traditional Dubai-Abu Dhabi corridor. A regional delivery capability across all seven emirates ensures organisations outside the capital corridor receive the same enterprise-grade security architecture and post-deployment support as flagship projects.
Why Tektronix LLC Is the UAE's Trusted Partner for Data Center Security
Tektronix LLC is a UAE-registered systems integrator and security consultancy with over a decade of documented expertise designing, deploying, and managing physical and cyber security programmes for enterprise facility environments. Our experience and authority credentials in this domain include:
• Certified security architects holding CISSP, CISM, CEH, and vendor-specific credentials from Palo Alto Networks, Fortinet, Cisco, and Thales
• A track record of delivering facility security projects for clients across BFSI, government, oil and gas, healthcare, and telecommunications verticals in the UAE
• Compliance advisory capability covering NESA, CBUAE, DESC, ADDA, UAE PDPL, and ISO 27001/IEC 27002 frameworks
• 24/7 managed security service (MSSP) capability with a UAE-based Security Operations Centre staffed by bilingual (Arabic/English) analysts
• Physical security integration spanning access control, CCTV, perimeter intrusion detection, and environmental monitoring — all converged with cyber defence platforms
Conclusion
The stakes of inadequate Data Center Security have never been higher for UAE enterprises. As the region's digital economy expands, its facilities attract a commensurate rise in threat actor attention — from ransomware operators chasing financial gain to sophisticated state-sponsored actors pursuing strategic intelligence. The organisations that emerge from this threat environment unscathed are the ones that treat facility protection not as a project with a completion date, but as a continuously evolving programme aligned with the threat landscape, the regulatory environment, and their industry's operational realities.
From next-generation firewalls and encryption key management to perimeter security and 24/7 SOC monitoring, every layer of a well-designed architecture plays an indispensable role. Cutting a corner on any single layer creates the vulnerability an adversary will eventually find. The question for UAE decision-makers is not whether to invest in comprehensive facility protection — it is whether to act before or after a breach forces the decision.
Tektronix LLC is ready to guide UAE enterprises from wherever they stand today toward a resilient, compliant, and continuously monitored security posture. Learn more about our approach to Data Center Perimeter Security Solutions — the conversation starts with an honest assessment.
FAQS
1. What is the difference between physical and cyber data center security, and do I need both?
Physical security governs who can physically enter the facility and interact with hardware — perimeter fencing, access control, CCTV, and environmental monitoring. Cybersecurity governs who can access data and systems through logical means — firewalls, encryption, identity management, and threat detection. The two are inseparable: a flawless cyber architecture can be defeated by uncontrolled physical access, and impenetrable physical security cannot stop a remote ransomware attack. UAE enterprises need an integrated approach that treats both as a single converged discipline.
2. Which UAE regulatory frameworks apply to my data center security programme?
The applicable frameworks depend on your sector and emirate of operation. Federal obligations that apply to all UAE entities include the UAE Cybersecurity Law and the UAE PDPL. Sector-specific frameworks include the CBUAE Cyber Risk Management Framework for financial institutions, HAAD and DHA standards for healthcare operators, and sector-specific frameworks for energy participants. Dubai-based operators must also comply with DESC standards, while Abu Dhabi entities are governed by ADDA ICT Security Policy. A compliance mapping exercise identifies all applicable frameworks and gaps against your current posture.
3. How often should a data center security assessment be conducted?
Industry best practice, and several UAE regulatory frameworks, recommend a comprehensive assessment at least annually, supplemented by quarterly vulnerability scanning and continuous automated monitoring. A full assessment should also be triggered by any significant change to the facility's infrastructure, network architecture, or threat landscape. Penetration testing of both physical controls and cyber defences should be conducted at least once per year by an independent, certified third party.
4. What is zero-trust architecture and is it relevant to UAE data centers?
Zero-trust architecture eliminates the concept of inherent trust for any user, device, or network segment, requiring continuous verification of identity and authorisation for every access request regardless of whether it originates inside or outside the traditional network perimeter. It is highly relevant to UAE facilities because it directly addresses the lateral-movement attack patterns used in the GCC's most damaging breaches, and it is increasingly referenced in government and financial sector procurement requirements.
5. How long does it take to deploy a comprehensive data center security solution?
A comprehensive deployment typically follows a five-phase methodology: discovery and risk assessment (two to three weeks); architecture design and solution specification (two to four weeks); procurement and staging (three to six weeks depending on hardware lead times); implementation and integration (four to twelve weeks depending on scope); and testing, commissioning, and staff training (two to three weeks). The full cycle for an enterprise engagement typically runs three to six months, with milestone-based reporting and clear acceptance criteria at each phase gate.
For more information contact us on:
Tektronix Technology Systems Dubai-Head Office
+971 50 814 4086
+971 55 232 2390
Office No.1E1 | Hamarain Center 132 Abu Baker Al Siddique Rd – Deira – Dubai P.O. Box 85955














Sign in to leave a comment.