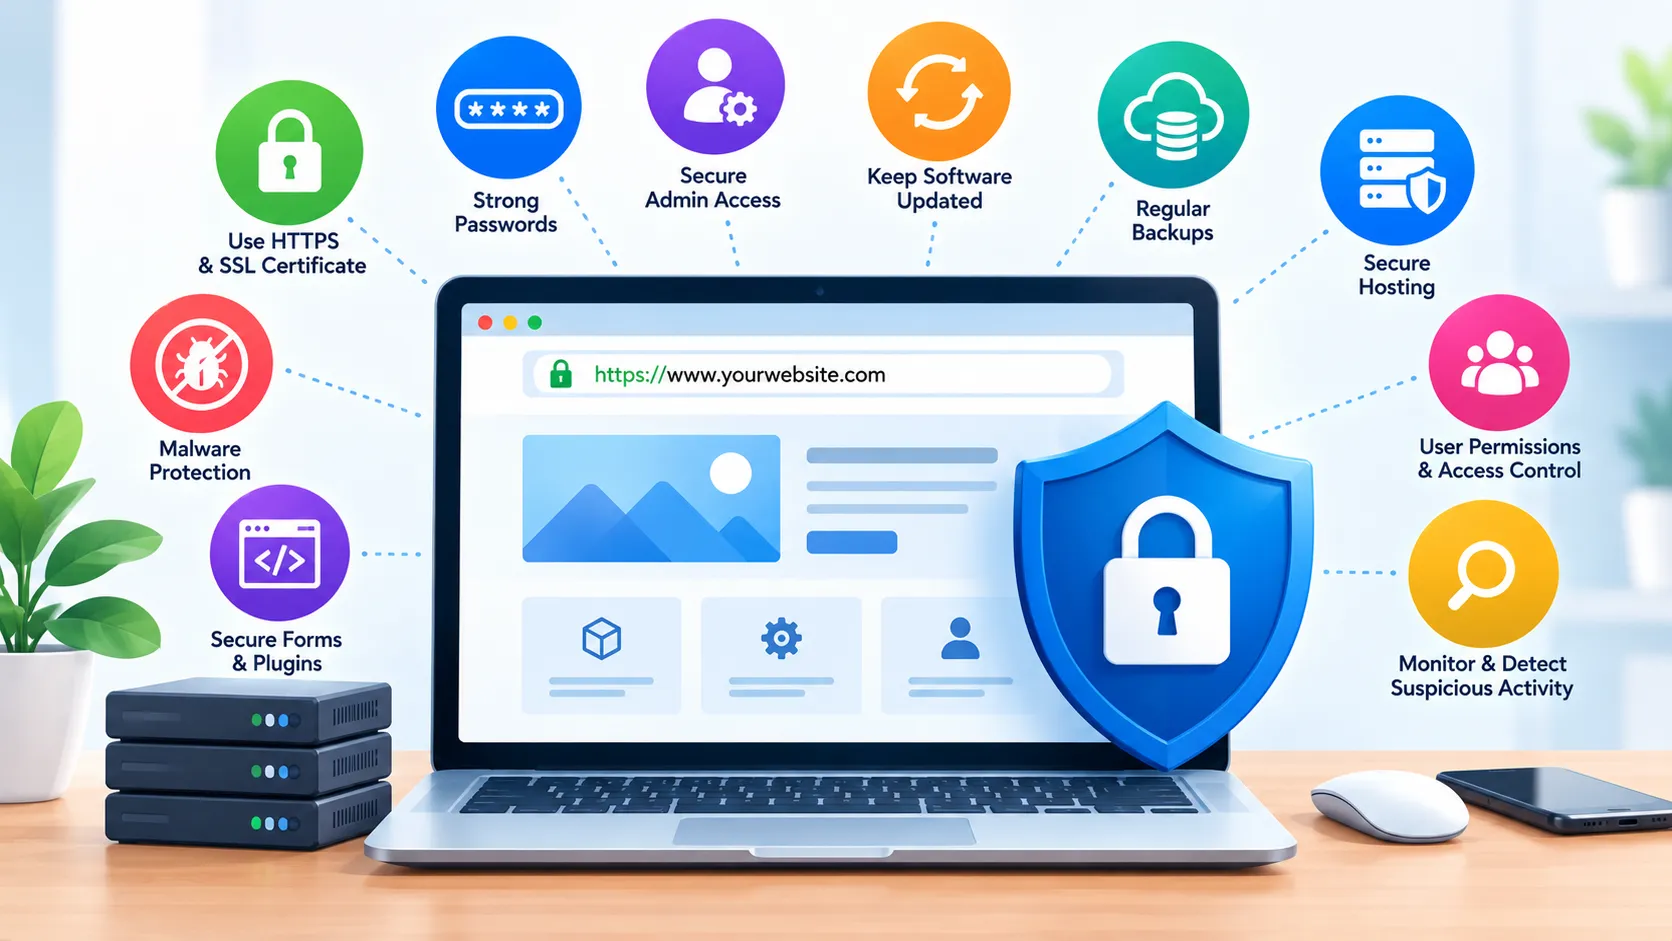


Quick Answer: To secure a business website, you should use HTTPS, keep software updated, create regular backups, use strong passwords, protect administrator accounts, choose secure hosting, monitor suspicious activity, and regularly check for vulnerabilities. Website security should be considered during development as well as ongoing maintenance.
Why Is Website Security Important for Businesses?
A security problem can affect more than just the website. A compromised website may become unavailable, display unauthorized content, expose sensitive information, or damage customer trust.
For ecommerce websites, security is particularly important because the website may process customer accounts, orders, payments, and other sensitive information. Service businesses should also protect contact forms, administrator accounts, databases, and other business information.
A proactive security approach can help identify and address potential problems before they become more serious.
1. Use HTTPS and an SSL/TLS Certificate
One of the basic steps toward securing a website is using HTTPS.
HTTPS encrypts information exchanged between a visitor's browser and the website. This is particularly important when visitors submit contact information, log in to an account, or make a payment.
Businesses should ensure that their SSL/TLS certificate is correctly configured and remains valid. An HTTPS-enabled website also provides visitors with a more trustworthy browsing experience.
2. Use Strong Passwords
Weak passwords can create unnecessary security risks.
Website administrators should use long, unique passwords rather than simple combinations that are easy to guess. Passwords should not be reused across multiple platforms.
Where supported, businesses should also use a password manager and multi-factor authentication to add another layer of protection to important accounts.
3. Protect Administrator Accounts
Administrator accounts have access to important website settings and should therefore be protected carefully.
Businesses should limit administrator access to people who genuinely need it. Unused accounts should be removed or disabled, and each team member should ideally have an appropriate individual account rather than sharing one administrator password.
Reducing unnecessary access can help limit the potential impact of a compromised account.
4. Keep Website Software Updated
Outdated software can create security and compatibility problems.
Businesses should regularly update their CMS, plugins, themes, frameworks, libraries, and other website components when appropriate. Software updates may include security fixes, bug fixes, and improvements.
However, updates should be handled carefully. A backup and appropriate testing process can help identify compatibility problems before they affect the live website.
5. Create Regular Website Backups
Backups are an important part of a website security strategy.
If a website experiences a serious technical problem, data loss, or security incident, a recent backup can provide a way to restore the website.
The appropriate backup frequency depends on how often the website changes. A frequently updated ecommerce website may need a more frequent backup strategy than a simple business website.
Backups should also be stored securely and tested periodically to confirm that they can actually be restored when required.
6. Choose Secure Website Hosting
Hosting infrastructure can affect website security as well as performance.
Businesses should choose a hosting environment that provides appropriate security controls, reliable infrastructure, regular backups where applicable, and technical support.
Hosting requirements can vary according to website size and functionality. An ecommerce website, for example, may have different security requirements from a basic informational website.
When comparing Web Development Packages, businesses should understand whether hosting is included and what level of security and technical support is provided.
7. Secure Website Forms
Contact forms, enquiry forms, registration forms, and other input fields can become targets for spam and malicious activity.
Businesses should use appropriate validation and security measures to protect forms. Spam protection can also help prevent large amounts of unwanted submissions.
Forms should be tested regularly to ensure that they remain functional while protecting the website from inappropriate or suspicious input.
8. Monitor for Malware and Suspicious Activity
Regular monitoring can help identify unusual website behavior.
Businesses should watch for unexpected changes to website files, unfamiliar administrator accounts, unauthorized content, unusual login attempts, or other suspicious activity.
Security monitoring tools can help identify potential problems, but businesses should also have a process for responding to security alerts.
Early detection can make it easier to investigate and address a security issue.
9. Keep Plugins and Third-Party Tools Under Control
Plugins and third-party tools can add useful functionality to a website, but every additional component can introduce another element that needs to be maintained.
Businesses should regularly review installed plugins, extensions, scripts, themes, and integrations. Unused components should be removed when appropriate.
Only trusted and properly maintained components should be used, and they should be updated when suitable updates are available.
10. Use Proper User Permissions
Not every person working on a website needs complete administrator access.
Businesses should assign permissions according to each user's responsibilities. For example, someone responsible only for publishing content may not need access to technical settings or sensitive administrative functions.
Limiting permissions can reduce the potential impact if one account becomes compromised.
11. Keep the Website and Server Configuration Secure
Website security is not limited to the visible pages.
Server configuration, databases, file permissions, access controls, security headers, software versions, and other technical settings can also affect security.
These areas may require professional technical knowledge, particularly for custom websites or websites running complex applications.
Businesses should therefore ensure that security requirements are considered during development and reviewed during ongoing maintenance.
12. Perform Regular Security Checks
Website security should be reviewed regularly rather than only after a problem occurs.
A security review can include checking software updates, administrator accounts, passwords, backups, SSL configuration, plugins, hosting settings, suspicious activity, and other relevant areas.
Regular checks can also help businesses identify outdated components or unnecessary access before they become larger concerns.
Website Security for Ecommerce Businesses
Ecommerce websites require additional attention because they may process customer accounts, orders, addresses, payments, and other sensitive information.
Businesses should use secure payment providers, HTTPS, appropriate access controls, updated software, secure hosting, backups, and monitoring.
Payment information should be handled through appropriate payment systems rather than unnecessarily stored on the website.
Ecommerce businesses should also regularly test checkout functionality and security-related configurations.
How Web Development Packages Can Affect Website Security
Security should be one of the factors considered when comparing Web Development Packages.
Businesses should ask whether the package includes HTTPS configuration, secure development practices, software updates, backups, security monitoring, access management, and post-launch support.
A package that focuses only on design and basic functionality may not provide the same level of ongoing security support as a more comprehensive development and maintenance arrangement.
However, security requirements depend on the website's technology, functionality, data, and business needs. Businesses should discuss these requirements with the development team before starting the project.
Website Security vs Website Maintenance
Website security and website maintenance are closely connected, but they are not exactly the same.
Security focuses on protecting the website and its users from unauthorized access, vulnerabilities, malware, and other threats. Maintenance is broader and may include security updates along with backups, content updates, performance optimization, broken-link checks, and technical improvements.
Regular maintenance can therefore support a stronger overall security strategy.
Common Website Security Mistakes
One of the most common mistakes is using weak or reused passwords for administrator accounts. Another is leaving outdated plugins, themes, or software installed for long periods.
Businesses may also fail to create reliable backups or assume that a backup exists without testing whether it can actually restore the website.
Sharing administrator credentials, giving excessive user permissions, ignoring security alerts, and using unnecessary third-party components can also increase security risks.
Another mistake is waiting until a website has been compromised before taking security seriously.
Website Security Checklist
Before launching or maintaining a business website, review the following:
- HTTPS and SSL/TLS configuration
- Strong administrator passwords
- Multi-factor authentication where available
- Limited administrator access
- Updated CMS and software
- Updated plugins and themes
- Regular backups
- Secure hosting
- Protected website forms
- Malware and activity monitoring
- Appropriate user permissions
- Secure server configuration
- Regular security reviews
The exact security measures required will depend on the website's technology, size, functionality, and the type of information it handles.
Conclusion
Learning how to secure a business website is an important part of responsible website management. Security should be considered from the beginning of development and maintained throughout the website's lifecycle.
Using HTTPS, strong passwords, secure hosting, regular backups, updated software, protected forms, controlled user access, and ongoing monitoring can help businesses reduce common security risks.
When selecting Web Development Packages, businesses should look beyond design and functionality and understand what security measures and post-launch support are included.
A secure website requires ongoing attention. Regular maintenance and security checks can help businesses protect their website, support customer trust, and keep important online services running reliably.
Want to build or secure your business website? Get in Touch with our team to discuss your website development and security requirements.
Frequently Asked Questions
How can I secure a business website?
Start with HTTPS, strong passwords, secure administrator accounts, regular backups, updated software, secure hosting, protected forms, and regular security monitoring.
Is an SSL certificate enough to secure a website?
No. HTTPS is an important security measure, but website security requires multiple layers, including software updates, access controls, backups, secure hosting, monitoring, and other appropriate protections.
How often should website security be checked?
Security should be monitored regularly, while important updates and vulnerabilities should be addressed as soon as reasonably possible. The exact schedule depends on the website's technology and risk level.
Why are website backups important for security?
Backups provide a recovery option if a website experiences data loss, a serious technical problem, or certain types of security incidents.
Can plugins affect website security?
Yes. Poorly maintained, outdated, or unnecessary plugins can introduce security and compatibility risks. Businesses should regularly review and update website components.





















Sign in to leave a comment.