
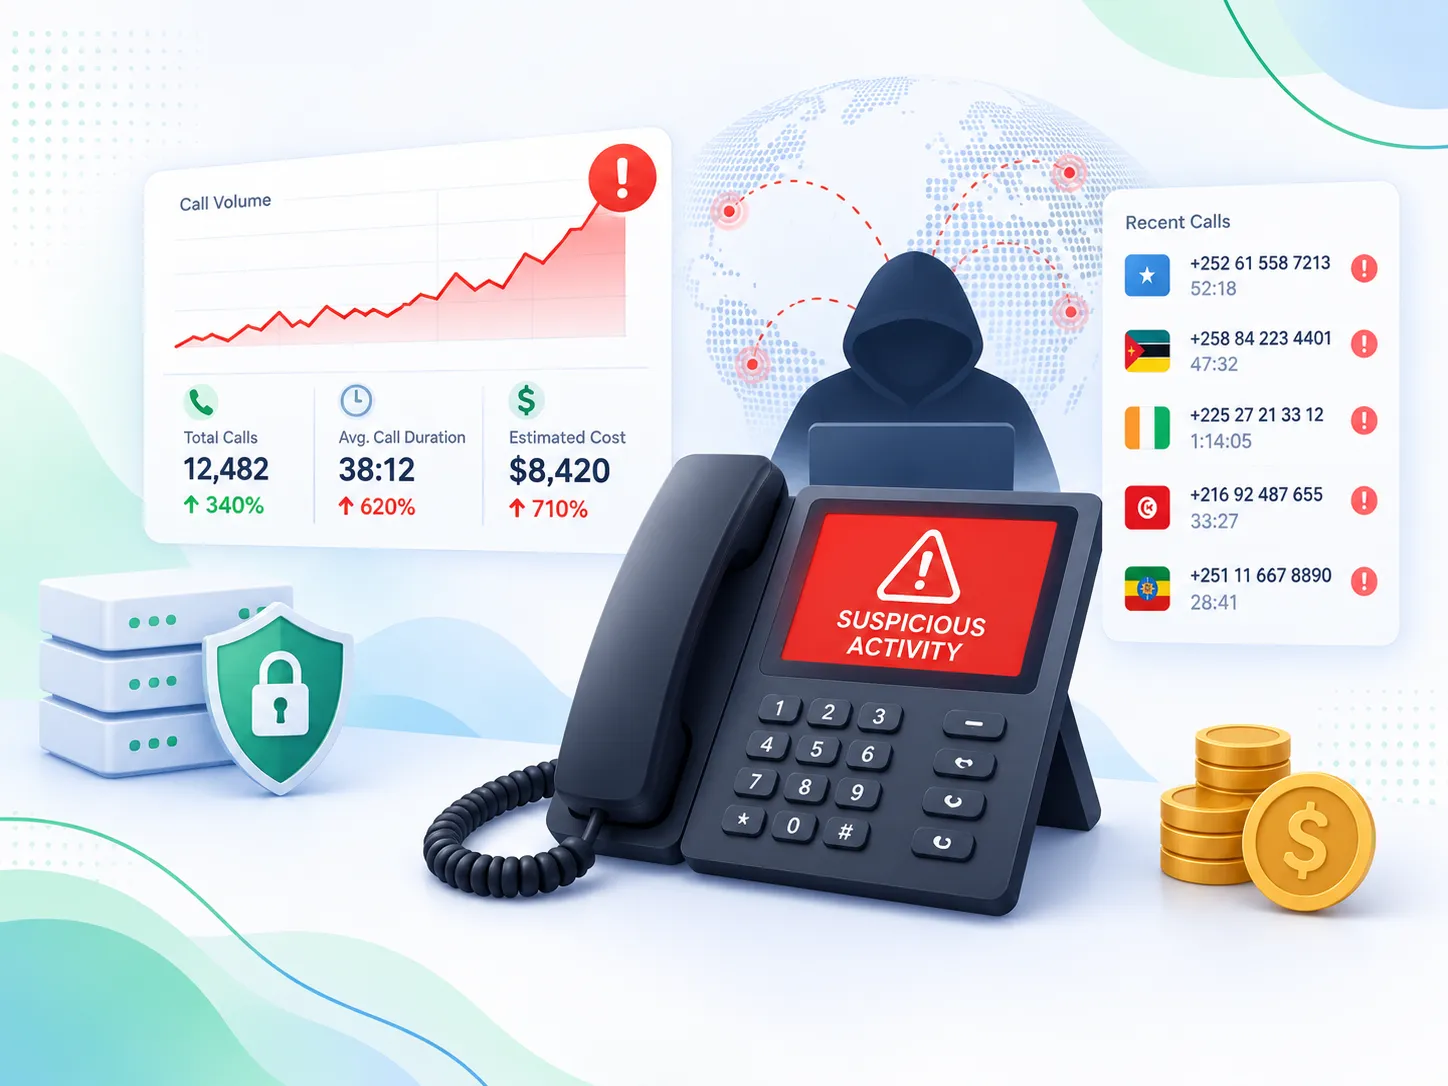
Most toll fraud is not discovered while it is happening. It is discovered later, when the bill shows up. That is the whole problem. The attack ran quietly all weekend, the calls connected, and by Monday the money is already gone.
But here is the thing. It is not actually invisible while it is happening. The signs are sitting right there in your call activity the entire time. The catch is that somebody has to be looking, and most of the time nobody is. So if you run a VoIP or SIP platform, these are the patterns worth knowing, because catching one of them early is the difference between a scare and a disaster.
A sudden spike in call volume
The most obvious sign, and the easiest to miss if you are not watching. Your call volume jumps well above normal for no reason you can explain. No campaign, no busy season, just a surge. Especially when it is outbound, and especially when it is international, that is worth stopping to look at straight away.
Calls to places you never call
Toll fraud, and IRSF in particular, runs on expensive destinations. Premium-rate numbers, obscure international prefixes, small countries with high termination costs. If your call logs suddenly show traffic to places your business has no reason to ever dial, that is a red flag, not a curiosity.
A pile of calls all at once
Fraudsters do not make one call at a time. They run as many parallel calls as your system allows, because they are trying to burn billable minutes as fast as possible before anyone reacts. So a single account suddenly placing dozens of simultaneous calls is a classic signature. Legitimate use almost never looks like that.
Activity at strange hours
There is a reason these attacks tend to kick off on a Friday night. Nobody is watching over the weekend. So one of the strongest signals is simply timing. A burst of calls at 3am on a Sunday, when your actual business is closed, deserves immediate suspicion. Real traffic follows your business hours. Fraud does not care about them.
A spike in failed logins
This one shows up before the attack rather than during it, which makes it your early warning. Attackers run automated scanners that hammer your SIP service trying to guess credentials. If your logs show a sudden flood of failed registration attempts, someone is testing your doors. Catching that is a chance to lock things down before they actually get in.
What to do if you spot one
If any of these turn up, treat it as live until proven otherwise. Block the account or source involved, kill the active calls, and reset the credentials that may have been exposed. Then work out how it got in, because the same gap will get used again if you leave it open.
Honestly, though, the bigger lesson is not about reacting faster. It is about not needing to. The businesses that never get burned by toll fraud are usually the ones that set up real-time alerts on exactly these patterns, so a spike pings a human the moment it starts, not the moment the invoice arrives. Add sensible dialing limits and spend caps on top of that, and most attacks get stopped before they cost anything at all.
If you want the full picture, there is a detailed guide on how to stop toll fraud and IRSF on SIP platforms that covers the detection signals, the layered VoIP security controls, and exactly what to do during an active attack. Teams like Hire VoIP Developer handle this kind of hardening day to day.
Toll fraud is quiet, but it is not silent. The signals are there the whole time. The only real question is whether anyone is watching for them before the bill lands.






















Sign in to leave a comment.