
Introduction
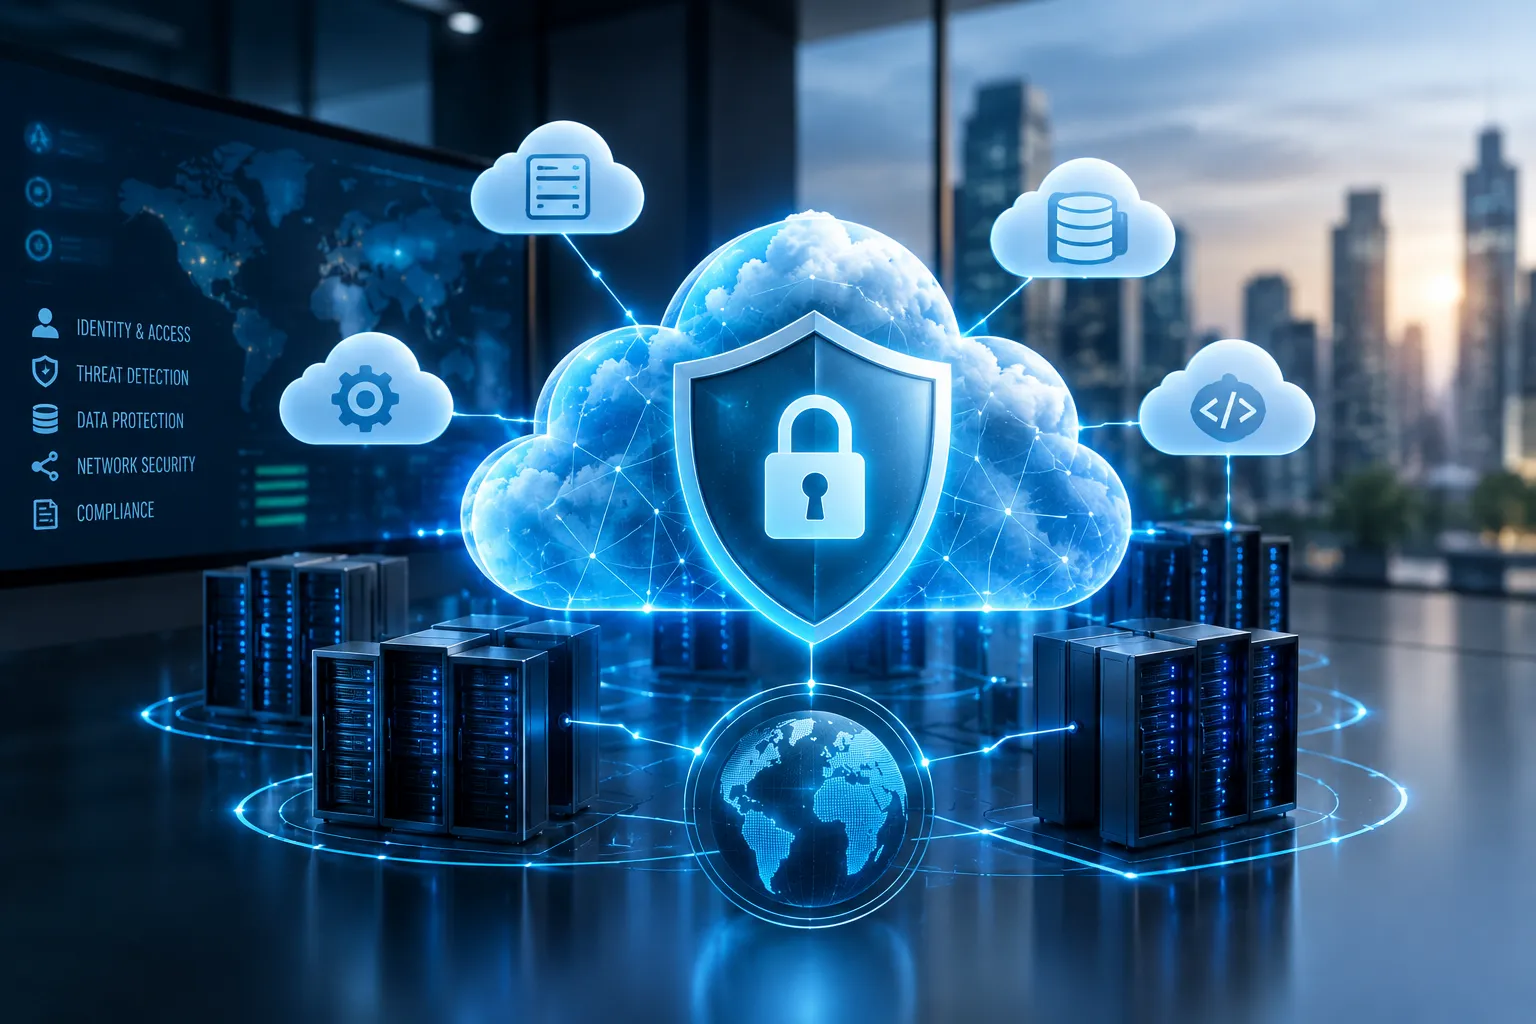
In an era of rapid digital transformation, maintaining strong cybersecurity for enterprises is no longer just a functional requirement for the IT department. It has transformed into a fundamental business metric that dictates operational resilience, brand reputation, and corporate longevity. Modern organizational networks have grown beyond traditional physical perimeters, stretching across multi-cloud environments, remote work forces, and interconnected third-party service providers. As these digital ecosystems become more sprawling and complex, the attack surface expands alongside them. Legacy protection tools and static perimeter defenses are no longer sufficient to stop modern, dynamic threats. To survive in today's threat environment, organizations must rethink how they protect sensitive information, secure critical infrastructure, and build long-term organizational resilience.
Evolution of Threats Facing Large Organizations
The modern threat landscape is moving faster and growing more sophisticated than ever before. Adversaries are leveraging sophisticated automated tools, rapid machine learning algorithms, and organized cybercrime networks to target core systems. Corporate data breaches and automated ransomware operations have shown that no organization is immune, regardless of industry or size.
A primary challenge in establishing effective cybersecurity for enterprises involves securing complex hybrid environments. Legacy approaches relied heavily on firewalls to guard a well-defined internal network. However, with data flowing across software-as-a-service platforms, private servers, and mobile endpoints, the perimeter has functionally vanished. Threat actors exploit these sprawling access points using advanced credential theft, supply chain exploits, and identity deception techniques, making early detection and rapid mitigation crucial.
Zero Trust Architecture and Identity Protection
Because physical and network boundaries no longer guarantee safety, modern security architecture relies on continuous verification. Adopting a Zero Trust framework means operating under the strict assumption that every internal and external request could be compromised until explicitly proven otherwise.
Instead of trusting devices simply because they sit inside a network, a strong identity-centric strategy demands rigorous authentication at every access request. Enforcing granular access management ensures that users receive only the absolute minimum system rights needed to fulfill their job roles. Combining granular permissions with continuous risk scoring and multi-factor authentication prevents compromised credentials from granting lateral movement across an enterprise network.
Artificial Intelligence in Cyber Defense Operations
The rapid deployment of automated tools across security platforms has changed how security operations centers function. Defense teams must analyze massive amounts of telemetry, logs, and user activity data across diverse platforms every single minute. Manual oversight of this scale is no longer practical.
Integrating intelligence-driven threat detection allows organizations to analyze vast streams of operational data in real time, identifying subtle anomalies that precede a major incident. Automated response playbooks can immediately isolate compromised endpoints, revoke access tokens, or quarantine suspicious payloads before human analysts even review the alert. This speed drastically reduces dwell time and mitigates potential financial or operational loss.
Cultivating an Internal Security Culture
Technology alone cannot completely protect an enterprise. The human element remains one of the most frequently targeted entry points for external attackers. Sophisticated social engineering and executive impersonation techniques often bypass technical controls by exploiting human trust and routine workflows.
Building effective cybersecurity for enterprises requires establishing a resilient security culture across every organizational department. Security awareness should extend beyond annual compliance sessions, morphing into continuous, real-world educational initiatives. Employees who understand risk indicators, spot unauthorized access attempts, and quickly report anomalous activity serve as an invaluable first line of defense. When every team member takes personal ownership of digital safety, the overall posture of the organization becomes significantly stronger.
Operational Resilience and Continuous Governance
A resilient enterprise strategy acknowledges that complete immunity from cyber incidents is impossible. True operational readiness is measured not just by an organization's ability to block inbound attacks, but by its capacity to maintain core operational continuity during and after an breach event.
Achieving long-term resilience requires integrating security governance directly into executive decision-making. Leadership must treat digital risk management with the same strategic weight as financial and operational risk. Regularly exercising incident response workflows, maintaining secure automated data backups, and constantly validating third-party supply chain risks ensure that an enterprise can quickly absorb disruption, isolate damage, and restore standard operations without compromising business continuity.
Key Takeaways
- Cybersecurity for enterprises requires a strategic shift from traditional perimeter defense to continuous, identity-driven protection.
- Implementing Zero Trust principles ensures that every user and device is authenticated continuously, drastically limiting lateral network movement.
- Automation and behavioral analytics are vital for processing modern threat telemetry and neutralizing incidents in real time.
- Fostering an ongoing, security-conscious corporate culture transforms employees into proactive assets against social engineering.
- Long-term success depends on framing security as a continuous business strategy integrated directly with executive risk governance.




















Sign in to leave a comment.