

Data Center Security has become a defining priority for hyperscale operators, colocation providers, and enterprise IT teams as the UAE cements its position as a regional digital infrastructure hub. With Dubai and Abu Dhabi attracting global cloud providers, financial institutions, and government cloud initiatives, the facilities housing this infrastructure face a threat landscape that spans everything from perimeter breaches to sophisticated network intrusions. This guide walks through the layered defenses UAE data center operators need, from the outer fence line to the server rack, and what to evaluate before the next infrastructure investment.

Why the UAE's Data Center Boom Demands Next-Level Security
The UAE's smart-city ambitions and its role as a regional connectivity hub have driven rapid growth in hyperscale, colocation, and enterprise data center capacity across Dubai and Abu Dhabi. This concentration of critical infrastructure, much of it supporting banking, government, and multinational corporate workloads, has raised the stakes for facility operators to adopt security postures that match the sensitivity of what they now house.
Dubai and Abu Dhabi's Growing Hyperscale and Colocation Market
Free zones and dedicated technology parks across both emirates have attracted major global cloud and colocation operators seeking a strategically located hub between Europe, Africa, and Asia. This growth has turned data center security from a specialized IT concern into a boardroom-level topic, since a single significant incident at a major facility could affect dozens of tenant organizations simultaneously.
Regional Compliance and Regulatory Drivers
Operators across the UAE increasingly need to align with frameworks such as ISO/IEC 27001, PCI DSS for financial workloads, and UAE Information Assurance guidance covering both government and critical infrastructure operators. These frameworks increasingly require documented physical controls, auditable access logs, and continuous monitoring, pushing facility owners toward integrated, standards-based protection strategies rather than fragmented, ad-hoc measures.
Cybersecurity for Data Center Environments: Where Physical Meets Digital
Modern threats rarely respect the line between the physical and digital domains, and UAE operators handling sovereign, financial, or multinational corporate data increasingly treat physical and network defense as a single, converged discipline rather than two separate departments. Security Operations Centers that correlate badge access events with network traffic anomalies can detect coordinated attacks — such as an unauthorized entry attempt paired with a credential-stuffing attempt on the network — far earlier than siloed systems ever could.
Perimeter Security: The First Line of Defense
Before an intruder ever reaches a building's front door, a well-designed facility has already layered fencing, vehicle barriers, and perimeter lighting to deter and delay unauthorized approach. This outer layer matters enormously for UAE facilities located within larger free zone or technology park campuses, where the property boundary itself — not just the building entrance — needs to be treated as the first meaningful checkpoint in the overall security design.
Data Center Access Control: Controlling Every Entry Point
This layer forms the physical checkpoint separating the data hall from the rest of the facility, combining biometric verification, multi-factor authentication, and mantrap vestibules to ensure only authorized IT and facilities staff reach server rooms. Layered credentialing — separating perimeter, building, and rack-level access — limits exposure even if a single credential is compromised, and generates an auditable trail for compliance reviews.
Data Center Surveillance: Round-the-Clock Visual Monitoring
High-resolution CCTV combined with AI-driven video analytics monitors perimeters, loading docks, and internal corridors around the clock, extending well beyond the building itself to cover parking areas and vehicle checkpoints across the wider property. Analytics-enabled cameras can flag loitering, tailgating, or unusual movement patterns in real time, giving security teams the ability to intervene before a minor incident escalates into a breach.
Data Center Intrusion Detection: Catching Breaches the Moment They Happen
Vibration sensors, door contacts, motion detectors, and perimeter fencing alarms identify unauthorized entry attempts the moment they occur, whether at the property boundary or at the data hall door itself. Integrating these sensors with a centralized alarm platform ensures security personnel receive instant, prioritized alerts rather than sifting through disconnected notifications from separate systems covering different layers of the facility.
Data Center Firewalls: Segmenting the Network from Outside Threats
Network segmentation and next-generation firewalls with deep packet inspection isolate critical workloads from general traffic, limiting lateral movement if a breach occurs elsewhere in the network. This is especially important for multi-tenant colocation facilities, where isolating one client's workload from another's is a baseline expectation rather than an optional feature.
Data Center Encryption: Protecting Data at Rest and in Transit
Strong encryption protects information both at rest and in transit, ensuring that even intercepted or physically removed storage media remains unreadable without authorized keys. Robust key management practices, including hardware security modules and regular key rotation, are essential to keeping encrypted data genuinely protected rather than merely compliant on paper.
Data Center Threat Detection: Spotting Anomalies Before They Escalate
SIEM platforms, behavioural analytics, and threat intelligence feeds identify anomalies before they escalate into full incidents, correlating activity across both IT and operational technology systems. Continuous monitoring allows security teams to spot early indicators — unusual login patterns, abnormal data transfers, or unexpected configuration changes — and respond proactively rather than discovering an issue during a routine audit.
Training and Awareness for Data Center Staff
Even the strongest technical controls can be undermined by a staff member propping open a secured door for convenience, or a contractor sharing a credential with a colleague who has not been formally enrolled in the system. Regular training for anyone with legitimate facility access — covering why tailgating matters, how to report a lost credential immediately, and what to do if they notice an unfamiliar person near the perimeter — closes a gap that no camera or sensor can fully address on its own.
Vehicle and Delivery Access: A Frequently Overlooked Risk Vector
Delivery vehicles, maintenance contractors, and equipment shipments represent a recurring point of access that facilities sometimes secure less rigorously than staff entry points, despite the genuine risk they can carry. A properly designed vehicle checkpoint verifies both the vehicle and its occupants against a pre-approved list before granting access to the loading area, and logs the visit with the same rigor applied to staff badge access, rather than treating deliveries as a lower-priority exception to the facility's normal security posture.
Common Deployment Scenarios: Hyperscale, Colocation, and Enterprise Data Centers in the UAE
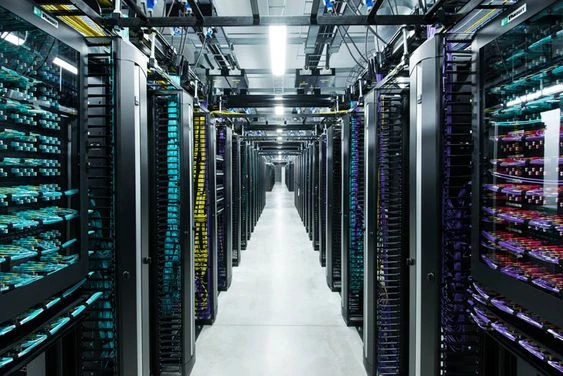
Hyperscale facilities operated by global cloud providers typically specify the most extensive perimeter and physical security investment of the three, given the scale and diversity of workloads hosted on a single campus. Colocation providers need particularly strong tenant isolation, since a single facility hosts multiple independent client organizations that each require confidence their infrastructure is separated from every other tenant's. Enterprise-owned data centers embedded within a corporate campus often need to balance strong data hall security with the more open access expectations of the surrounding office environment.
Perimeter Design: Fencing, Barriers, and Vehicle Access Control
Effective perimeter design combines physical fencing rated to deter forced entry, vehicle barriers capable of stopping a ram-raid attempt, and controlled vehicle checkpoints that verify a delivery or service vehicle before it ever reaches the building. UAE facilities operating within larger free zone campuses should coordinate their own perimeter design with the broader campus security plan, since gaps between individually secured buildings and shared campus infrastructure are a common oversight in multi-tenant technology parks.
Integration Between Physical Security and IT Security Operations
Facilities that maintain separate physical security and IT security teams, each running its own tools and incident response process, often struggle to correlate an event that spans both domains — such as a badge anomaly coinciding with unusual network activity. Converging these functions into a single security operation view, even if the underlying teams remain organizationally distinct, significantly improves an operator's ability to detect and respond to coordinated attacks targeting both the physical and digital layers simultaneously.
Data Privacy and Governance for UAE Data Center Operators
Because data centers often host a mix of financial, government, and multinational corporate workloads, operators need clear policies on data classification, tenant isolation, and internal access rather than treating all hosted data as equally sensitive. UAE operators should confirm that any data-sharing agreements with international clients or partners are properly documented, and that tenant data specifically is protected according to contractual privacy commitments made to each client.
Measuring Return on Investment for Data Center Security Upgrades
The business case for comprehensive data center security usually rests on avoided downtime costs, reduced risk of a tenant or client data breach that could trigger contractual penalties, and a stronger audit trail for compliance reviews. Operators that previously treated perimeter and physical security as separate line items from IT security spending often find that a properly integrated approach avoids the far higher cost of a breach discovered only after client data has already been compromised.
Staffing and Governance: Building a Dedicated Security Team
Technology alone does not secure a facility without clear ownership of who is responsible for badge issuance, camera monitoring, and incident response around the clock. Many UAE operators find that data center security works best as a distinct function with its own escalation procedures, rather than being folded entirely into general building security that also handles unrelated tenant or campus concerns. Establishing clear governance over who can approve new access credentials and how quickly a lost credential is revoked is often what separates a well-run facility from one that looks secure on paper.
Disaster Recovery and Business Continuity Planning
A data center's physical security plan should not be considered separate from its disaster recovery planning, since both ultimately protect the same underlying systems and client data. Operators should maintain documented failover procedures for power loss, cooling failure, or a physical security incident that temporarily restricts access to the facility, along with regular testing of these procedures rather than only reviewing them after an actual incident occurs.
Choosing the Right Vendor: Questions to Ask Before You Commit
Operators evaluating a security provider should ask for specific examples of comparable data center deployments, not just general commercial building references, since the two environments present meaningfully different challenges. Useful questions include how the vendor's proposed system separates perimeter, building, and data hall credentials, what happens during a network outage between the facility and any centralized monitoring platform, and how quickly the platform can issue or revoke access following staffing changes.
Comparing In-House and Managed Security Services
Some UAE operators prefer to manage their data center security entirely with in-house teams, while others opt for a managed service arrangement where a specialist provider handles ongoing monitoring, system maintenance, and incident response on the operator's behalf. In-house management offers tighter direct control and can be more cost-effective for larger operators with existing dedicated security staff, while a managed arrangement often makes more sense for smaller or single-site facilities without a dedicated security operations team.
Total Cost of Ownership Beyond Initial Hardware
Operators comparing providers often focus heavily on the upfront cost of cameras, sensors, and access control hardware, but the total cost of ownership over a multi-year deployment includes software licensing, firmware updates, ongoing technical support, and the labour required for credential and policy management. A cheaper initial hardware quote can end up costing more over several years if the vendor's support response times are slow or if system updates require costly on-site visits.
Aligning Investment with UAE Smart-City Standards
The UAE's continued push toward smart-city standards across Dubai and Abu Dhabi means new data center developments increasingly specify integrated, technology-forward security infrastructure from the earliest design stages rather than retrofitting it after construction. Developers and operators alike benefit from aligning their security specification with these broader smart-city expectations, since doing so both future-proofs the investment and signals a level of operational maturity that increasingly matters to prospective tenants and clients.
Building a Long-Term Data Center Security Roadmap
Rather than attempting to fund every layer of protection in a single budget cycle, many operators find it more realistic to phase a security upgrade across two or three fiscal years, prioritizing the highest-risk gaps first. A common approach starts with perimeter and access control, since these address the most immediate exposure, followed by surveillance and intrusion detection upgrades, and finally more advanced analytics and threat detection capabilities once the foundational layers are in place.
Data Center Security UAE: Local Market Considerations
Strategies for UAE facilities must account for the country's rapid expansion of hyperscale and colocation capacity across free zones and dedicated technology parks, alongside guidance from national information assurance frameworks. Facilities embedded within Dubai and Abu Dhabi technology districts increasingly pair physical redundancy with layered access and surveillance controls to satisfy both operational security goals and external compliance reviews.
Data Center Security Dubai: Business Hub Deployments
Projects in the emirate are concentrated within its major free zones and technology parks, where high tenant density and the concentration of financial and multinational corporate workloads make comprehensive, layered security especially valuable for both operators and their clients.
Why Facility Owners Choose Tektronix LLC
Tektronix LLC has delivered integrated physical and cyber protection projects for hyperscale, colocation, and enterprise data center clients across the UAE and wider GCC, with engineering teams holding certifications spanning perimeter security, access control, video analytics, and network security design. Its project portfolio includes facilities requiring compliance with ISO 27001 and regional information-assurance mandates. Operators evaluating a provider for a new build or retrofit can review the full Tektronix LLC data center perimeter security solutions to see how these capabilities are applied on real deployments across the region.
Best Practices Checklist for UAE Data Center Operators
Data center operators across the UAE should benchmark their current posture against the following priorities:
- Layer perimeter fencing, vehicle barriers, and controlled checkpoints ahead of the building entrance
- Maintain layered credentialing with periodic access-rights review
- Integrate video analytics with centralized alarm and monitoring platforms
- Test incident-response and failover procedures at least twice per year
- Align encryption and key-management practices with ISO/IEC 27001 requirements
- Converge physical and IT security monitoring into a single operational view
- Document all controls for audit readiness under national information-assurance guidance
Conclusion
Data Center Security in the UAE now spans everything from the property fence line to the server rack, with Cybersecurity for Data Center convergence, Data Center Encryption, and Data Center Firewalls protecting the digital layer while Data Center Access Control, Data Center Surveillance, Data Center Intrusion Detection, and Data Center Threat Detection protect the physical one. As Data Center Security UAE and Data Center Security Dubai deployments continue to mature alongside the country's hyperscale and colocation growth, operators who treat perimeter and digital defense as one integrated system will be far better positioned for the compliance reviews and threat landscape ahead.
FAQs
1. Why does perimeter security matter for a data center beyond the building itself?
Facilities located within larger free zone or campus environments benefit from treating the property boundary as the first checkpoint, since fencing, vehicle barriers, and controlled checkpoints deter and delay unauthorized approach well before anyone reaches the building entrance.
2. How does physical security integrate with network security in a modern facility?
Converged security operations correlate badge access events with network activity, allowing teams to detect coordinated attacks that span both the physical and digital layers far earlier than treating the two as separate concerns.
3. What compliance frameworks matter most for UAE data centers?
ISO/IEC 27001, PCI DSS for financial workloads, and UAE Information Assurance guidance are among the most commonly referenced frameworks for facilities handling sensitive or regulated data.
4. Is managed security a better option than an in-house team?
It depends on the operator's scale and existing resources; larger facilities with dedicated staff often prefer in-house management, while smaller or single-site operators frequently benefit from a managed service arrangement.
5. How often should disaster recovery procedures be tested?
Most operators benefit from testing failover and incident-response procedures at least twice a year, rather than only reviewing them after an actual incident has already occurred.
For more information contact us on:
Tektronix Technology Systems Dubai-Head Office
+971 50 814 4086
+971 55 232 2390
Office No.1E1 | Hamarain Center 132 Abu Baker Al Siddique Rd – Deira – Dubai P.O. Box 85955











Sign in to leave a comment.