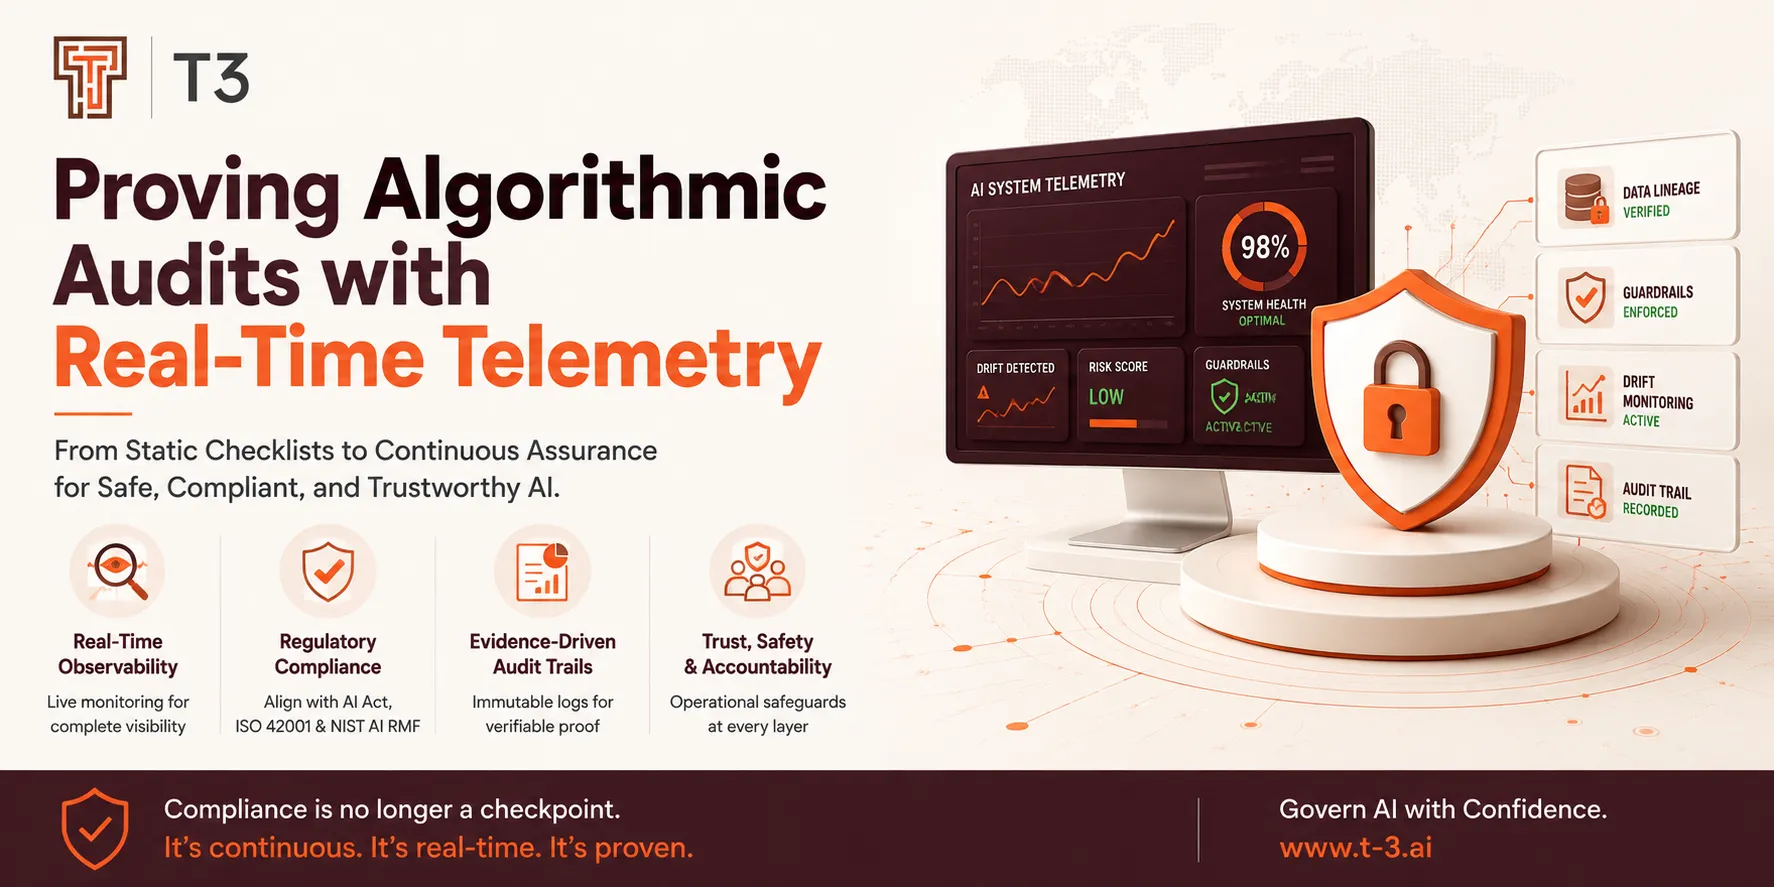

The era of treating Artificial Intelligence as a black box is officially over. As generative models and autonomous agents shift from experimental novelties to core enterprise infrastructure, they exit the lawless frontier and enter one of the most strictly regulated technology landscapes in history. Globally, frameworks like the European Union AI Act, ISO/IEC 42001, and the NIST AI Risk Management Framework are redefining what it means to deploy software safely. For organizations operating in high-stakes environments, such as financial services, enterprise technology, and critical infrastructure, regulatory compliance automated tracking can no longer be an afterthought managed by a static checklist or an annual legal review. It requires direct, active production engineering because true algorithmic safety means proving alignment with law, regulation, and internal policy at every moment of a model's lifecycle. To achieve this, businesses must bridge the gap between abstract policy and active systems engineering by deploying algorithmic auditing software built for continuous production monitoring. Specifically, LLM observability drives continuous data validation during an AI Conformity Assessment. By establishing continuous telemetry, organizations transform static point-in-time documentation into an active, verifiable defensive posture
The Paradigm Shift: From Checklists to Continuous Assurance
Historically, software compliance followed a predictable cadence. A team built a system, an internal or external auditor reviewed the documentation, a risk tier was assigned, and a certificate was signed. This approach worked well for deterministic software. If the code did not change, the outputs remained predictable.
Generative models, large language models, and agentic workflows completely break this traditional paradigm. By their very nature, these systems are non-deterministic. A model that undergoes adversarial red-teaming in a controlled laboratory environment may behave completely differently when exposed to the unpredictable nuances of real-world user inputs. Context windows shift, vector databases receive fresh or potentially toxic data, and semantic drift slowly degrades the guardrails originally engineered to protect the system.
Relying on a static, manual registration process leaves a company blind to "shadow AI", which includes untracked models or fine-tuned variants operating without formal oversight. True assurance demands that organizations maintain an audit-ready register that dynamically discovers, catalogues, and risk-tiers every active asset across the enterprise. Compliance cannot be a snapshot taken before launch; it must be an ongoing, living state of execution.
+-----------------------------------------------------------------+
| TRADITIONAL AUDITING |
| [Lab Training] ---> [Static Legal Review] ---> [Blind Launch] |
+-----------------------------------------------------------------+
VS.
+-----------------------------------------------------------------+
| CONTINUOUS ASSURANCE |
| [Live Model] ---> [Real-Time Telemetry] ---> [Dynamic Audit] |
+-----------------------------------------------------------------+
Mapping Real-Time Telemetry to Regulatory Requirements
When regulatory bodies demand an evaluation of a high-risk system, they look for verifiable evidence across multiple structural layers. They want to ensure that risks are caught before they impact end-users or violate systemic compliance boundaries.
By leveraging advanced monitoring stacks, engineering teams can turn complex runtime metrics into structural evidence that satisfies rigorous legal audits. This bridge between live telemetry and regulatory requirements spans four foundational pillars:
1. Data Foundation and Lineage Verification
An evaluation must guarantee that the data feeding a model is both traceable and trustworthy. In production, this requires tracking data source lineage, validation workflows, and real-time bias screening. Live telemetry monitors the inputs flowing into Retrieval-Augmented Generation (RAG) systems, verifying data freshness and screening out corrupted or non-compliant vectors before they compromise the prompt window.
2. Guardrails and Live Moderation Logs
Maintaining data security and access controls requires real-time enforcement. Telemetry frameworks capture every prompt-response pair, ensuring that role-based access limits remain fully functional. By logging the inputs and outputs of inline guardrails, organizations generate an immutable record proving that toxic, biased, or restricted data was successfully intercepted and anonymized before causing harm.
3. Model Performance and Drift Detection
A model must remain fair, fit, and monitored across its entire operational lifespan. Runtime monitoring tracks token usage, latency, and semantic distance metrics to identify when a model begins to drift from its baseline evaluation benchmarks. When confidence scores drop or output distributions shift unexpectedly, telemetry triggers automated alerts, showing exactly where a system is beginning to degrade.
4. Human Oversight and Escalation Tracking
Regulators strictly require clear accountability mapping, establishing clear boundaries for human override authority wherever decisions carry serious weight. Live logging tracks exactly when an autonomous system hands off a decision to a human operator, records the validation or override action taken, and logs the final outcome. This ensures that the chain of responsibility is never ambiguous during an official investigation.
Moving Beyond Standard Infrastructure Monitoring
A common mistake made by enterprise organizations is treating artificial intelligence components like standard web microservices. Traditional infrastructure monitoring looks at metrics like CPU utilization, memory allocations, server uptime, and generic HTTP 500 error rates. While these metrics are vital for maintaining system health, they are completely blind to algorithmic failures.
An LLM application can operate with a flawless 99.99% server uptime, return rapid 200 OK responses, and consume minimal memory, while simultaneously outputting legally hazardous hallucinations, leaking protected personal data, or violating regional fairness guidelines.
+----------------------------------------+------------------------------------------+
| WHAT TRADITIONAL MONITORING SEES | WHAT ALGORITHMIC TELEMETRY SEES |
+----------------------------------------+------------------------------------------+
| * Server Uptime (e.g., 99.9%) | * Semantic Evaluation Drift Scores |
| * HTTP Error Rates (e.g., 200 OK) | * Toxic or Biased Content Flags |
| * Memory / CPU Consumption | * Context Window Lineage & Grounding |
| * Network Latency | * PII Leakage & Prompt Injections |
+----------------------------------------+------------------------------------------+
To bridge this visibility gap, companies must transition from basic infrastructure monitoring to specialized semantic tracking. This means measuring the properties of the unstructured text itself. By establishing production traces that evaluate semantic relevance, grounding scores, and toxic content markers on the fly, teams can spot system anomalies that traditional software dashboards miss entirely.
When these semantic evaluation thresholds are crossed, the system can automatically flag the incident, log the full context window, and alert compliance teams before a minor model drift turns into a severe regulatory breach.
Architectural Blueprint for an Audit-Ready Stack
Building an infrastructure capable of converting live runtime metrics into audit-ready legal evidence requires a thoughtful, multi-layered approach. The objective is to decouple the production runtime from the compliance and analysis engine, ensuring zero performance overhead while capturing an immutable, end-to-end audit trail.
[ User Interaction ]
│
▼
┌────────────────────────────────────────────────────────┐
│ 01. INGESTION & DISCOVERY LAYER │
│ • Dynamic Agent Discovery │
│ • Shadow Tool Identification │
└───────────────────────┬────────────────────────────────┘
│
▼
┌────────────────────────────────────────────────────────┐
│ 02. INLINE GUARDRAIL & ACCESS LAYER │
│ • PII Masking & Token Anonymisation │
│ • Input / Output Moderation Filters │
└───────────────────────┬────────────────────────────────┘
│
▼
┌────────────────────────────────────────────────────────┐
│ 03. SEMANTIC TELEMETRY & RUNTIME LAYER │
│ • OpenTelemetry Semantic Conventions │
│ • Multi-step Agent Dependency Tracing │
└───────────────────────┬────────────────────────────────┘
│
▼
┌────────────────────────────────────────────────────────┐
│ 04. ASSURANCE & AUDIT ENGINE │
│ • Automated Compliance Mapping │
│ • Immutable Legal Audit Logs │
└────────────────────────────────────────────────────────┘
Layer 1: Ingestion & Discovery
Every interaction begins with discovery. The stack must automatically inventory every inbound request, mapping it to a registered model or flagging it as an unauthorized tool. This ensures that no hidden workflows bypass the security perimeter.
Layer 2: Inline Guardrails
Before data reaches the core model, it passes through an inline security layer. Here, sensitive user data is scrubbed or anonymized, and prompts are inspected for adversarial injection attacks. This layer acts as the initial firewall, preventing compliance failures before they occur.
Layer 3: Semantic Telemetry
As the request executes, standard open-source tracing protocols collect semantic details of the multi-step agent actions. Rather than just recording that a function ran, this layer captures what the function retrieved, how it reasoned, and what payload it passed along.
Layer 4: The Compliance Engine
Finally, this runtime telemetry stream is fed directly into an immutable database. Here, the raw system logs are mapped directly against specific regulatory articles, such as EU AI Act requirements or ISO standards, turning engineering logs into structured, audit-ready compliance evidence.
Conclusion: Engineering Trust as a Competitive Advantage
The companies that thrive in this highly regulated future will be those that treat safety as an engineering discipline rather than a legal burden. By moving past static point-in-time reviews and embedding automated tracking directly into the runtime fabric, organizations protect themselves from liabilities while accelerating their production deployments.
When your technical data streams are directly aligned with regulatory expectations, an upcoming audit ceases to be an existential risk. Instead, it becomes a structured, repeatable validation of your operational excellence. True alignment means having the infrastructure in place to identify exactly where your models would fail, long before they ever do.
How to Turn Policy into Production Reality
Are you ready to transform your risk-management strategy from manual checklists into automated engineering controls? If you are looking to secure your deployment pipeline, let us know how we can assist:
- Do you want to build a production-ready telemetry architecture blueprint for your engineering team?
- Do you need to map your existing runtime monitoring metrics directly to the strict legal demands of the EU AI Act or ISO/IEC 42001?
- Are you looking to run adversarial red-teaming to test your model's real-world guardrails under stress?
Let us know your core focus area, and we can tailor the next steps directly to your operational needs!










Sign in to leave a comment.