
The day ransomware stops being an IT problem
Most companies discover their ransomware strategy the same way people discover they should have backed up their phone—after the screen goes dark and starts making demands. One minute payroll is running, warehouse scanners are syncing, customer support is opening tickets; the next, every shared drive has a new file extension and a note that reads like a badly translated hostage script. The joke, if there is one, is that ransomware rarely arrives with cinematic flair. It comes through ordinary things: a phishing email, an exposed remote desktop service, a stolen VPN credential, an unpatched edge device. Very IKEA-manual energy—small missing screws, then the whole shelf collapses.
That is why serious ransomware protection is not a single product purchase. It is an operating model. Businesses that resist extortion well tend to do a few unfashionable things consistently: they know what assets matter, they reduce identity risk, they patch internet-facing systems quickly, they segment networks, they maintain recoverable backups, and they rehearse decisions before panic turns the boardroom into a group chat with legal consequences.
Recent reporting and industry guidance have sharpened that point. TechTimes’ 2026 overview of major cyber threats emphasizes layered controls rather than silver bullets, while BizTech’s prevention guide for SMBs focuses on fundamentals that remain painfully relevant because attackers keep succeeding against fundamentals. That should be mildly embarrassing for the industry—and very clarifying for buyers.
For businesses, the strategic question is no longer whether ransomware is possible. It is whether the company can keep operating if a threat actor reaches one part of the environment. Resilience, not wishful thinking, is the benchmark. The best defense plan is the one that assumes somebody eventually gets in. Very sitcom apartment door with a broken lock—less glamorous, more realistic.
Ransomware protection is a business continuity discipline disguised as cybersecurity. The technical controls matter, but the outcome that counts is whether the company can contain damage and recover operations without funding criminals.
How ransomware became a business model
Ransomware used to be discussed as a malware category. That framing is now too small. Modern ransomware is an ecosystem with brokers, affiliates, leak sites, negotiators, initial access sellers, and data extortion specialists. The malware is only one component; the business model is the real threat. Attackers may encrypt systems, steal data first, threaten public leaks, harass customers or employees, and pressure executives through regulatory exposure. Encryption was the pilot episode. Multi-extortion became the spin-off that somehow got darker.
The shift accelerated in the early 2020s as ransomware-as-a-service lowered the barrier to entry. A criminal group could develop tooling once and let affiliates run campaigns at scale. That made operations more distributed and more resilient from the attacker’s perspective. Takedowns still matter, but the ecosystem regenerates quickly because access, malware, and monetization are modular. If one crew disappears, another often reuses similar tactics within weeks or months, according to repeated reporting from Reuters and major incident-response firms.
Businesses also gave attackers exactly what they wanted: sprawling cloud estates, hybrid work, over-privileged identities, and too many unmanaged devices. Add third-party software dependencies and internet-exposed appliances, and the attack surface starts to look like a software bug report nobody triaged. The result is that ransomware is no longer just a “data center” risk. It can hit SaaS administration, virtualized workloads, backup systems, manufacturing lines, retail operations, and sector-specific operational technology.
That is especially visible in industries where uptime is non-negotiable. pv magazine International’s piece on ransomware in the solar sector underscores how cyber incidents can affect operational continuity, not merely office productivity. Once physical operations are tied to digital control and monitoring, recovery planning has to include both IT and OT realities.
For smaller firms, the misconception that attackers only chase giant enterprises remains dangerous. The Tech Edvocate’s 2026 article on unseen ransomware threats for small businesses makes the obvious but still underappreciated point: smaller organizations are often easier to breach and less able to absorb downtime. Criminals like prestige targets, sure—but they also like easy money. Same reason scammers text everyone, not just billionaires.
Understanding that evolution matters because it changes defensive priorities. If ransomware is an industrialized extortion pipeline, then protection must cover access prevention, privilege control, detection, containment, offline recovery, legal response, and communications. Buying endpoint software without changing operational habits is like putting a deadbolt on a tent.
The controls that actually change outcomes
When security teams discuss ransomware, the conversation can drift toward tooling catalogs—EDR, XDR, MDR, SIEM, SOAR, and a few acronyms that sound like rejected Star Wars droids. Tools help, but outcome-changing controls are more basic and more measurable. They reduce the chance of initial compromise, slow lateral movement, and preserve clean recovery paths. Businesses looking for a practical baseline should prioritize a stack of controls that map directly to common ransomware kill chains.
- Identity hardening: enforce phishing-resistant multifactor authentication where possible, remove dormant accounts, restrict local admin rights, and review privileged access continuously.
- Exposure reduction: patch internet-facing systems quickly, disable unnecessary remote access, and place remote administration behind stronger controls.
- Endpoint and server visibility: deploy modern endpoint protection with behavioral detection and tamper resistance across workstations and servers.
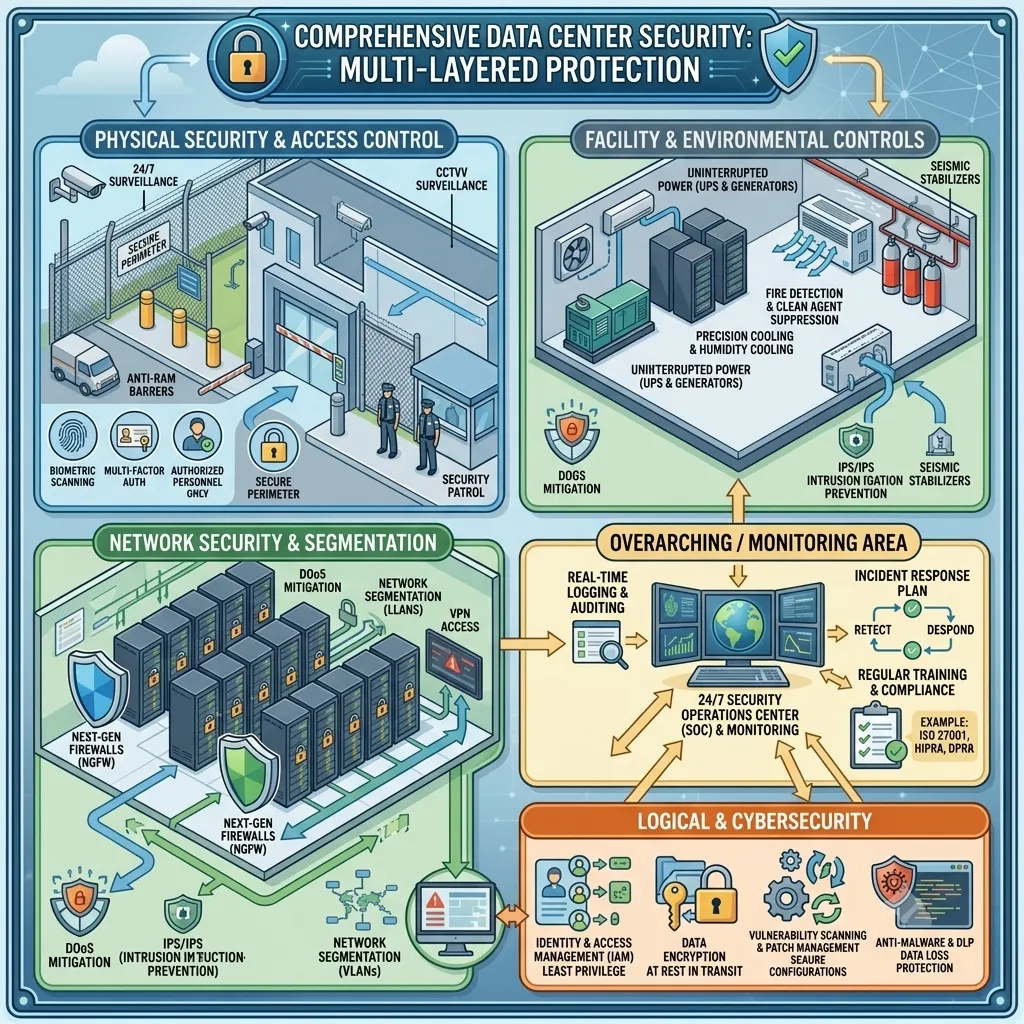
- Network segmentation: separate critical servers, backup infrastructure, identity systems, and operational technology to limit blast radius.
- Backup resilience: maintain offline or immutable backups, test restoration regularly, and secure backup consoles with separate credentials.
- Email and web defenses: filter malicious attachments, block known bad domains, and isolate risky browsing where feasible.
- Logging and monitoring: retain enough identity, endpoint, and network telemetry to detect privilege escalation and mass encryption behavior.
Among these, identity deserves special emphasis. Many large incidents begin with stolen credentials rather than exotic malware. Once attackers obtain administrative access, they can disable security tools, push malicious payloads through legitimate management systems, and target backups. According to multiple vendor incident reports over recent years, abuse of remote management tools and living-off-the-land techniques remains common because they blend into normal operations. That means the old perimeter-centric mindset is not merely dated; it is structurally inadequate.
Patch discipline is similarly unglamorous and similarly decisive. Internet-facing firewalls, VPNs, file transfer appliances, hypervisors, and collaboration tools have all featured in major exploitation waves. Businesses should maintain an asset inventory that identifies which systems are externally reachable and who owns patching decisions for each one. If nobody owns the box, the box eventually owns your weekend.
For organizations building maturity, internal educational resources can help frame the journey. WriteUpCafe’s Beginners Guide to Ransomware Protection Strategies for Businesses is useful for foundational planning, while Advanced Ransomware Protection Strategies for Businesses goes further into layered defenses and response thinking.
The best anti-ransomware control is often the boring one that was maintained properly for 18 months. Attackers routinely exploit inconsistency more than complexity.
None of this eliminates risk. It changes economics. Attackers prefer environments where privilege is easy, monitoring is thin, and backups are reachable. Make those conditions harder to find, and many campaigns fail earlier or recover less profitably for the criminal side. Security does not need to be perfect. It needs to be expensive to defeat.
Backups, recovery, and the myth of “we can just restore”
Ask a company whether it is prepared for ransomware and you will often hear a confident line about backups. Ask whether those backups are isolated, tested at scale, protected from admin compromise, and mapped to recovery time objectives for critical processes, and the room gets quieter. A backup strategy that exists only in policy documents is basically fan fiction.
Effective ransomware resilience depends on recoverability, not mere data retention. That means businesses must know which systems need to return first, in what order, with which dependencies. Restoring a database before identity services, DNS, or application secrets may not deliver actual business function. Likewise, restoring encrypted data from a backup that was silently corrupted or never tested under pressure can waste precious hours during an incident.
A practical recovery model usually includes three layers: frequent operational backups for routine issues, isolated backups for destructive scenarios, and documented rebuild procedures for core platforms such as identity, virtualization, and endpoint management. The isolated layer matters most in ransomware events because attackers increasingly target backup repositories and management consoles. Immutable storage, air-gapped copies, or logically separate environments can prevent the “restore” plan from being encrypted alongside production.
- Define tier-0 systems: identity, backup management, core networking, virtualization hosts, and security tooling.
- Map application dependencies so restoration follows business logic rather than guesswork.
- Test backup restoration quarterly for representative critical systems, not just one token file server.
- Run a full ransomware recovery exercise annually with IT, security, legal, communications, and executive leadership.
- Measure realistic recovery time and recovery point outcomes, then update board-level risk assumptions.
Businesses should also separate retention from resilience. Long retention helps with legal and compliance needs; resilience requires clean, recoverable snapshots beyond attacker reach. Those are different design goals. According to incident responders cited by Reuters over the past several years, organizations that recover fastest are not necessarily the ones with the most tools. They are the ones that know exactly what “minimum viable operations” looks like and have rehearsed restoring it.
There is also a governance issue here. Executives sometimes assume cyber insurance or negotiators will smooth the path if things go wrong. Insurance may help with costs, subject to policy terms and controls, but it does not rebuild your Active Directory at 3 a.m. on a holiday weekend. Recovery remains an operational capability. No insurer is assembling your flat-pack wardrobe for you.
The human layer: phishing, privilege, and third-party risk
Ransomware prevention discussions often default to user awareness posters—hover over links, report suspicious emails, do not click strange attachments. Fine, as far as it goes. But employee behavior is only one piece of the human problem. Administrative behavior, contractor access, help desk workflows, and vendor trust relationships are often more consequential than whether Karen from accounts payable clicked a fake invoice. Poor Karen gets blamed for a lot.
Phishing still matters because credential theft remains a common path to access. Security awareness training should therefore be tied to technical controls: multifactor authentication, conditional access, browser isolation for risky content, and rapid credential revocation. If training is not reinforced by system design, it becomes corporate theater with slides.
Privilege management is more important. Many ransomware operators move laterally by harvesting cached credentials, abusing service accounts, or escalating through weak admin practices. Businesses should minimize standing privileges, use separate accounts for administration, rotate secrets, and monitor for unusual privilege assignments. Help desk procedures deserve special scrutiny because attackers increasingly exploit password reset and device enrollment processes through social engineering.
Third-party access creates another weak seam. Managed service providers, software vendors, and contractors may have remote access into production environments. If those pathways are not segmented and monitored, a partner compromise can become your incident. This is one reason sector guidance increasingly emphasizes supply-chain hygiene and vendor due diligence. A contract clause does not stop ransomware; it just gives legal something to read while operations are on fire.
Useful questions for vendor reviews include:
- What remote access methods do they use, and are those methods restricted by time, role, and network location?
- Do they enforce multifactor authentication and maintain separate administrative accounts?
- How quickly do they disclose security incidents that may affect customer environments?
- Can their access be monitored, logged, and disabled rapidly by your team?
- Do they require broad persistent privileges, or can access be scoped to specific systems and maintenance windows?
For small and midsize businesses, this is where managed detection and response providers can add real value—if the relationship is structured well. The goal is not to outsource accountability. It is to shorten detection time and improve containment when internal teams are thin. WriteUpCafe’s Ransomware Protection Strategies for Businesses That Work pairs nicely with this point because it focuses on practical measures rather than vendor mythology.
What changed recently in 2026
By 2026, the ransomware conversation has become less naive in three visible ways. First, organizations are paying more attention to identity and cloud administration planes, not just endpoints. Attackers have learned that compromising a cloud tenant, backup admin portal, or remote management platform can be more efficient than detonating malware on one laptop at a time. Defensive planning is finally catching up—slowly, like software release notes after a production outage.
Second, sector-specific exposure is receiving more scrutiny. Energy, manufacturing, healthcare, education, and logistics each have distinct operational dependencies, and guidance now reflects that. The solar and broader energy context discussed by pv magazine International is a good example: digital disruption can affect field operations, maintenance visibility, and revenue continuity, not just office files. That broadens the stakeholder map well beyond the CISO.
Third, 2026 commentary has become more explicit about the limits of prevention-only thinking. Forbes’ piece on endpoint defense and battlefield-style tactics argues for layered, adaptive preparation—an idea echoed across modern incident-response practice. Meanwhile, TechTimes and The Tech Edvocate both stress that small and midsize organizations remain deeply exposed because attackers continue to exploit neglected basics. The industry has not solved ransomware; it has merely become better at admitting which controls matter.
There is also a stronger regulatory and governance undertone. Boards increasingly want evidence of resilience, not just policy statements. Questions now center on restoration testing, critical asset inventories, incident communications, and third-party dependencies. That is healthy pressure. Security teams should answer with metrics that mean something operationally: percentage of critical systems covered by immutable backups, mean time to isolate compromised endpoints, percentage of privileged accounts under stronger authentication, and patch latency for internet-facing assets.
If you want a broader internal reading path, Effective Ransomware Protection Strategies for Businesses in 2026 and Advanced Strategies for Ransomware Protection in Businesses 2026 both fit naturally into a more mature planning cycle. The point is not to collect articles like Pokémon cards. It is to turn guidance into operating discipline.
How to build a ransomware program that survives contact with reality
A credible ransomware strategy should be built like a continuity program with security controls attached. Start by identifying the business processes that cannot fail for more than a defined period—billing, order fulfillment, clinical operations, manufacturing control, customer support, payroll, core communications. Then map the systems, identities, vendors, and data stores those processes rely on. Many organizations skip this and go straight to shopping. That is how you end up with expensive dashboards and no recovery sequence.
From there, define a minimum viable operating state for the first 24, 72, and 168 hours after a destructive cyber event. Which services must be restored first? Which manual workarounds exist? Which customers, regulators, insurers, and partners need notification? Which executives can authorize network isolation or shutdown decisions? These are not side questions. During a real incident, they become the plot.
A strong business program usually includes the following components:
- Governance: named owners for prevention, detection, backup integrity, crisis communications, legal coordination, and vendor management.
- Technical baseline: MFA, segmentation, endpoint protection, patching, secure admin practices, and monitored logging.
- Recovery architecture: immutable or offline backups, rebuild documentation, golden images, and dependency-aware restoration plans.
- Exercises: tabletop sessions for executives and hands-on restoration drills for technical teams.
- Metrics: patch latency, privileged account coverage, restoration success rates, and time to contain test scenarios.
One underused tactic is pre-authorizing disruptive response actions. Security teams often know they should disable remote access, block east-west traffic, or isolate a business unit, but hesitate because approvals are unclear. That delay can turn one compromised enclave into a company-wide outage. A written decision framework—approved before an incident—removes some of the chaos.
Another is communications hygiene. Employees, customers, and partners need timely, accurate updates during ransomware events. Misinformation spreads fast, and attackers sometimes exploit public confusion. Drafting templates in advance for internal notifications, customer advisories, and media holding statements saves time when every minute matters. Boring preparation, heroic payoff.
The final test is cultural. If leaders reward uptime at any cost, defer patching because “operations are busy,” and treat backup testing like an optional dental cleaning, ransomware risk will remain structurally high. If leaders accept short-term inconvenience to preserve long-term resilience, the odds improve substantially. Not magic—just management.
What smart businesses should do next
For companies reassessing ransomware exposure now, the next steps are less mysterious than vendors imply. Begin with the attack paths most likely to hurt you: exposed remote services, weak identity controls, over-privileged admins, untested backups, and flat networks. Then validate whether your assumptions survive a realistic scenario. Could an attacker with one compromised employee account reach sensitive file shares? Could a domain admin compromise disable endpoint tools? Could your backup team restore a critical ERP system into a clean environment within the promised timeframe? If the answer is “probably,” that is not a strategy. That is a prayer with licensing fees.
Businesses should also calibrate expectations around payment. Law enforcement agencies and many security professionals discourage paying ransoms because payment fuels criminal activity and does not guarantee full recovery or data deletion. Some organizations still pay under extreme pressure, but that outcome should be treated as a failure state, not a fallback plan. The goal of preparation is to preserve options so the company is not negotiating from a position of collapse.
What deserves attention over the next year is not just malware sophistication but attacker adaptability. As defenses improve on endpoints, criminals will continue targeting identity systems, cloud control planes, third-party pathways, and backup infrastructure. The response should be equally adaptive: stronger identity assurance, better telemetry, tighter segmentation, and routine restoration drills that include business leadership, not just engineers muttering at dashboards.
The companies that handle ransomware best are rarely the loudest about cybersecurity. They are the ones that did the quiet work—asset inventory, patch discipline, backup isolation, privilege control, rehearsed communications, tested recovery. No fireworks, no cyber-drama trailer voice-over. Just operational competence under pressure.
That is the uncomfortable lesson and, frankly, the useful one. Ransomware protection strategies for businesses succeed when they are treated as a repeatable management system rather than a panic purchase. Build for containment. Build for recovery. Build for the day somebody clicks the wrong thing and the network decides to audition for a disaster movie. Then make sure your ending is boring.












Sign in to leave a comment.