
Data Center Security has become the single most important investment for organizations that operate critical infrastructure inside the Kingdom of Saudi Arabia. As Vision 2030 accelerates the nation's digital transformation, colocation campuses, hyperscale facilities, and private enterprise data centers across Riyadh, Jeddah, and Dammam are processing more sensitive workloads than at any point in the Kingdom's history. A single physical or cyber breach can compromise thousands of tenants, trigger regulatory penalties, and permanently damage client trust. This guide walks through the layered strategies, technologies, and regional realities that define resilient protection, and explains how enterprises can work with a trusted data center security solutions provider to safeguard their most valuable digital assets.
Why Critical Infrastructure Protection Is a National Priority
Saudi Arabia's digital economy is expanding at a pace few regions in the world can match. Under Saudi Vision 2030, the Kingdom has positioned itself as a regional hub for cloud computing, artificial intelligence, and hyperscale investment, with global technology providers building new facilities across the country. This growth has made data centers a form of national critical infrastructure, on par with power grids, water systems, and telecommunications networks. Regulatory bodies, including the National Cybersecurity Authority, have responded with stricter physical and digital security mandates for any facility handling regulated data. For operators, this means protection can no longer be an afterthought bolted onto an existing building; it must be engineered into the facility from perimeter fencing to the individual server cabinet.
This shift is also reshaping procurement. Enterprise tenants evaluating a colocation provider now ask for physical security documentation as routinely as they ask about power redundancy or network uptime. Boards and audit committees increasingly treat physical breach risk as a board-level concern rather than a facilities-management line item, particularly for sectors such as banking, healthcare, and government services where downtime or data exposure carries direct regulatory consequence. As a result, security architecture has moved from the end of the design process to the very beginning of it, influencing site selection, building layout, and even the placement of loading docks and generator yards.
Understanding the Modern Threat Landscape Facing Data Centers
The threats facing modern facilities fall into two closely connected categories: physical intrusion and cyber intrusion. Perimeter breaches, tailgating, and unauthorized cabinet access remain common, but insider risk is now the dominant concern for security teams. Independent industry research consistently finds that a majority of physical security incidents involve individuals who already hold some level of authorized access, whether through credential sharing, ghost accounts, or privilege creep. At the same time, attackers increasingly target the network layer, attempting to move laterally from a compromised workstation into the systems that control badge readers, environmental sensors, and cooling infrastructure. Because physical and digital systems are now deeply interconnected, a weakness in one domain quickly becomes a weakness in the other.
Colocation and multi-tenant facilities carry an additional dimension of risk: a contractor or vendor with legitimate access to one tenant's cage should never be able to reach another tenant's equipment, network segment, or audit trail. Third-party maintenance staff, cleaning crews, and equipment vendors are frequently the weakest link in an otherwise strong perimeter, simply because their access is granted infrequently and reviewed even less often. A resilient security program treats vendor and contractor access with the same rigor as full-time staff access, including scheduled expiry, escort requirements in sensitive zones, and full audit logging of every credential issued.
Data Center Access Control: The First Line of Defense
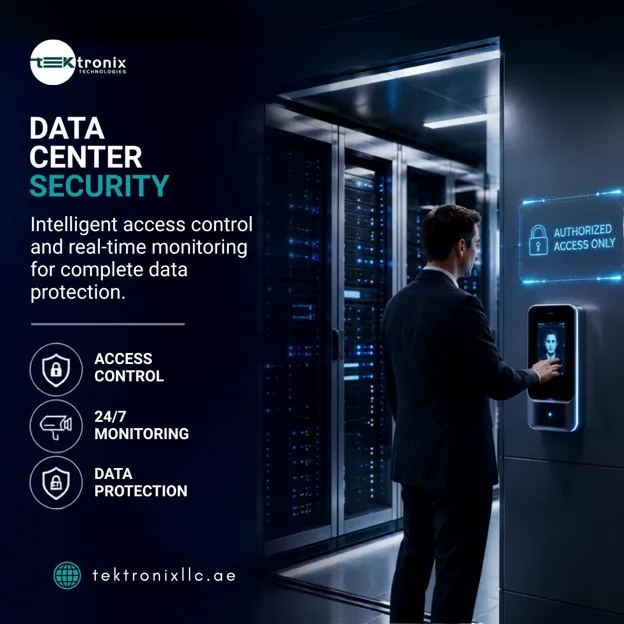
Data Center Access Control is the foundation on which every other security layer is built. A mature deployment does not rely on a single credential type at a single door; it enforces multi-factor verification at the site perimeter, the building entrance, the server room, and the individual cabinet or cage. Biometric readers combined with card credentials, mantrap interlocks that permit only one verified person through at a time, and role-based, time-restricted permissions all work together to close the gaps that a simple keycard system leaves open. Colocation operators face an additional requirement: each tenant must be isolated from every other tenant, with independent audit trails and credential policies enforced down to cage level. Organizations evaluating a layered data center access control framework should look for a provider capable of unifying perimeter, building, server room, and cabinet-level control under a single auditable system.
Data Center Surveillance and Real-Time Situational Awareness
Cameras alone are no longer sufficient. Modern Data Center Surveillance combines high-definition CCTV coverage with AI-driven video analytics capable of detecting multi-person entry in single-person zones, loitering near restricted cabinets, or unauthorized objects left in sensitive areas. Automatic number plate recognition at vehicle entry points, integration with guard booth workflows, and centralized monitoring dashboards give security operations centers a single, real-time view across every zone of the facility. When surveillance data is synchronized with access control logs, security teams can correlate a badge event with the corresponding video footage in seconds rather than hours, dramatically reducing incident response time.
Data Center Intrusion Detection: Layered Physical Defense
Data Center Intrusion Detection extends protection beyond monitored entry points to cover the areas between them. Vibration sensors on perimeter fencing, occupancy sensors inside mantraps, door-forced-open alarms, and motion detection in raised floor voids all feed into a centralized alarm management platform. When a sensor is triggered outside expected parameters, whether that is a door held open too long or unexpected movement in a restricted zone, the system automatically escalates the event to on-site guards and remote monitoring staff simultaneously. This layered approach ensures that even if one control is bypassed, a secondary detection mechanism captures the anomaly before it develops into a full breach.
Data Center Threat Detection: From Reactive to Predictive Security
Traditional alarm systems tell a security team what has already happened. Modern Data Center Threat Detection platforms are designed to identify what is about to happen. By applying behavioural analytics to access patterns, environmental telemetry, and network traffic simultaneously, these systems can flag anomalies, such as a technician badging into a cabinet outside their normal working hours, or an unusual spike in access attempts, before they escalate into an incident. Predictive threat detection shifts security operations from a reactive, alarm-driven model to a proactive one that identifies risk indicators early enough for teams to intervene.
Data Center Firewalls and Network-Level Protection
Physical barriers protect the building; Data Center Firewalls protect the network that runs inside it. Enterprise-grade firewall architecture segments the facility's network into isolated zones, separating building management systems, access control infrastructure, and tenant workloads so that a breach in one segment cannot move freely into another. Next-generation firewalls add deep packet inspection, intrusion prevention, and application-aware filtering, giving operators visibility into traffic patterns that legacy perimeter firewalls simply cannot see. For colocation environments in particular, strict network segmentation between tenants is not optional; it is the technical foundation of the zero-trust model that regulators and enterprise customers now expect.
Data Center Encryption: Safeguarding Data at Rest and in Transit
Even the strongest physical perimeter cannot protect data once storage media leaves the building or traffic moves across a shared network. Data Center Encryption addresses this gap by protecting information both while it is stored on disk and while it moves between systems. Strong encryption standards, combined with rigorous key management practices and hardware security modules, ensure that data remains unreadable to anyone who bypasses physical or network controls. For facilities handling financial, healthcare, or government workloads, encryption is frequently a mandatory requirement under both international standards and Saudi regulatory frameworks, not an optional enhancement.
Cybersecurity for Data Center Operations: Where Physical and Digital Security Converge
Cybersecurity for Data Center environments can no longer be treated as a separate discipline from physical security. Badge readers, cameras, and environmental sensors are themselves networked devices, and a compromised IoT sensor can become an entry point into the broader IT environment just as easily as a stolen credential can. Leading operators now run converged security operations centers where physical alarms, network intrusion alerts, and identity management events are correlated on a single platform. This convergence allows a single anomaly, such as an access badge being used at a door while the same user's network credentials are simultaneously active from a remote location, to be caught immediately rather than investigated after the fact.
Compliance and Regulatory Framework for Data Centers in Saudi Arabia
Operators in the Kingdom must navigate a growing list of compliance obligations. International frameworks such as ISO 27001 Annex A.11, SOC 2 Type II, and PCI DSS 9.x set global benchmarks for physical access control, while the National Cybersecurity Authority's ECC-1:2018 controls and the Communications, Space & Technology Commission's data center licensing conditions establish Kingdom-specific requirements. Auditors increasingly expect documented, timestamped access logs rather than manual sign-in sheets, along with clear evidence of tenant isolation for colocation facilities. Meeting these requirements demands a security architecture designed for compliance reporting from day one, with pre-built templates that map directly to each framework's control language.
Uptime Institute Tier certification adds a further layer of expectation, since Tier III and Tier IV facilities are assessed not only on power and cooling redundancy but on the operational discipline surrounding access to critical infrastructure. During an audit, the ability to produce a complete, tamper-evident access history for any cabinet, on demand and covering any date range, is often the difference between a smooth certification renewal and a lengthy remediation cycle. Facilities that treat compliance reporting as a built-in system feature, rather than a manual exercise performed before each audit, consistently spend less time and cost preparing for regulatory review.
Data Center Security KSA: Regional Considerations Across the Kingdom
Data Center Security KSA requirements vary meaningfully from one region to another. Riyadh's rapidly expanding hyperscale and enterprise campuses demand solutions built for large-scale, multi-tenant environments, while Jeddah's Western Region facilities often need to account for coastal climate conditions alongside standard physical controls. Dammam and Al Khobar, at the heart of the Eastern Province's industrial and energy sector, frequently host facilities with heightened compliance obligations tied to critical national infrastructure. Emerging hubs such as NEOM and Madinah are being built with security requirements engineered in from the ground up rather than retrofitted later. A provider with certified engineers’ resident across these regions, rather than a single national office, is better positioned to deliver same-day response and region-specific compliance expertise. Organizations researching enterprise data center security services in Saudi Arabia should confirm local presence before selecting a long-term security partner.
Data Center Security Riyadh: Protecting the Kingdom's Enterprise Hub
As the capital and the epicenter of the Kingdom's hyperscale investment boom, Data Center Security Riyadh deployments face some of the highest stakes in the country. The city hosts a concentrated mix of government, financial, and multinational enterprise workloads, making it a priority target for both physical and cyber threats. Facilities here typically require the full four-layer security model, from perimeter vehicle barriers along major access roads to cabinet-level electronic locks inside the data hall, supported by a security operations center capable of same-day, on-site response anywhere in the city.
Why Partner with an Experienced Data Center Security Provider
Selecting the right partner is as important as selecting the right technology. Look for evidence of hands-on experience: certified engineers who are resident in the Kingdom rather than flown in for each project, a track record across multiple facility types, and integration expertise with major DCIM platforms such as Nlyte, Sunbird, Schneider EcoStruxure, and Vertiv. Tektronix Technologies has deployed physical security across more than 500 enterprise environments in Saudi Arabia, with certified engineers’ resident in Riyadh, Jeddah, and Dammam and a four-layer security framework aligned to NCA ECC-1:2018, ISO 27001, SOC 2, and PCI DSS. This combination of documented experience, regional presence, and compliance-ready reporting is what separates a genuine security partner from a hardware reseller. Enterprises evaluating providers can review Tektronix's data center security solutions to see how a defense-in-depth architecture is applied across real Saudi facilities.
Best Practices Checklist for Data Center Security
Organizations strengthening their security posture should prioritize the measures below as an integrated system rather than a list of isolated purchases:
- Enforce multi-factor, role-based access control at every layer rather than relying on a single credential type.
- Deploy mantrap interlocks with occupancy sensors at all server room entries to eliminate tailgating.
- Integrate video surveillance with access logs for rapid incident correlation and forensic review.
- Maintain encrypted backups with regularly tested recovery procedures.
- Segment networks so that building management and IT systems cannot be reached from a single compromised point.
- Schedule regular third-party audits against ISO 27001, SOC 2, and NCA ECC-1:2018 controls rather than relying solely on internal reviews.
Conclusion
Protecting critical infrastructure in the Kingdom now depends on a defense-in-depth approach to Data Center Security that spans the perimeter fence to the individual server cabinet. Strong Data Center Access Control, continuous Data Center Surveillance, and reliable Data Center Intrusion Detection work together to stop physical breaches before they escalate. On the digital side, Data Center Firewalls, Data Center Encryption, and integrated Cybersecurity for Data Center operations close the gaps that physical controls cannot reach alone. Predictive Data Center Threat Detection turns security from a reactive discipline into a proactive one, catching risk indicators before they become incidents. Whether you operate in the capital or elsewhere in the Kingdom, choosing a proven partner for Data Center Security KSA and Data Center Security Riyadh deployments is the single most important decision an operator can make.
Frequently Asked Questions
1. What is included in a complete Data Center Security strategy?
A complete strategy combines physical layers, including Data Center Access Control and Data Center Surveillance, with digital protections such as Data Center Firewalls and Data Center Encryption, unified under a single monitoring platform.
2. How is Cybersecurity for Data Center different from traditional IT security?
Cybersecurity for Data Center treats physical security devices, such as badge readers and cameras, as networked assets that require the same protection as servers, converging physical and digital monitoring into one operations center.
3. Why is Data Center Intrusion Detection important if I already have surveillance cameras?
Cameras record what happens; Data Center Intrusion Detection sensors, including door and occupancy sensors, actively alert security teams the moment an anomaly occurs, closing gaps that passive video coverage leaves behind.
4. What makes Data Center Threat Detection “predictive” rather than reactive?
Data Center Threat Detection platforms analyze access and network behaviour patterns to flag unusual activity before it becomes a breach, rather than only alerting after an incident has already occurred.
5. Do regional considerations really change how Data Center Security KSA or Data Center Security Riyadh projects are designed?
Yes. Climate, facility type, and regulatory obligations vary across Saudi regions, so a provider with local, certified engineers can design region-specific solutions for Data Center Security KSA and Data Center Security Riyadh rather than a one-size-fits-all deployment.
For more information contact us on:
Tektronix Technology Systems
+966 5021 04086
Building No. 8194, Additional No. 4368, Office No. 21, Third Floor
King Abdul Aziz Road, Al Rabie District
Riyadh 13315, Saudi Arabia

















Sign in to leave a comment.