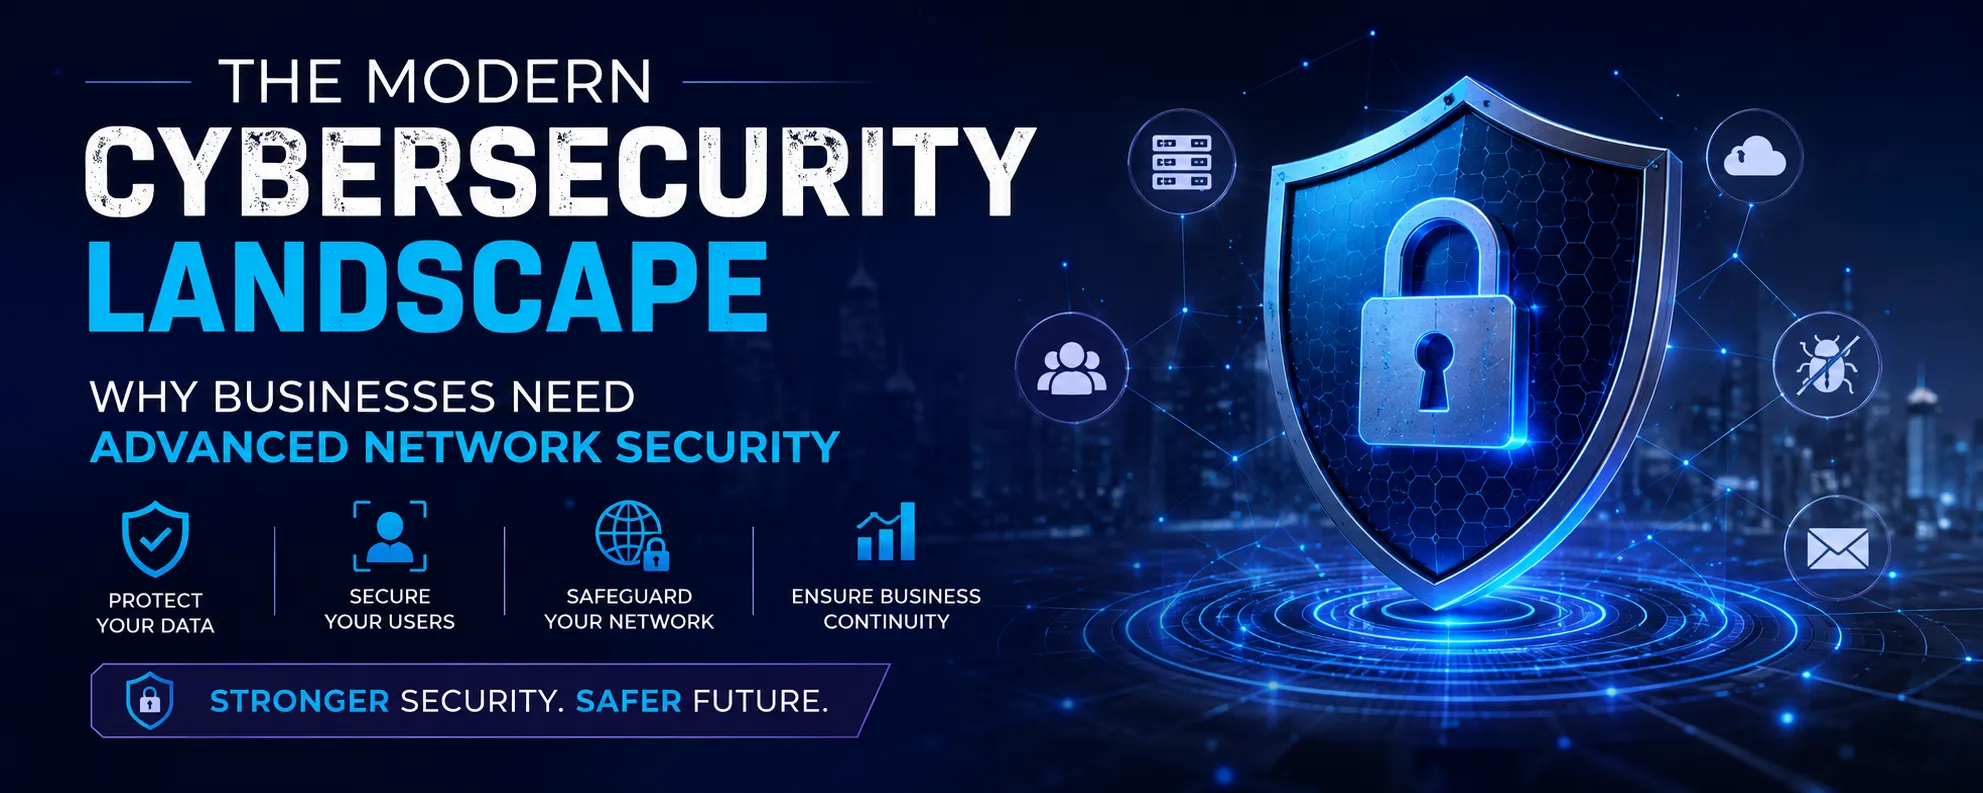

Cybersecurity is now a business resilience issue, not just an IT function. For Indian organisations managing hybrid work, cloud adoption, digital payments, customer data, and distributed branch networks, advanced network security helps reduce risk while keeping operations moving. The Modern Cybersecurity Landscape: Why Businesses Need Advanced Network Security comes down to one practical idea: businesses need visibility, speed, and disciplined processes before threats become disruptions.
Why has network security become a boardroom priority?
Network security has become a boardroom priority because cyber incidents can affect revenue, compliance, reputation, customer trust, and day-to-day service delivery. A ransomware event, data breach, or prolonged outage is not only a technical failure; it can interrupt sales, logistics, finance, manufacturing, healthcare delivery, or public-facing digital services. For decision-makers, the question is no longer whether security matters, but whether the organisation can detect, contain, and recover from attacks quickly enough.
In India, this pressure is amplified by rapid digitisation across sectors such as BFSI, healthcare, education, retail, manufacturing, and IT services. Many companies are modernising infrastructure while still running legacy applications, branch connectivity, third-party integrations, and cloud workloads. That mix creates a wider attack surface, where a single weak endpoint, misconfigured firewall rule, exposed cloud asset, or unpatched application can become a doorway into the enterprise.

The modern threat landscape is faster, broader, and more connected
Attackers today rarely rely on one obvious path. They combine phishing, stolen credentials, vulnerable web applications, unmanaged devices, cloud misconfigurations, and lateral movement inside networks. This is why advanced threat detection matters: it helps teams identify suspicious behaviour, not just known malware signatures or blocked connections.
For technical teams, this means correlating signals across endpoints, firewalls, identity systems, servers, applications, and cloud environments. For business leaders, it means investing in capabilities that reduce blind spots and shorten response time. A security alert that arrives too late, lacks context, or sits unattended can be almost as damaging as having no alert at all.
The shift is also cultural. Security can no longer be treated as a one-time deployment or annual audit activity. It must become an ongoing operating discipline, supported by monitoring, testing, response planning, user awareness, and continuous improvement.
Core layers of advanced network security
A strong security architecture is built in layers, so that failure in one control does not expose the entire organisation. While every business has different needs, mature enterprise network security usually includes several connected capabilities:
- Network visibility: Clear understanding of users, devices, applications, traffic flows, branch links, cloud connections, and privileged access paths.
- Secure connectivity: Well-designed LAN, WAN, wireless, VPN, SD-WAN, and segmentation policies that limit unnecessary exposure.
- Perimeter and internal controls: Firewalls, intrusion prevention, secure web access, email protection, endpoint security, and zero-trust-aligned access controls.
- Monitoring and correlation: SIEM-driven log collection and analysis across infrastructure, applications, endpoints, and identity systems.
- Continuous validation: Vulnerability Assessment and Penetration Testing, or VAPT, to identify exploitable weaknesses before attackers do.
- Incident readiness: SOC processes, escalation paths, playbooks, and managed response support to act quickly when something looks wrong.
Trace Network & Engineering Pvt Ltd works across these practical layers, bringing together Cybersecurity, Cloud, Networking, and Managed Services for organisations that need both implementation depth and operational support. This integrated view is important because a security tool is only useful when it is correctly designed, configured, monitored, and maintained.
What should Indian businesses prioritise first?
Indian businesses should first prioritise visibility, risk-based controls, and response readiness. Before buying more tools, organisations need to know what they own, what is exposed, which systems are business-critical, and where the biggest operational risks sit. Once that baseline is clear, technology investments become more targeted and easier to justify.
A practical starting point looks like this:
- Map critical assets and data flows. Identify key applications, user groups, cloud workloads, databases, payment systems, and third-party connections.
- Assess current exposure. Use VAPT, configuration reviews, and access audits to find gaps in applications, networks, endpoints, and cloud environments.
- Strengthen identity and access. Enforce least privilege, multi-factor authentication, privileged access control, and regular access reviews.
- Improve monitoring. Centralise logs through SIEM and define meaningful alert rules aligned with real business risks.
- Prepare response workflows. Establish who investigates, who approves containment, who communicates, and how recovery is handled.
- Review regularly. Security posture changes whenever the business adds users, branches, applications, vendors, or cloud services.
This approach helps bridge the gap between technical control and business outcome. IT teams get clearer priorities, while leadership gets a defensible roadmap tied to risk reduction rather than isolated product purchases.
The role of VAPT, SIEM, and SOC in everyday resilience
VAPT, SIEM, and SOC functions form a useful cycle: test, monitor, detect, respond, and improve. VAPT reveals weaknesses in systems, networks, and applications. SIEM brings logs and events into a central platform for correlation. SOC operations help ensure alerts are triaged, investigated, and escalated rather than lost in inboxes or dashboards.
For example, a VAPT exercise may uncover an exposed service or weak authentication flow. The remediation may involve patching, firewall policy changes, application fixes, or access control improvements. After that, SIEM use cases can be tuned to detect similar behaviour in the future, while SOC workflows define how the team should respond if the risk reappears.
Trace Network & Engineering Pvt Ltd’s capability sits in connecting these pieces rather than treating them as separate activities. A typical engagement may begin with assessment and network design review, move into security control implementation, and continue through managed monitoring or support. That continuity matters for organisations that do not want strategy, deployment, and operations to live in disconnected silos.
Cloud and networking decisions now shape security outcomes
Cloud adoption has changed the security perimeter. Business applications may sit across private data centres, public cloud platforms, SaaS tools, and remote user devices. In this environment, cloud architecture and network architecture directly influence cyber risk.
A secure cloud journey requires more than migration. It requires identity controls, secure connectivity, workload segmentation, backup planning, logging, encryption, and configuration discipline. Similarly, enterprise networking decisions around wireless access, switching, routing, branch connectivity, and segmentation affect how easily an attacker can move if an account or device is compromised.
This is where ecosystem knowledge becomes valuable. Trace Network & Engineering Pvt Ltd works with technology environments involving partners such as HPE Aruba, Sophos, Dell, Palo Alto, and similar enterprise platforms. The benefit is not simply access to products; it is the ability to align networking, security, cloud, and managed services into an architecture that fits the organisation’s operations and growth plans.
Cybersecurity best practices that still make the biggest difference
Even advanced environments depend on disciplined basics. Many incidents become serious because simple controls were missing, outdated, or inconsistently applied. Cybersecurity best practices should be treated as operating habits, not a checklist completed once.
Focus on the fundamentals that compound over time:
- Keep systems, firmware, and applications patched based on risk and business criticality.
- Segment networks so that users, guests, servers, operational systems, and sensitive assets are not unnecessarily exposed to one another.
- Use strong authentication, especially for administrators, remote access, cloud consoles, and business-critical applications.
- Back up important data and test restoration, not just backup completion.
- Train users to recognise phishing, suspicious links, unusual payment requests, and social engineering.
- Review firewall rules, privileged accounts, and cloud permissions regularly.
- Document response playbooks so teams know what to do during an incident.
These practices are not glamorous, but they reduce the likelihood that a small weakness becomes a major outage. They also help technical and business teams speak the same language: risk, continuity, accountability, and improvement.
Building security as a long-term capability
The most resilient organisations treat cybersecurity as a capability they build over time. They combine strong architecture, skilled people, reliable processes, and continuous monitoring. They also accept that security must support the business, not slow it down unnecessarily.
For Indian enterprises, the goal is not to copy someone else’s security model. It is to create a practical roadmap that reflects business priorities, regulatory expectations, available skills, and operational realities. Whether the immediate need is VAPT, SIEM implementation, SOC support, cloud security, networking modernisation, or Managed Services, the right partner should help clarify risks and build a sustainable path forward.
Trace Network & Engineering Pvt Ltd brings a grounded, engineering-led perspective to that journey, with services spanning Cybersecurity, Cloud, Networking, and Managed Services. If your organisation is reviewing its security posture or planning the next phase of enterprise network security, consider exploring Trace’s services or starting a conversation with their team for practical guidance.























Sign in to leave a comment.