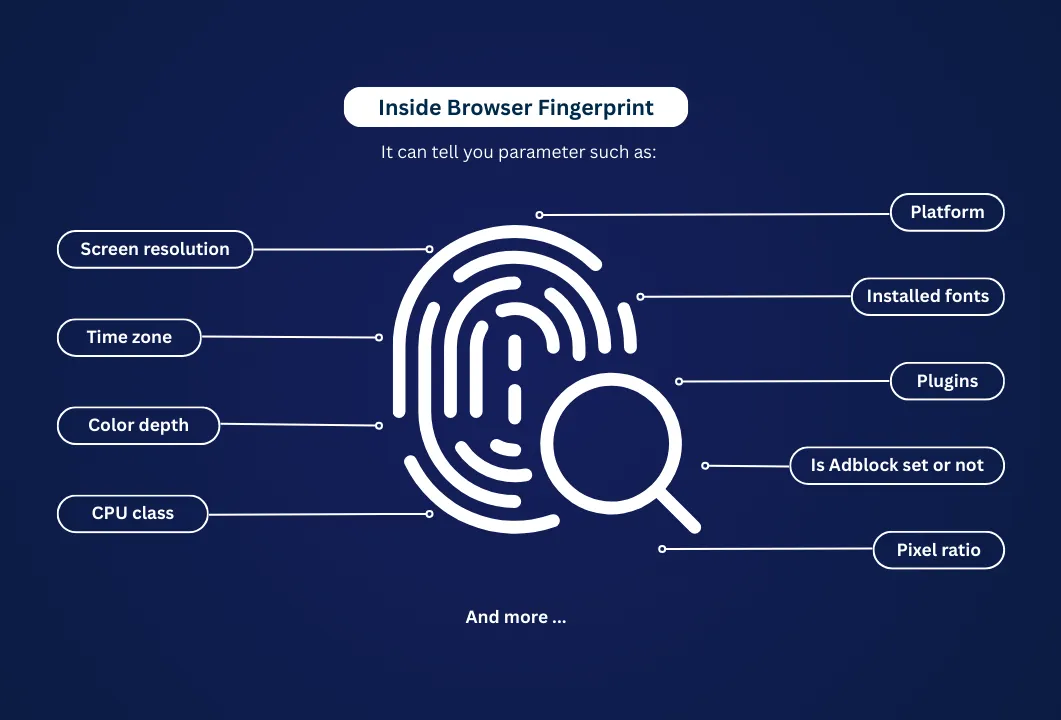

Every time you open a web page, your browser hands over far more data than most people realize, and much of it gets combined into what's called a browser fingerprint. None of it requires a password, a login form, or even a cookie banner click. It happens silently, in the background, through APIs that were built into browsers for legitimate reasons, and that websites, trackers, and ad networks now use to build a detailed profile of who you are, even if you've never created an account.
Understanding exactly what gets collected is the first step to controlling it. Here's a full breakdown of what a website can learn from your browser alone.
1. Network-Level Information
Before a page even finishes loading, the server already knows:
- IP address: reveals your approximate location, ISP, and sometimes your organization
- Connection type: mobile, broadband, VPN, proxy, or datacenter IP ranges (many sites flag known VPN/proxy ranges automatically)
- HTTP headers: including referrer, accepted languages, and connection details sent with every request
This is the layer most people try to hide first, usually with a VPN or proxy. But IP address is only one piece of the puzzle. The browser itself leaks far more.
2. Device and System Information
Through standard JavaScript APIs, a site can read:
- User agent string: browser name, version, and operating system
- Screen resolution and color depth
- Time zone and system language
- Number of CPU cores (navigator.hardwareConcurrency)
- Device memory (navigator.deviceMemory)
- Installed fonts: detected by measuring how text renders
- Battery status (on some browsers/versions)
Individually these look harmless. Combined, they narrow you down to a small group of devices out of millions.
3. Browser Fingerprinting
This is where things get serious. Fingerprinting techniques don't rely on cookies at all, which means clearing your cookies or browsing in incognito mode does nothing to stop them.
Canvas fingerprinting: the site draws invisible text or shapes on an HTML5 canvas element. Because rendering depends on your GPU, drivers, and OS, the resulting image differs slightly from device to device, creating a near-unique hash.
WebGL fingerprinting: similar to canvas, but reads GPU rendering details and graphics card information directly.
AudioContext fingerprinting: plays an inaudible audio signal through your device's audio stack and measures tiny variations caused by hardware and software differences.
Font enumeration: checks which fonts are installed by comparing text width/height across a list of font names.
ClientRects fingerprinting: measures pixel-level rendering of DOM elements, which varies subtly by rendering engine and OS.
When combined, these signals form a fingerprint that's often unique to a single device, accurate enough that changing your IP address or clearing cookies barely moves the needle. Sites like EFF's Cover Your Tracks or AmIUnique.org let you test how identifiable your own browser fingerprint currently is.
4. Storage-Based Tracking
Beyond fingerprinting, browsers offer several places to persist an identifier:
- Cookies: the classic method, first- and third-party
- LocalStorage / SessionStorage
- IndexedDB
- Cache-based tracking (ETags)
- Supercookies / evercookies: scripts that respawn a deleted identifier by storing copies across multiple storage mechanisms simultaneously
5. Behavioral Signals
Some sites go further and track how you interact with the page:
- Mouse movement patterns and click speed
- Typing cadence and scroll behavior
- Time spent on page, tab-switching frequency
These signals are increasingly used by anti-fraud and bot-detection systems to distinguish humans from automation, and in stricter systems, to link separate accounts that "behave" the same way.
6. WebRTC Leaks
Even behind a VPN or proxy, WebRTC (a protocol used for video calls and peer-to-peer connections) can expose your real local and public IP address directly through the browser, bypassing your VPN tunnel entirely if not properly configured.
Why This Matters Beyond Privacy
For most casual users, browser fingerprinting mainly means more targeted ads. But for anyone managing multiple accounts on the same platform (e-commerce sellers, agencies running paid social ad accounts, affiliate marketers, or researchers doing market analysis), it's a much bigger problem. Platforms use exactly the signals above to detect that "different" accounts are actually being run from the same device, and link or ban them together, even when each account uses a separate IP.
Clearing cookies, using incognito mode, or switching proxies doesn't solve this, because none of those touch canvas, WebGL, audio, or font fingerprints. The browser environment itself is the identifier.
How Antidetect Browsers Address This
This is the specific problem antidetect browsers like Hidemyacc are built to solve. Instead of just rotating an IP address, an best antidetect browser creates isolated browser profiles, each with its own independently randomized fingerprint:
- Separate canvas, WebGL, and audio fingerprint values per profile
- Distinct fonts, screen resolution, timezone, and hardware parameters
- Isolated cookies, local storage, and cache per profile, with no cross-contamination between accounts
- Built-in proxy integration, so IP and fingerprint are managed together rather than separately
- WebRTC leak protection, so the real IP never slips through
The result is that each browser profile looks, to a website's fingerprinting script, like a genuinely different physical device, not just a different IP behind the same computer. This is why fingerprint isolation matters more than IP rotation alone when managing multiple accounts.
Checking Your Own Exposure
If you want to see what your current browser is exposing right now, a few free tools are worth running:
- AmIUnique.org: shows how unique your fingerprint is compared to other visitors
- EFF Cover Your Tracks: tests both tracker blocking and fingerprinting resistance
- BrowserLeaks.com: breaks down canvas, WebGL, fonts, and WebRTC individually
FAQ
Does clearing cookies stop browser fingerprinting?
No. Fingerprinting techniques like canvas, WebGL, and audio fingerprinting don't rely on cookies or any stored data, so they survive cookie clearing, incognito mode, and even full browser resets on the same device.
Can a VPN alone protect against fingerprinting?
A VPN only hides your IP address. It does nothing to change your canvas, WebGL, audio, or font fingerprint, and without proper WebRTC leak protection, your real IP can still be exposed even while connected.
Is browser fingerprinting legal?
Fingerprinting itself isn't illegal in most jurisdictions, but regulations like GDPR and CCPA increasingly require disclosure and, in some cases, consent when it's used for tracking or profiling users.
How is an antidetect browser different from incognito mode?
Incognito mode only avoids saving local history and cookies after the session ends. It doesn't change the fingerprint the browser presents to a website. An antidetect browser actively generates a distinct, consistent fingerprint for each profile.
















Sign in to leave a comment.