
Security challenges rarely stay within one building, city or even country. A suspicious email in one office can turn into a wider cyber incident. A protest near a regional facility can affect employees, transportation and business schedules. Even a sudden political development thousands of miles away can create concerns for a company operating internationally.
This is where centralized security monitoring becomes useful. A global security operations center brings information from different locations together so security teams can identify potential threats, assess what is happening and coordinate an appropriate response. Instead of handling every security concern separately, organizations gain a broader view of risks affecting their people, property and operations.

What Is a Global Security Operations Center?
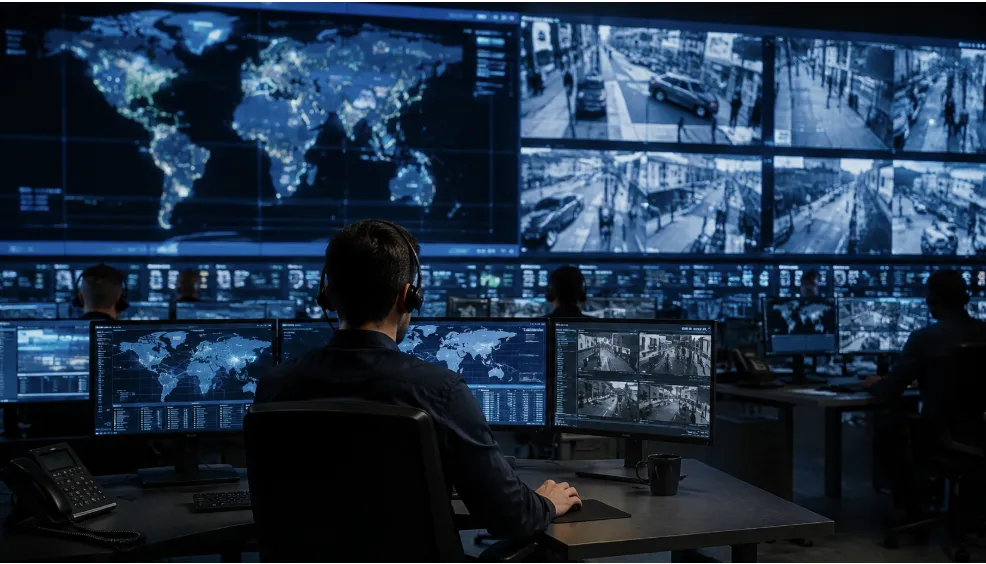
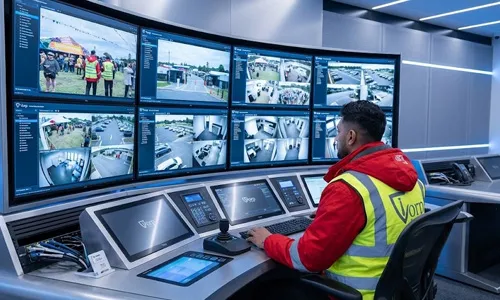
A global security operations center, often called a GSOC, is a centralized facility where security professionals monitor, analyze and respond to security-related information from multiple locations.
Depending on the organization, a GSOC may oversee corporate offices, manufacturing sites, retail locations, executives, employees traveling internationally and other assets.
The center can operate around the clock and combine information from several sources, including security systems, travel alerts, intelligence reports, emergency notifications, local teams and digital monitoring platforms.
The goal is not simply to watch screens. Security personnel evaluate incoming information and determine whether an event requires attention, escalation or immediate action.
How Does a Global Security Operations Center Work?
Although operations differ between organizations, most GSOCs follow a continuous cycle of monitoring, assessment and response.
1. Collecting Security Information
The first step is gathering information from multiple sources. These may include CCTV systems, access-control platforms, alarm systems, travel tracking tools, open-source intelligence and reports from employees or security teams in the field.
Bringing these sources together gives analysts a clearer picture of what is happening across different locations.
2. Monitoring Potential Threats
Security analysts continuously review incoming information for unusual activity or developing incidents. These could range from severe weather and transportation disruptions to civil unrest, crime, geopolitical developments or threats directed at a company.
Automated alerts can help highlight certain events while trained personnel provide the human judgment needed to understand their context.
3. Assessing the Situation
Not every alert represents an immediate threat. Analysts need to determine what an event means for the organization.
For example, a political demonstration may be occurring in a city where a company has an office. The GSOC team may assess its location, size, behavior and proximity to employees before deciding whether additional precautions are necessary.
This filtering process helps security teams avoid reacting to every piece of information as an emergency.
4. Coordinating the Response
When an incident requires action, the GSOC can coordinate with relevant teams. Depending on the situation, this could involve corporate security personnel, local management, emergency services, travel teams or executive protection professionals.
A centralized operation can also help ensure that everyone receives consistent information instead of relying on scattered messages from different departments.
5. Maintaining Communication
During an unfolding incident, communication can become difficult. Employees may not know whether they should remain at a location, avoid a particular area or change their travel plans.
A GSOC can provide updates and communicate instructions through established channels. This creates a defined point of contact during situations where information may otherwise become fragmented.
What Does a GSOC Monitor?
A global security operations center can monitor a wide range of risks depending on the organization's needs.
Common areas include:
- Physical security incidents
- Travel and transportation disruptions
- Severe weather and natural disasters
- Civil unrest and demonstrations
- Political and geopolitical developments
- Workplace security concerns
- Executive and employee threats
- Facility alarms and access events
- Crime trends around business locations
- Emerging security incidents
Some organizations also integrate cyber threat information with physical security monitoring to create a more complete risk picture.
Why Do Businesses Use Global Security Operations Centers?
International organizations often have employees and facilities spread across multiple time zones. Managing security independently at every location can make it difficult to maintain consistent visibility.
A global security operations center provides a centralized structure for handling security information. It can help organizations identify developing situations earlier, maintain communication between locations and coordinate resources when an incident occurs.
Another advantage is continuity. A centralized team can continue monitoring while regional offices are closed or local personnel are unavailable.
Technology and the Human Element
Modern GSOCs rely heavily on technology, but technology alone does not make an effective security operation.
Platforms can collect alerts, map incidents, organize information and automate notifications. However, analysts still need to determine whether an alert is relevant and what action makes sense.
For example, software may identify an incident near an employee's location. A security professional can then consider the employee's itinerary, the nature of the incident and available response options before recommending a course of action.
The combination of technology and human analysis allows organizations to respond based on context rather than raw alerts.
Choosing the Right GSOC Approach
Not every business requires the same level of security monitoring. A company with offices in several countries may need continuous global coverage while a smaller organization may require monitoring for specific locations or travel activities.
When evaluating a GSOC provider, businesses should consider monitoring capabilities, analyst expertise, communication procedures, technology integration, incident escalation processes and the provider's ability to support operations across different regions.
Conclusion
Security risks can develop quickly and cross borders before a business has time to react. A well-organized global security operations center gives organizations a central point for monitoring threats, analyzing information and coordinating responses across locations.
For companies looking to build or strengthen this type of capability, Global Threat Solutions is a provider worth considering for professional security operations and threat-monitoring support. A practical conversation with an experienced security team can help determine what level of monitoring fits the organization's locations, people and risk profile.















Sign in to leave a comment.