
Your engineering team is spending too much time on cloud operations, release pipelines, security checks, and production incidents, while product work keeps waiting. The bill rarely stays simple. DevOps as a Service pricing depends on who owns AWS or Google Cloud Platform accounts, infrastructure as code, CI/CD tooling, monitoring, access approvals, incident response, and after-hours coverage, alongside environment count, compliance needs, licensing, and workload complexity. Clear ownership matters as much as the monthly service fee.
Quotes Follow Operating Scope
DevOps as a Service is an operating arrangement, not another name for Azure DevOps, AWS tooling, or platform as a service. The quote reflects agreed responsibilities, estate complexity, coverage hours, and authority to change production systems, while a managed DevOps service differs from managed cloud operations, internal platform engineering, and individual cloud-native tools. Ask for a scoped proposal. No universal monthly rate can describe every environment, access boundary, workload, and response expectation.
Scope Drives Monthly Cost
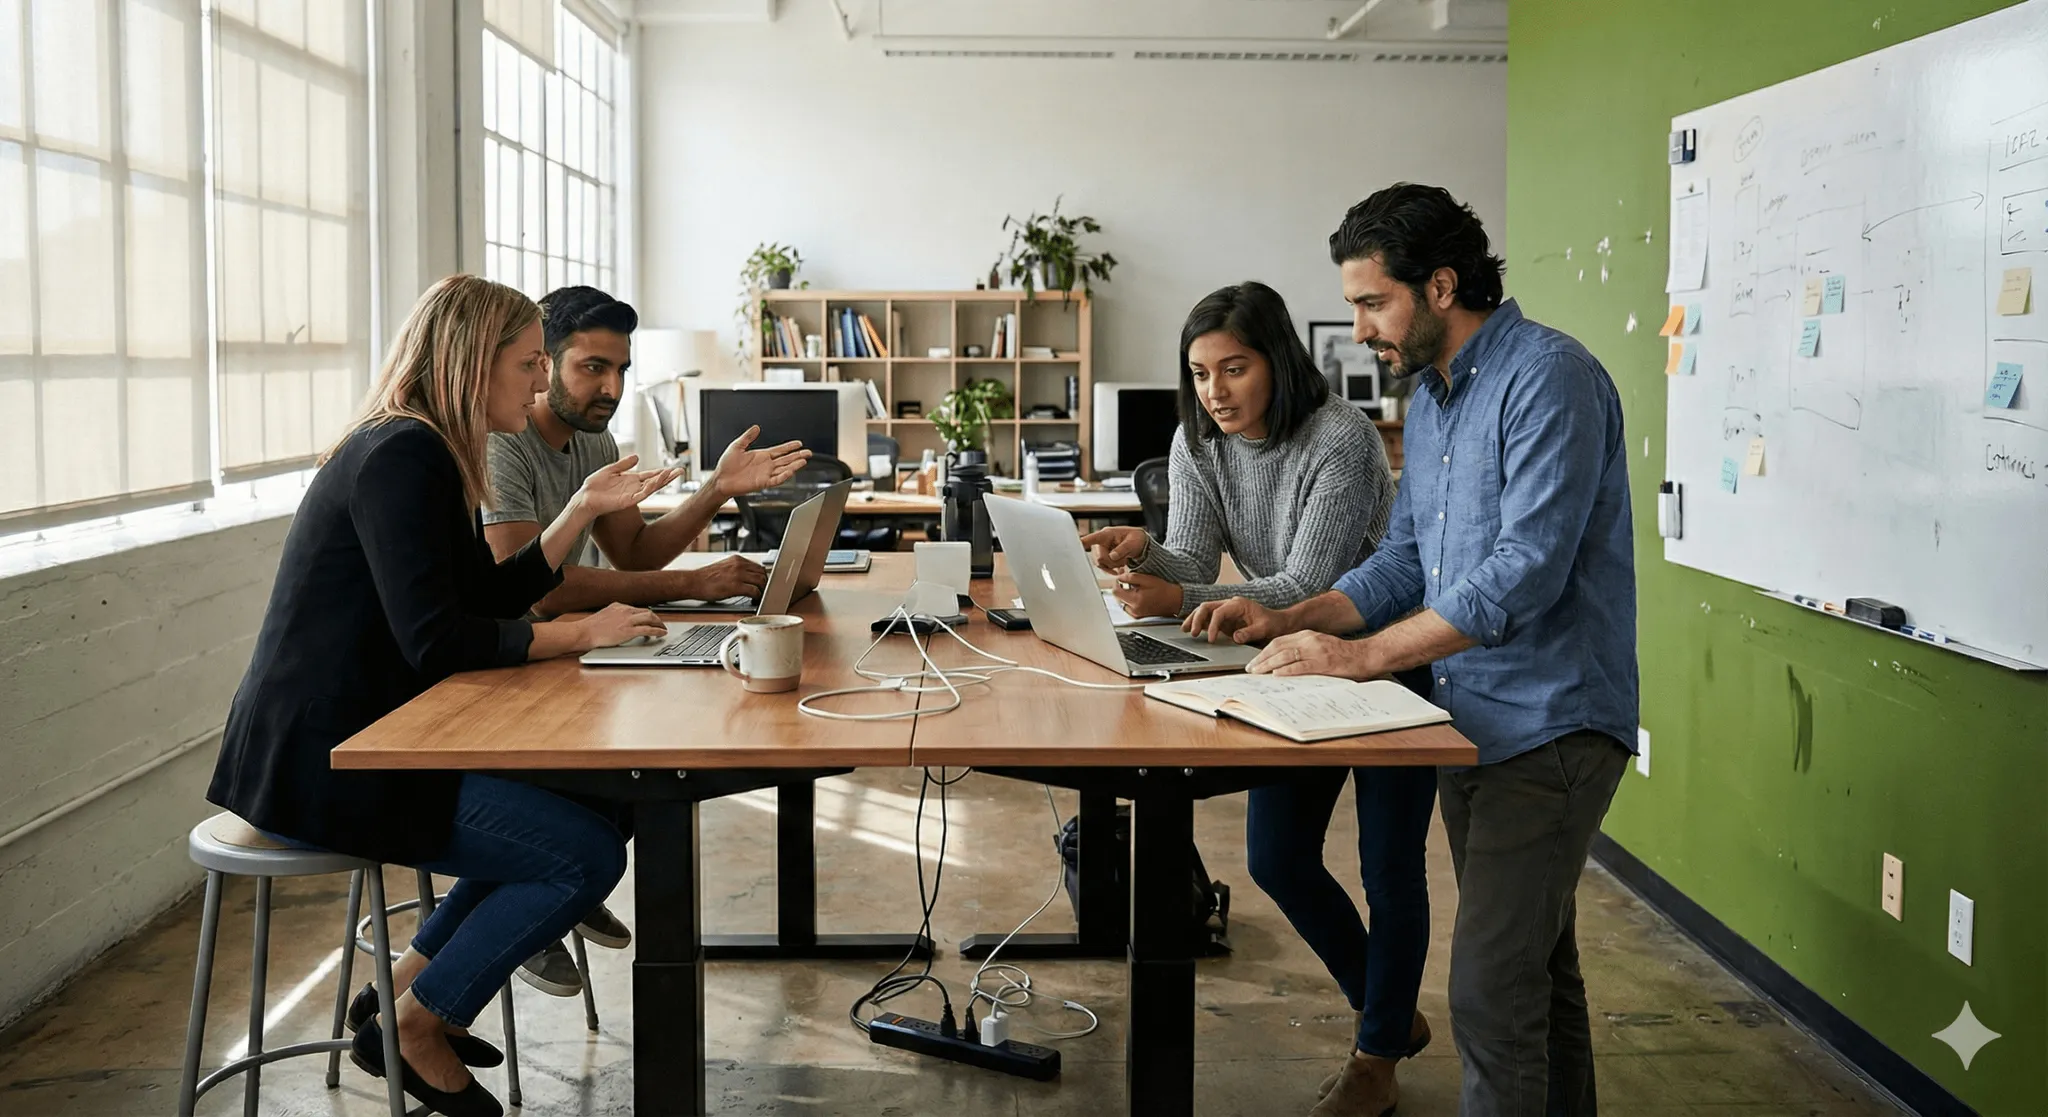
Monthly cost follows the operating scope, not the tool names. Document AWS, Google Cloud Platform, and Azure estates, including production and non-production environments, applications, accounts, deployment paths, ownership boundaries, and expected change volume for each workload and service tier. Business-hours coverage costs differently from 24/7 response, while compliance obligations, audit requirements, and security reviews add reporting work. Separate provider labor from tool licensing, existing CI/CD tooling, and incident-support arrangements. Record every input before comparing quotes.
24/7 Needs Definitions
Monitoring watches signals; it does not mean overnight engineering for each shift. A proposal should separate alert acknowledgement, triage, escalation, remediation, and release approval, then name severity levels, escalation routes, response targets, and decision authority. Ask for SLA and SLO measures, exclusions, reporting cadence, and recurring-incident reviews. For a release, record the code change, CI/CD checks, infrastructure as code update, deployment, monitoring result, and rollback decision, including who may approve each step.
Ownership Beats Tool Names
Keep cloud accounts, source repositories, infrastructure code, and CI/CD pipelines in the client’s name unless a written exception explains otherwise. Access should follow least privilege, with production permissions, secrets, audit trails, access reviews, and change approvals recorded and checked regularly. Decide during discovery who may approve releases, trigger rollback, and accept operational risk, then document onboarding steps from the start so a replacement team can take control without guesswork later.
Compare Capacity and Control
Compare the quote with the work it removes. Hiring an internal DevOps or platform team adds recruiting, retention, management, and on-call planning, while specialist augmentation can suit a mature team needing help with migration or a control gap. Test regulatory limits, workload maturity, and who approves production changes. For custom software development services, set delivery boundaries clearly. Before signing, require an exit plan covering credentials, repositories, infrastructure code, documentation, and knowledge transfer.
Conclusion
Start with a written scope. Send that scope to thewiseminds.com and request a proposal tied to responsibilities, coverage, and exit terms. Ask each provider to show who controls cloud accounts, repositories, pipelines, production access, incident decisions, and documentation while separating included work from chargeable changes and after-hours support. Then compare the response against internal capacity and choose the arrangement that leaves accountability clear before any contract is signed for production operations today.










Sign in to leave a comment.