
Robust Data Center Security has moved from a back-office checklist item to a board-level priority as the UAE races to build the region's cloud, AI, and hyperscale infrastructure. With Dubai and Abu Dhabi positioning themselves as global digital economy hubs, facility operators can no longer treat physical and digital protection as separate disciplines — the two must operate as one coordinated defense.
This guide examines where facility protection is heading across the UAE, the layered defenses every modern facility should have in place, and how operators in Dubai, Abu Dhabi, and beyond can build a security posture that satisfies regulators, enterprise tenants, and increasingly sophisticated threat actors alike.
Why Data Center Security Is a National Priority in the UAE
The UAE's push to become a global cloud and AI infrastructure hub — backed by significant hyperscale investment and national digital-economy strategies — has placed facility protection under a level of scrutiny it never faced when data centers served purely local enterprise needs. International cloud providers, government tenants, and financial institutions now expect UAE facilities to meet the same protection standards found in mature markets, from redundant physical barriers to continuous digital threat monitoring.
At the same time, the threat landscape has grown more complex. Nation-state actors, ransomware groups, and insider threats increasingly target the physical and network layers together, probing for the weakest link rather than attacking a single vector in isolation. A facility that hardens its firewalls but leaves a loading dock unmonitored, or that installs cameras but never encrypts data at rest, is still exposed.
Cybersecurity for Data Center Operations: Beyond the Perimeter Fence
Modern Cybersecurity for Data Center environments extends well past network firewalls and antivirus software. It now encompasses continuous vulnerability scanning across every connected system — building management platforms, HVAC controllers, and power distribution units included — because attackers have repeatedly shown they will pivot through an unpatched IoT device to reach far more sensitive systems.
Segmentation plays a central role here. Isolating operational technology networks from corporate IT, and further isolating tenant environments from one another in a colocation facility, limits how far an attacker can move laterally once they gain an initial foothold, containing an incident before it escalates into a facility-wide outage.
Data Center Encryption: Protecting Information at Rest and in Transit
Even with strong perimeter and network defenses, information itself needs independent protection. Data Center Encryption ensures that data stored on disk, moving between racks, or transmitted to a disaster-recovery site remains unreadable to anyone without the correct decryption keys — including, in a worst-case scenario, an attacker who has already breached the network perimeter.
UAE operators serving government or financial-sector tenants increasingly need to demonstrate not just that encryption is in place, but that key management follows documented rotation schedules, hardware security modules protect the keys themselves, and encryption standards align with national cybersecurity expectations for regulated data.
Data Center Firewalls: The First Line of Digital Defense
Next-generation Data Center Firewalls do far more than block unauthorized ports. Modern appliances inspect traffic at the application layer, apply behavioural analysis to catch anomalies that signature-based rules would miss, and enforce microsegmentation policies that treat every internal connection with the same scrutiny once reserved only for external traffic — an approach commonly described as zero-trust architecture.
For multi-tenant facilities, firewall policy also needs to enforce strict tenant isolation, ensuring that a security incident affecting one customer's environment cannot spread laterally into a neighbouring tenant's infrastructure hosted in the same facility.
Data Center Access Control: Securing the Physical Perimeter
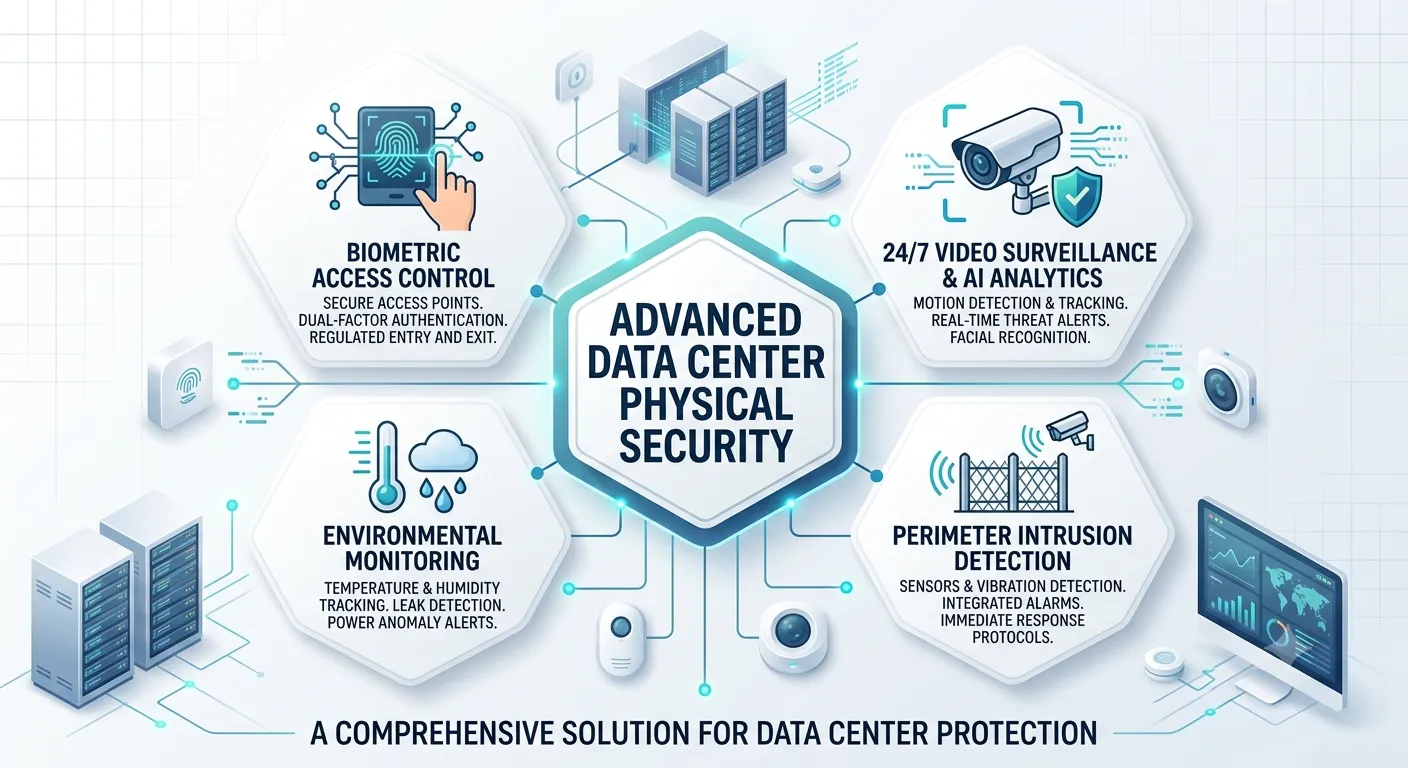
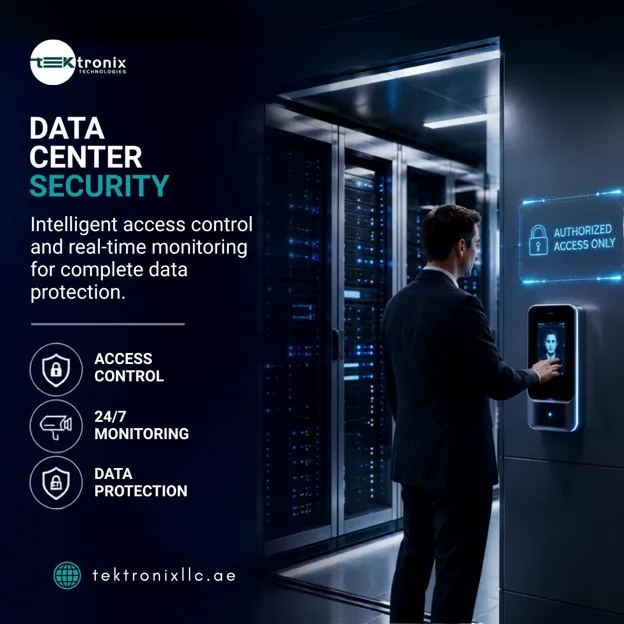
Digital defenses mean little if an unauthorized individual can simply walk into a server hall. Comprehensive Data Center Access Control layers multiple verification checkpoints — perimeter fencing, mantraps, biometric authentication, and cabinet-level locking — so that reaching a physical server requires passing through several independent barriers, each logged and auditable, rather than a single door with a shared key.
- Perimeter fencing and vehicle barriers to control site-wide entry before reaching the building.
- Mantrap vestibules that require successful authentication before a second door will open.
- Biometric verification at server-hall entrances for staff with elevated clearance.
- Individually locked and monitored server cabinets for tenant-specific isolation.
- Two-person authorization rules for access to the most sensitive infrastructure zones.
Data Center Surveillance: Continuous Visual Verification
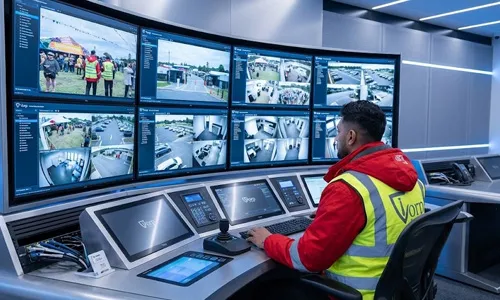
Access logs tell you who badged through a door; camera coverage confirms what actually happened at that door. Comprehensive Data Center Surveillance combines high-resolution cameras at every entry point, server row, and loading dock with AI-based video analytics that flag tailgating attempts, unattended packages, or a badge being used by someone who does not visually match the enrolled profile — turning passive recording into an active detection layer rather than only forensic evidence reviewed after an incident.
Footage retention policies matter as much as camera placement. Facilities serving regulated tenants typically need to retain recordings for a defined period and demonstrate a tamper-evident chain of custody in case footage is required for an investigation or compliance audit.
Data Center Intrusion Detection: Catching Breaches in Real Time
Whether the intrusion is physical or digital, speed of detection determines how much damage occurs before a response begins. A properly tuned Data Center Intrusion Detection system monitors for forced doors, unexpected motion in server halls after hours, and abnormal network traffic patterns simultaneously, correlating physical and digital signals so that a badge-cloning attempt paired with unusual network activity from the same zone triggers an immediate, high-priority alert rather than two disconnected, low-priority log entries.
Data Center Threat Detection: Staying Ahead of Evolving Attack Patterns
Beyond reacting to intrusions already underway, mature Data Center Threat Detection programs actively hunt for early warning signs — reconnaissance scans probing for open ports, credential-stuffing attempts against administrative logins, or subtle changes in power and cooling telemetry that could indicate tampering with physical infrastructure. Machine-learning models trained on a facility's normal operating baseline can flag these deviations long before they escalate into a full breach or outage.
Threat intelligence sharing across the region is also gaining traction, with UAE operators increasingly participating in information-sharing partnerships that surface attack patterns observed at one facility before they are attempted against another, shortening the window attackers have to exploit a known technique.
Data Center Security UAE: Regulatory Landscape and Compliance
Operators pursuing Data Center Security UAE -wide compliance must navigate a regulatory framework that includes national cybersecurity guidance, federal data protection regulations governing how personal information is stored and processed, and sector-specific requirements for facilities hosting government or financial-services workloads. Documentation matters as much as the technology itself — auditors expect evidence of tested incident-response plans, regular penetration testing, and clearly assigned accountability for both physical and digital security domains.
Data Center Security Abu Dhabi: Protecting the Capital's Critical Infrastructure
As the UAE's political and administrative capital, Abu Dhabi hosts a dense concentration of government ministries, sovereign wealth institutions, and major enterprise data centers that carry outsized national significance. Data Center Security Abu Dhabi deployments typically face higher regulatory scrutiny and larger attack surfaces than smaller regional facilities, making layered physical barriers and continuous digital monitoring non-negotiable rather than optional upgrades reserved for later phases.
Data Center Security Dubai: Safeguarding a Global Commercial Hub
Dubai's role as a global trade, finance, and technology hub gives the city's data center sector a distinct risk profile, hosting facilities that serve multinational cloud providers, major banks, and rapidly growing technology firms. Data Center Security Dubai facilities benefit from hardened physical enclosures suited to the region's climate, alongside the same rigorous access-control and surveillance layers expected across the UAE's other major data hubs, including Abu Dhabi and the Northern Emirates.
How Tektronix Delivers Layered Data Center Protection Across the UAE
Tektronix has spent years designing and deploying physical and digital security infrastructure for data centers, enterprise clients, and critical facilities across the UAE and the wider Gulf. Our engineering team combines hands-on deployment experience with a deep understanding of regional compliance requirements, giving facility operators a partner who can design protection around real operational risk rather than a generic template.
Facility operators evaluating their security posture can review our full data center perimeter security solutions for the UAE to see how perimeter, access, surveillance, and cyber defenses combine into a single, coordinated protection strategy.
Our deployments integrate biometric access control, AI-enabled surveillance analytics, and network-layer defenses into one coherent security operations view, so facility teams are not left correlating alerts across a dozen disconnected dashboards during an active incident. Every project includes local onboarding, staff training, and ongoing technical support tailored to the facility's specific risk profile.
For a detailed breakdown of how our layered facility protection methodology addresses both physical intrusion and network-based threats, explore the dedicated solution page linked above.
Operators who have implemented our layered approach consistently report faster incident correlation between physical and digital alerts, cleaner audit trails during regulatory inspections, and measurably fewer unauthorized access attempts reaching sensitive server halls compared to facilities relying on disconnected point solutions.
Why Vendor Experience Matters for Critical Infrastructure Security
Data center protection sits at the intersection of national infrastructure resilience and enterprise risk management, so vendor selection deserves the same rigor as the technology architecture itself. Facility operators should ask prospective integrators how long they have secured critical infrastructure in the UAE market, request references from comparable facilities, and confirm how incident response, patching, and 24/7 monitoring support are structured once the deployment goes live.
A provider that documents real project history, holds relevant security certifications, and maintains a locally based response team is far more likely to deliver protection that holds up under an actual attack, rather than one that performs well only in a controlled sales demonstration.
Best Practices for Building a Future-Ready Security Program
- Treat physical and digital security as one integrated program with shared incident-response procedures.
- Run regular penetration tests and physical red-team exercises rather than relying on point-in-time audits alone.
- Segment networks and physical zones so a single compromised credential cannot expose the entire facility.
- Maintain documented, tested disaster-recovery and incident-response plans reviewed at least annually.
- Continuously monitor emerging regional threat intelligence to adapt defenses ahead of new attack patterns.
Facilities that revisit their security architecture on a regular cycle — rather than treating a single deployment as a permanent solution — remain resilient as both regulatory expectations and attacker techniques continue evolving across the region.
Conclusion
Building a more secure digital future depends on treating Data Center Security and Cybersecurity for Data Center operations as one system across the UAE. Strong Data Center Encryption, modern Data Center Firewalls, and layered Data Center Access Control must work alongside continuous Data Center Surveillance, Data Center Intrusion Detection, and proactive Data Center Threat Detection. Facilities pursuing Data Center Security UAE compliance, or hardening Data Center Security Abu Dhabi and Data Center Security Dubai sites, achieve the strongest resilience with an experienced regional security partner.
FAQs
1. What does comprehensive Data Center Security actually include?
Comprehensive Data Center Security combines physical layers such as perimeter fencing, mantraps, and biometric access with digital defenses including firewalls, encryption, and continuous threat monitoring, treated as one coordinated program rather than separate initiatives.
2. How does Cybersecurity for Data Center operations differ from standard corporate IT security?
Cybersecurity for Data Center environments must protect operational technology systems like power and cooling controllers alongside standard IT networks, and typically requires stricter tenant segmentation than a single-organization corporate network.
3. Why is Data Center Encryption important even with strong network defenses in place?
Data Center Encryption protects information even if an attacker breaches the network perimeter, ensuring stored and transmitted data remains unreadable without properly managed decryption keys.
4. What role does Data Center Access Control play in a multi-tenant facility?
In shared facilities, Data Center Access Control enforces cabinet-level and zone-level restrictions so one tenant's staff cannot physically reach another tenant's infrastructure, maintaining isolation alongside network-level segmentation.
5. How does Data Center Threat Detection identify risks before a breach occurs?
Data Center Threat Detection uses behavioural baselines and machine learning to flag reconnaissance activity, unusual login patterns, or abnormal infrastructure telemetry early, often well before an intrusion attempt fully develops.
For more information contact us on:
Tektronix Technology Systems Dubai-Head Office
+971 50 814 4086
+971 55 232 2390
Office No.1E1 | Hamarain Center 132 Abu Baker Al Siddique Rd – Deira – Dubai P.O. Box 85955














Sign in to leave a comment.