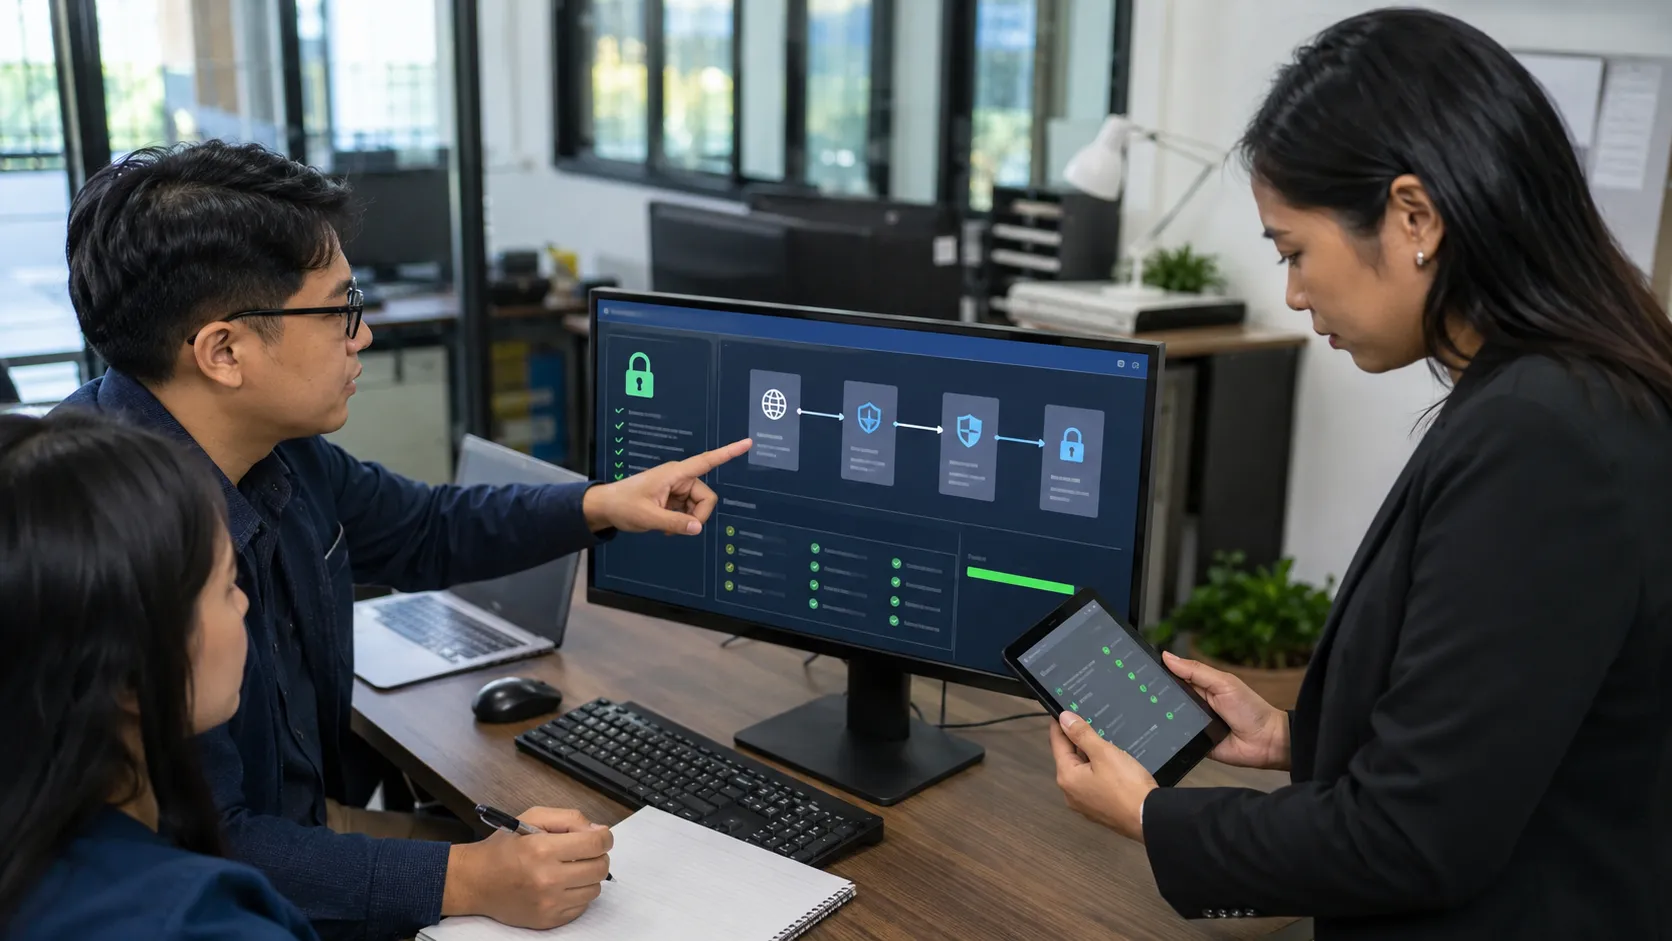

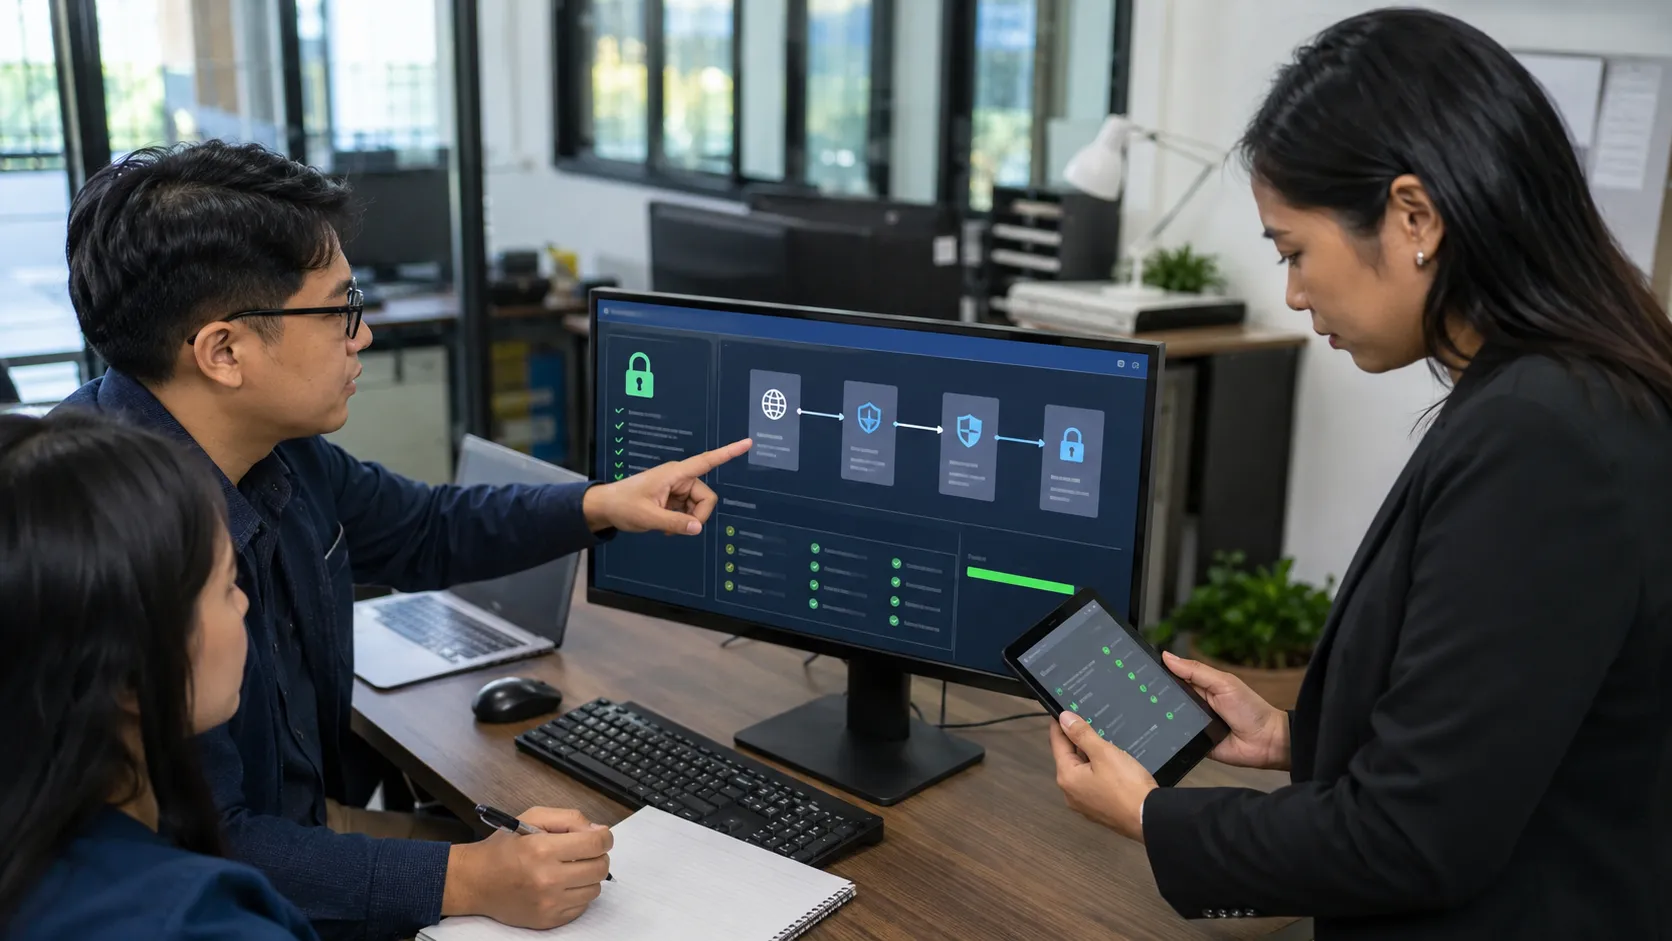
An SSL certificate renewal test record needs to identify the exact portal tested, the replacement certificate, the test conditions, the observed results, unresolved faults, and the officers responsible for technical and service approval. A local government unit (LGU) needs to complete this record before treating a renewed citizen portal as ready for public transactions. Teams reviewing the GoLGU SSL Certificate service need to bring their current domain list, renewal procedure, and release authority.
The record does more than confirm a future expiration date. It links one certificate replacement to the deployed hostname, citizen-facing routes, test evidence, correction work, and release decision. This scope keeps the review separate from broad website security assessments.
Why Does a Renewal Need Its Own Test Record?
A successful purchase or certificate issuance does not prove that the public server presents the replacement correctly. Installation errors still arise from a wrong hostname, a missing intermediate certificate, an old certificate served by another endpoint, an incomplete redirect, or an insecure page resource.
The LGU needs to preserve one dated account of what staff checked after deployment. Without that evidence, a later browser warning leaves the service office and Information and Communications Technology (ICT) team reconstructing events from email threads, screenshots, and vendor messages.
The record also separates three decisions. The technical reviewer confirms the certificate and server results. The service owner confirms that the citizen route works from entry through submission. The release authority accepts the outcome or holds the portal for correction. Combining those decisions in one unchecked status hides responsibility.
What Details Belong in an SSL Certificate Renewal Test Record?
The record follows the test from scope to decision. Group the information by purpose instead of collecting unrelated server details in one long form.
Which details identify the tested deployment?
Start with the public hostname, the environment, the installation date, and the approved change or service request used for the replacement. Record the certificate issuer, serial number or fingerprint, validity period, and covered domain names. The tester also identifies the server, load balancer, content delivery network, or hosting layer involved in the deployment.
Use a separate entry for each deployment state when several systems serve the same portal. A result from a staging server does not prove that production presents the same certificate. A result from the main domain also does not prove that a permit, payment, login, or document-upload subdomain passed.
Which facts explain how staff performed the test?
Record the test date and time, tester, device or client type, browser or tool version, network route, and tested URLs. A post-renewal HTTPS test must include the public route a citizen follows, not only a server command run inside the office network.
The evidence reference must point to an approved storage location. Store the result summary, certificate details, and failure evidence there. Do not place private keys, account passwords, session cookies, full citizen submissions, or unrelated personal data in the testing record.
Which fields show the final decision?
For each tested route, record the expected result, observed result, status, and evidence reference. If a fault appears, add the affected service, assigned owner, target correction date, and retest outcome. Finish with the technical reviewer, service owner, decision date, and release status.
The approved status terms need to stay short and defined. For example, the LGU might use Accepted, Held for Correction, and Accepted With Recorded Limitation. The approved procedure needs to explain who has authority to use each status and which conditions block release.
Which Tests Should Take Place After Certificate Replacement?
The test sequence begins from the citizen's route and then moves toward certificate details. This order exposes service failure before the team becomes focused on one technical result.
- Open every approved public hostname through a normal external connection. Confirm that the browser reaches the intended service without a certificate warning.
- Check the certificate subject alternative names against the exact hostnames in scope. A certificate for the main domain does not cover every subdomain unless the certificate lists or validly covers them.
- Confirm the active validity period, issuer, serial number or fingerprint, public key profile, and server-authentication purpose through an approved testing method.
- Inspect the chain sent by the server. LGUs needing a deeper chain review should use the same-domain guide on certificate chain completeness for citizen portals.
- Test the HTTP-to-HTTPS redirect and each approved alternate hostname. The destination should remain on the intended official domain.
- Complete a safe transaction path. Open the form, enter non-sensitive test values, submit through the designated test method, and confirm the expected response without placing a real citizen record at risk.
- Review images, scripts, stylesheets, embedded content, and application programming interface calls for insecure HTTP resources. Record any mixed-content warning as a failed condition.
- Repeat the critical route on the approved browser, mobile, and integration profiles. Save a separate result when client behavior differs.
The LGU SSL validation log should name the tools and versions used. A result such as “working” gives future reviewers little evidence. A stronger entry states the route, client, expected behavior, observed behavior, and evidence location.
Who Should Perform, Review, and Approve the Test?
The ICT or web administration team performs the technical checks. A hosting provider or developer corrects deployment faults when the approved contract assigns that duty. The service office tests the citizen transaction and reports whether the public route produces the expected service response.
The Data Protection Officer joins the review when the route processes personal data and a failure affects confidentiality, access, or exposure. NPC Circular No. 16-01 applies to government agencies, including LGUs, and requires controls suited to the risks involving personal data. It also requires encryption for personal data processed in transit.
An authorized technical officer approves the certificate result. The office responsible for the citizen service approves operational release. The approved change procedure should name a higher official for unresolved high-risk faults or disputed release decisions.
Keep vendor completion separate from LGU acceptance. A vendor's installation message proves the vendor reported completion. The LGU's certificate replacement verification proves whether the deployed public service met local test conditions.
How Should the LGU Handle a Failed Renewal Test?
A failed post-renewal HTTPS test should stop the affected release path when citizens face a warning, a wrong hostname, an invalid chain, an insecure redirect, or a broken submission. The test record should preserve the original result before correction begins.
Consider a city permit portal with separate login and payment subdomains. The main portal presents the renewed certificate, yet the payment subdomain still serves the older certificate. The ICT tester records the failing hostname, certificate fingerprint, observed warning, test client, and time. Treasury confirms that payment transactions should remain paused.
The hosting provider updates the certificate binding on the payment endpoint. A different staff member repeats the route from an external network and records the new result. The service owner then approves reopening after both the certificate check and the test payment route pass.
Do not replace the failed result with the later pass. Keep both states under one change reference. The first result explains why the service was held, while the second supports the approved release.
How Should Evidence Be Stored and Retained?
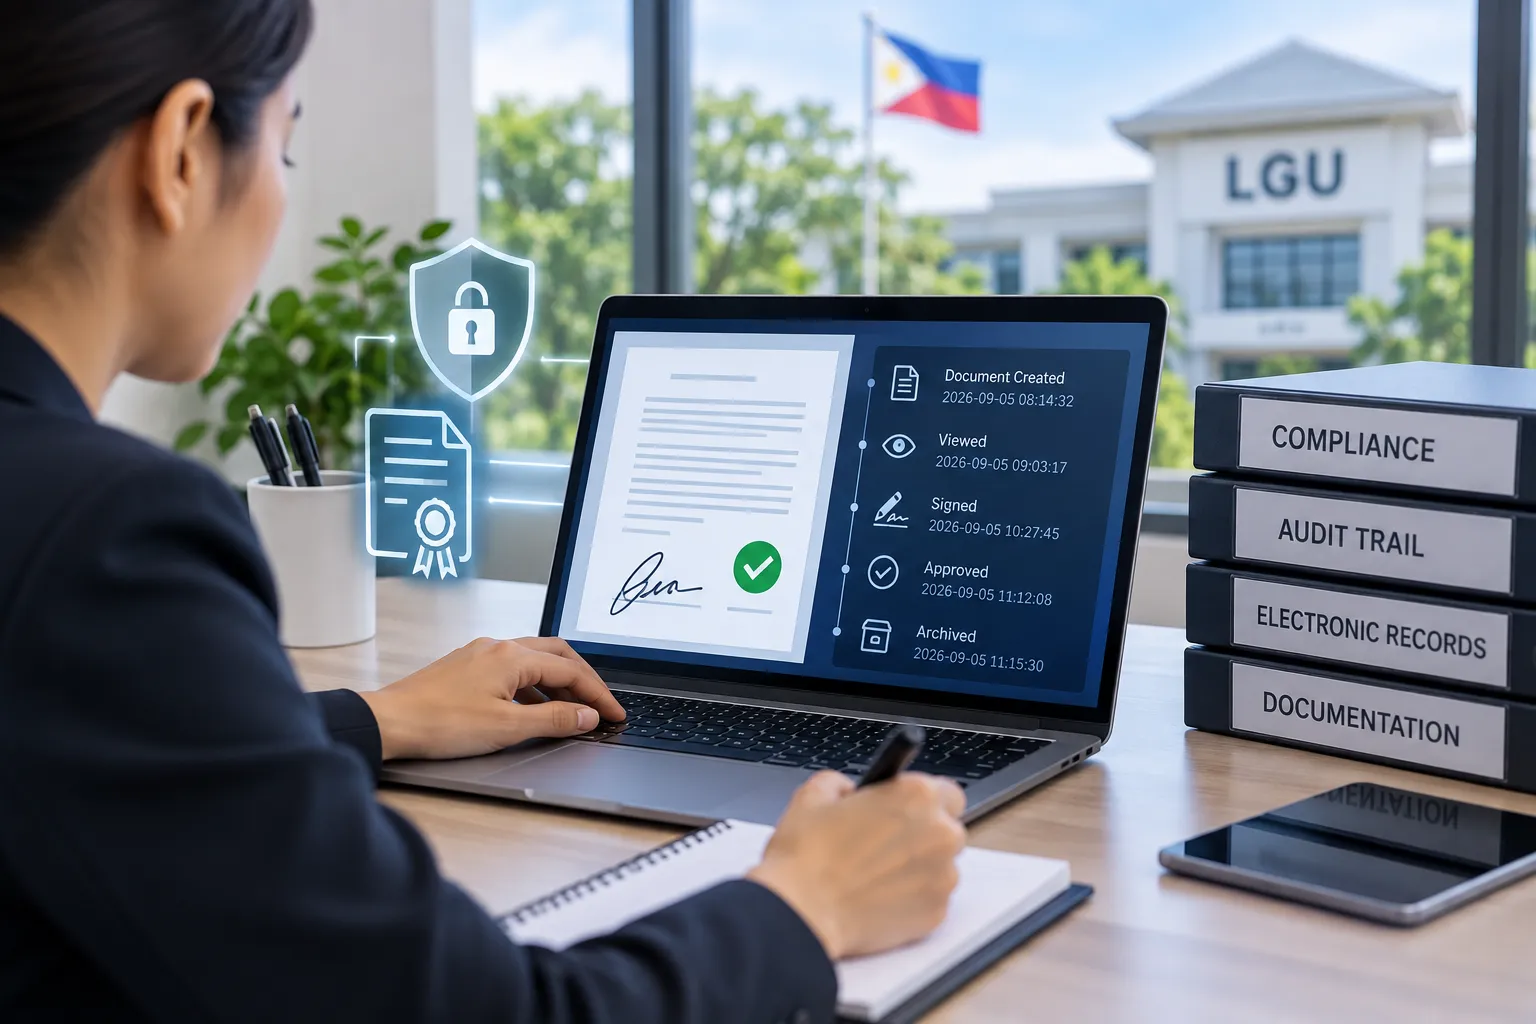
The LGU SSL validation log should point to evidence without turning into a collection of secrets. Suitable evidence includes a certificate summary, test output, redacted browser capture, route checklist, correction ticket, retest result, and signed decision. Keep the files in the approved evidence repository and restrict them to staff with assigned duties.
The LGU should set retention through its approved records schedule, security policy, contract requirements, and incident needs. No universal retention period applies to every certificate test. The records owner should document the retention trigger and disposal authority before evidence accumulates across several renewals.
Store each result under a stable naming rule tied to the hostname, deployment date, and change reference. This organization produces useful TLS renewal evidence during internal review, vendor dispute, incident analysis, or the next renewal.
How Does the Record Support Privacy and Digital Governance?
Republic Act No. 12254 covers LGUs and calls for reliable, secure, citizen-centered digital government services. A dated renewal record supports defined roles, accountable decisions, and evidence of a tested public-service route. The law does not prescribe one certificate-testing form, tool, or automatic approval rule.
NPC Circular No. 16-01 places responsibility on government agencies to protect personal data through appropriate organizational and technical measures. A citizen portal renewal check supports this duty when staff test encrypted access, restrict evidence, and address failures before normal processing resumes.
International technical guidance adds detail. NIST Special Publication 800-52 Revision 2 covers the selection and configuration of Transport Layer Security (TLS), including certificates and security-relevant extensions. The OWASP Transport Layer Security Cheat Sheet recommends testing hardened server configurations, matching certificates to correct domain names, and avoiding mixed secure and insecure content.
These sources guide the review, but the LGU should align the final procedure with its systems, supported clients, contracts, risk decisions, and current government guidance. The resulting TLS renewal evidence should show both the technical result and the approved service decision.
What Is the Practical Next Step?
Select one citizen-facing hostname from the next renewal schedule. Prepare a one-page test record before the replacement date. Assign the tester, technical reviewer, service owner, evidence location, hold conditions, and final approver. Run the form first in a controlled environment, then revise unclear fields before production use. This certificate replacement verification should use the same approved scope during the final production check.
An LGU evaluating certificate support should request a GoLGU demonstration and bring its domain inventory, current renewal procedure, latest test evidence, and one recent browser-warning case. Those materials keep the discussion focused on the LGU's real portal routes and responsibilities. The completed citizen portal renewal check becomes part of the final evidence used for the release decision.
Frequently Asked Questions
Is checking the new expiration date enough after renewal?
No. The tester should also confirm hostname coverage, the served certificate, chain completeness, redirects, citizen routes, insecure resources, supported clients, and final service approval.
Does each subdomain need a separate result?
Yes, when the subdomain serves a distinct endpoint or deployment. The main domain's result does not prove that login, payment, upload, or application subdomains present the same certificate correctly.
Who signs the final renewal test decision?
The approved local procedure should identify the technical reviewer and service owner. A higher authority should decide unresolved exceptions according to the LGU's change and risk rules.
Should the record contain a private key or password?
No. Store certificate identifiers, test results, and evidence references. Keep private keys, passwords, session values, and real citizen submissions outside the record.
What happens when one browser passes and another fails?
Record both clients and results. Identify the affected certificate, chain, protocol, resource, or client condition. Hold the affected route until the responsible officer accepts a verified correction or a formally documented limitation.
When should the test be repeated?
Repeat the test after certificate replacement, server migration, load-balancer changes, content delivery changes, certificate authority changes, new subdomains, material hosting updates, and reported certificate warnings. The SSL certificate renewal test record links each new result to the affected deployment and decision.
References
- Republic Act No. 12254, E-Governance Act
- NPC Circular No. 16-01, Security of Personal Data in Government Agencies
- NIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations
- OWASP Transport Layer Security Cheat Sheet
Disclaimer
This guide provides general operational information for Philippine LGUs. Each LGU should confirm current laws, government guidance, contracts, security policies, records schedules, certificate issuer instructions, and authorized technical advice before applying a renewal procedure.








Sign in to leave a comment.