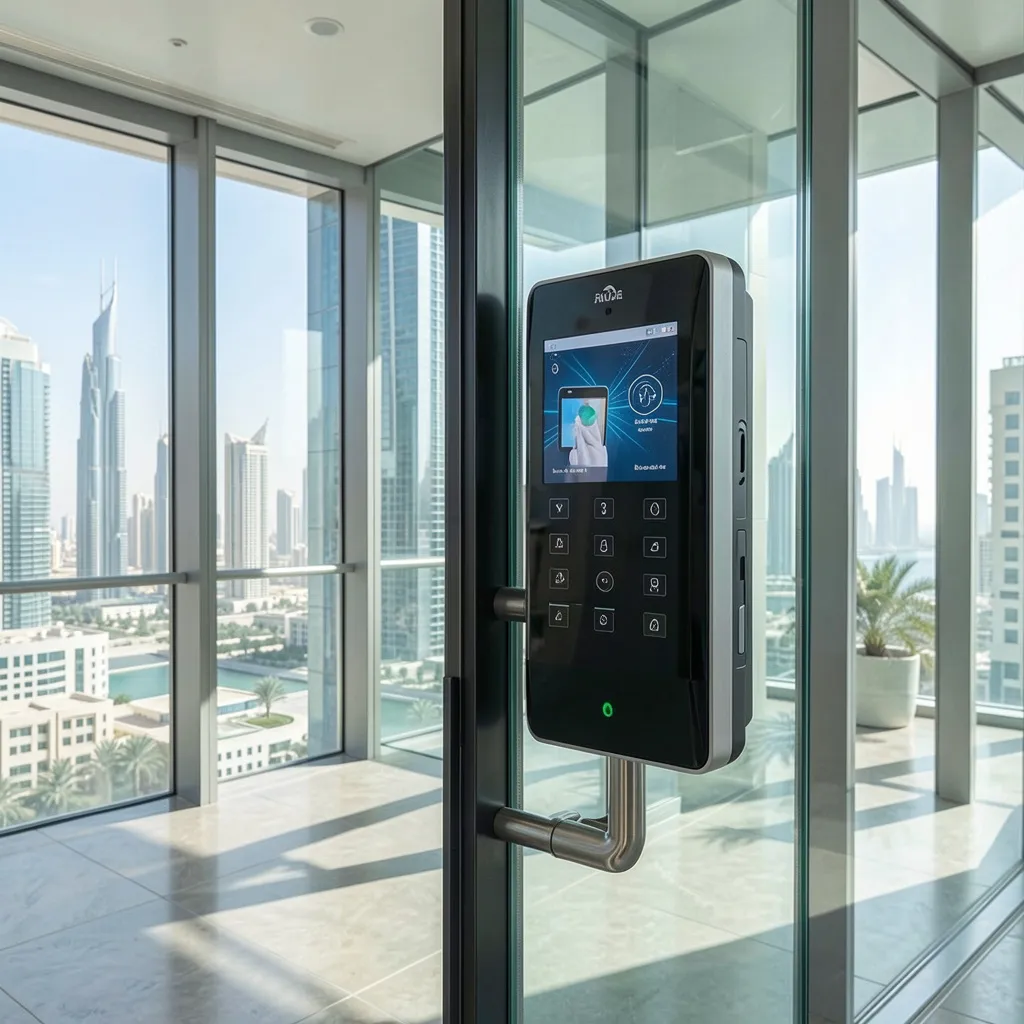

For a corporate security manager, an Access Control System is rarely evaluated as a single product decision — it's the operational backbone of the entire physical security program, the tool that turns written policy into something actually enforced at every door, every day, without requiring a guard to be physically present at each entry point.

This distinction matters considerably for how UAE corporate security teams should approach the technology. A door lock secures a door; an access control platform, properly implemented, becomes the mechanism through which a security manager can demonstrate policy compliance, respond to incidents with actual data rather than guesswork, and report meaningfully to leadership about the organization's physical risk posture — a fundamentally different, more strategic role than simply keeping unauthorized people out.
Access Control as a Security Management Discipline, Not Just Hardware
Security managers who treat access control purely as a hardware procurement decision — which reader, which lock, which card — often end up with a system that technically works but fails to support the broader security management function it should serve. The hardware is simply the enforcement mechanism; the actual discipline lies in the policy design, the ongoing governance of who has access to what, and the ability to answer detailed questions about the organization's security posture on demand.
This reframing matter practically. A security manager evaluating access control should be thinking as much about reporting capability, policy governance workflows, and incident investigation support as about the physical readers and locks themselves — since the value delivered to the organization comes primarily from the management layer, not the door hardware in isolation.
Building a Corporate Access Policy That the System Can Actually Enforce
Before any hardware decision, effective corporate security management starts with a clearly defined access policy — which roles need access to which zones, under what time restrictions, and with what approval workflow for exceptions. A system deployed without this groundwork tends to accumulate ad-hoc access grants over time, gradually eroding the very security posture the deployment was meant to establish.
Security managers should treat the access control platform as the enforcement layer for a policy they've already designed, rather than letting default system configuration dictate the policy by omission. This distinction between policy-first and hardware-first thinking is often what separates a genuinely effective corporate security program from one that merely has expensive access control equipment installed.
Core Technologies a Security Manager Should Understand
While the underlying policy work matters most, corporate security managers still need working knowledge of the core technologies available to implement that policy effectively.
Biometric Access Control Dubai Security Teams Deploy for the Highest-Risk Zones
For zones where the consequence of unauthorized access is genuinely severe — server rooms, executive offices, finance departments — Biometric Access Control Dubai security managers increasingly specify uses fingerprint, iris, or facial recognition, since these credentials cannot be shared or borrowed the way a card can. From a security management perspective, biometric verification also closes a specific policy enforcement gap: a card-sharing violation is difficult to detect after the fact, while biometric access inherently prevents it.
Security Access Control System Design as a Risk-Tiering Exercise
A well-designed Security Access Control System reflects a deliberate risk-tiering exercise carried out by the security management team — mapping every zone in the organization to an appropriate verification level based on genuine risk assessment, rather than applying uniform security everywhere or, worse, leaving zone-level decisions to whoever happened to configure the system during initial installation.
Door Access Control and the Audit Trail It Generates for Security Governance
At the individual door level, Door Access Control hardware does more than lock and unlock — every event it logs becomes raw material for security governance. A corporate security manager can use this data to verify policy compliance, investigate incidents, and identify unusual access patterns that might warrant closer review, turning routine door hardware into an ongoing source of security intelligence.
Mobile Access Control and the Administrative Burden It Removes from Security Teams
From a security management workload perspective, Mobile Access Control meaningfully reduces the administrative burden of credential lifecycle management — issuing, replacing, and revoking physical cards consumes real security team time that mobile credentials largely eliminate, freeing the team to focus on policy design, incident investigation, and other higher-value security management work instead.
Choosing an Access Control Device Based on Risk, Not Just Convenience
Security managers selecting an Access Control Device for a specific zone should weigh the decision against the organization's own risk assessment rather than defaulting to whatever hardware feels most convenient to deploy. A high-traffic general office entrance genuinely prioritizes speed and reliability, while a data center or records room should prioritize verification assurance even at some cost to throughput speed.
This device-selection discipline is a recurring theme across effective corporate security programs — the technology choice should follow from the risk assessment, not precede it, since defaulting to convenience-driven hardware selection across every zone often means under-securing the areas that actually warrant stronger protection.
Reporting Access Control Metrics to Leadership
A mature corporate security management function doesn't just operate access control — it reports on it. Regular metrics worth tracking and presenting to leadership include the number of active credentials versus current headcount, the average time to revoke access after an employee's departure, the frequency of after-hours access attempts, and any unresolved access anomalies flagged during the reporting period.
These metrics give leadership a concrete, evidence-based view of the organization's physical security posture, rather than a purely qualitative assurance that "security is handled." For security managers seeking greater organizational investment in their program, demonstrable metrics reported consistently over time are often more persuasive than any individual incident or anecdote.
Key Benefits of Access Control Solutions for Corporate Security Programs
Organizations implementing comprehensive Access Control Solutions as part of a formal corporate security management program typically report measurable improvements:
- Clear, auditable evidence of policy compliance across every secured zone
- Faster incident investigation through detailed, searchable access logs
- Reduced administrative burden through centralized credential lifecycle management
- Stronger reporting capability supporting leadership and board-level security discussions
- Consistent policy enforcement independent of individual guard shift coverage
- A defensible security posture supporting insurance and regulatory requirements
Incident Response: Where Access Control Data Becomes Genuinely Valuable
The true test of a well-managed access control system often comes during incident response, when a security manager needs to answer specific, time-sensitive questions — who accessed a particular area during a given window, whether a specific credential was used at an unexpected time, or whether an anomaly preceded a reported incident. A system generating comprehensive, searchable logs turns this from a difficult forensic exercise into a straightforward data query.
This incident response value is one of the strongest arguments for investing properly in access control governance rather than treating the system as a passive background utility — the return on that investment becomes most visible precisely when it's needed most, during an actual security event requiring fast, accurate answers.
Access Control System UAE: Compliance and Governance Considerations
Corporate security managers deploying an Access Control System UAE-wide need to align their governance framework with the country's data protection expectations, particularly around biometric data storage and retention, while also ensuring the system's audit trail meets the documentation standards expected during any regulatory or insurance review the organization might face.
For organizations with operations spanning multiple emirates, maintaining consistent security governance — the same policy standards, the same reporting cadence, the same incident response procedures — across every location strengthens the organization's overall security posture considerably more than allowing each site to develop its own informal approach independently.
Access Control System Dubai: Meeting the Expectations of a Sophisticated Corporate Market
Dubai's dense concentration of multinational corporate headquarters and financial institutions has raised the baseline expectation for what a credible corporate security program looks like. An Access Control System Dubai security manager implement needs to support the kind of detailed governance, reporting, and audit capability increasingly expected by clients, investors, and regulators evaluating the organization's overall risk management maturity.
For corporate security leaders operating in this environment, demonstrable investment in a properly governed access control program has become a genuine credibility factor during client due diligence and investor security reviews, not merely an internal operational concern.
Implementing Access Control as a Security Management Program
Rolling out access control as part of a formal corporate security management function generally follows a more deliberate, policy-first process than a purely technical hardware installation.
1. Risk assessment and policy design: mapping every zone to an appropriate access tier before selecting any hardware.
2. Governance framework definition: establishing approval workflows, review cadence, and reporting standards.
3. Hardware and software selection: choosing technology that supports the pre-defined policy rather than dictating it.
4. Deployment and staff training: implementing the system alongside clear communication of the underlying policy.
5. Ongoing governance and reporting: establishing regular metrics review and policy refinement as the organization evolves.
Treating access control as an ongoing management program rather than a one-time installation project is what allows the system to keep delivering security value years after the initial deployment, rather than gradually drifting out of alignment with the organization's actual risk profile.
Integrating Access Control into the Broader Corporate Security Program
Access control delivers the most strategic value when integrated with the rest of a corporate security program rather than managed as a standalone system. Linking access data with visitor management, surveillance, and incident reporting tools gives security managers a unified view of physical security across the organization, rather than needing to manually correlate data from disconnected systems during an investigation.
This is where Tektronix's access control platform stands out for UAE corporate security teams — the system is built to integrate with visitor management, surveillance, and broader security infrastructure under one centralized reporting environment, supporting the kind of unified security management program that mature corporate security functions require.
What Security Managers Should Look for in an Access Control Partner
Corporate security leaders evaluating vendors should prioritize reporting and governance capability alongside hardware reliability, since the management layer is what ultimately determines whether the system supports a genuine security program or merely functions as expensive door hardware. Demonstrated experience supporting formal corporate security functions, rather than purely small-business or residential deployments, is a meaningful differentiator worth confirming.
Vendor responsiveness during an actual security incident — not just routine support tickets — should also factor into the evaluation, since access control data often becomes most critical during exactly the high-pressure moments when a vendor's genuine support quality is tested.
Why UAE Corporate Security Teams Trust Tektronix
Tektronix has supported corporate security management functions across offices, healthcare facilities, and industrial sites throughout the UAE, giving the team direct, hands-on experience with the governance, reporting, and incident response demands that mature security programs require. Every deployment is supported end-to-end, from initial policy and risk assessment through installation, staff training, and ongoing governance support.
For corporate security leaders across Dubai, Abu Dhabi, and the wider Emirates evaluating access control solutions built for corporate security programs, this experience translates into a platform that supports genuine security management practice, not just door hardware installed without the governance framework behind it.
Conclusion
Access Control System technology anchors a mature corporate security management program. Biometric Access Control Dubai teams trust protects the highest-risk zones, while a risk-tiered Security Access Control System, auditable Door Access Control, and efficient Mobile Access Control support ongoing governance. The right Access Control Device and complete Access Control Solutions drive demand for Access Control System UAE and Access Control System Dubai corporate security programs.
Frequently Asked Questions
1. How is access control different from a broader corporate security management program?
Access control is the enforcement technology; a security management program is the policy, governance, and reporting framework that determines how that technology is configured, monitored, and used to support organizational risk decisions.
2. What metrics should corporate security managers track from their access control system?
Useful metrics include active credentials versus current headcount, average credential revocation time after departure, after-hours access frequency, and any unresolved access anomalies from the reporting period.
3. Why does policy design need to happen before choosing access control hardware?
Selecting hardware first often means the technology's default configuration dictates security policy by omission, rather than the organization's actual risk assessment driving deliberate zone-by-zone access decisions.
4. How does access control data support incident investigation?
Detailed, searchable access logs let security managers quickly answer specific questions during an investigation, such as who accessed a given area during a particular time window.
5. How long does it take to implement access control as part of a formal security management program?
Timelines depend on the complexity of the risk assessment and governance framework being established, but most organizations complete policy design, hardware deployment, and staff training within a few weeks.










Sign in to leave a comment.